
Intelligence
Built to an uncompromising standard, exposing hostile intent, anticipating the next move, and outmaneuvering the most capable nation state adversaries by turning raw noise into advantage long before they strike.
Cyber Threat Intelligence, Entrepreneur, Presentation Virtuoso
Hello and こんにちは!
I am Scott Jarkoff (ジャーカフ スコット),
a threat intelligence and cyber security professional, entrepreneur, visionary leader, presentation virtuoso, cyclist, tech geek, and wannabe iPhone photographer living and working in the heart of Tokyo, Japan.
a powerhouse on-stage speaker, delivering electrifying and profoundly impactful keynotes that captivate, challenge, and inspire.
a remarkably creative presenter featuring incredible visuals combined with striking insights on cyber threat actors, their evolving tradecraft, and the attacks defining modern cyber warfare. I illuminate the future of generative AI in offensive operations, the shifting cyber security landscape, and the critical thought leadership shaping the next era of digital conflict.
I write about cyber security, sophisticated cyber adversaries, global cyber attacks, threat intelligence, the eCrime ecosystem and the dark web economy, leadership, global and domestic travel, hiking trips in Japan, and occasionally post various photos taken with an iPhone and meager composition skills.
I am the ambitious co-founder and mastermind behind deviantART, the largest and most vibrant online art community the world has ever seen, launched on August 7, 2000.
I am orchestrating the inception of Praeryx, a new cyber threat intelligence startup currently in deep development.
the quiet architect of jark after dark, a nocturnal pursuit of the uncomfortable questions hiding behind polished narratives, built for those who suspect the official story is never the whole one.

Finally, I live in Tokyo, Japan, where I architect and oversee these mission critical operations.
Reach out to me for inquiries.
Three decades across government and industry have forged a rare command of cyber security and threat intelligence. My experience spans technology and code, entrepreneurship, and the global stage. I have written software, scoured security logs, administered firewalls, and architected defense-grade systems. I have built companies, led exceptional teams, and directed regional intelligence strategy. I translate complex cyber realities into language understood from the engineering floor to the boardroom and the halls of government. In today’s sophisticated threat landscape, the ability to decode chaos into clarity and transform understanding into decisive action is not optional. It is imperative.
Built to an uncompromising standard, exposing hostile intent, anticipating the next move, and outmaneuvering the most capable nation state adversaries by turning raw noise into advantage long before they strike.
Exceeding expectations is only the baseline. I build and lead elite teams where innovation thrives, collaboration becomes a force multiplier, and elegant solutions achieve what others consider impossible.
Co-founder of deviantART and Praeryx, developing and building ambitious ventures, challenging established industries, and transforming revolutionary ideas into platforms, companies, and global communities with lasting impact.
Electrifying keynotes and commanding panel conversations exposing the forces reshaping cyber conflict, shattering conventional thinking, and leaving audiences with a radically clearer view of what comes next.
The modern threat landscape no longer respects borders, industries, or operational domains. Nation state adversaries pursue strategic advantage through espionage and disruption. eCrime operations industrialize intrusion for profit. Hacktivists weaponize access, narrative, and attention. Artificial intelligence compresses timelines and expands reach. Understanding each force in isolation is no longer enough. The real advantage comes from seeing how they converge.
State sponsored operations pursue long-term strategic advantage through espionage, intellectual property theft, surveillance, disruption, and influence. Campaigns target governments, defense, technology, critical infrastructure, and the institutions shaping geopolitical power.
Financially motivated adversaries operate an industrialized ecosystem of ransomware, extortion, access brokers, fraud, underground markets, and cryptocurrency laundering. Specialization turns compromise into profit with global reach, speed, and ruthless efficiency.
Ideologically motivated actors use disruption, data leaks, defacement, and influence operations to seize attention and apply pressure. Activity intensifies during geopolitical crises, where activism, coercion, opportunism, and state interests increasingly overlap.
Artificial intelligence is accelerating reconnaissance, social engineering, vulnerability research, malware development, and influence operations. It lowers cost, expands reach, and compresses the time between intent and impact, giving capable adversaries a powerful force multiplier.

Binance explained how North Korea stole US$6.34 billion, and the explanation is worse than the silence it replaced. A fake job interview, a poisoned coding assignment, the exchange’s own AI tooling, and an Ethereum delegation feature let PRESSURE CHOLLIMA drain wallets after withdrawals were frozen.

By the time Japan Airlines told 92,000 customers their data was taken, the break-in was more than three years old. It was not the airline, but inside Amadeus, the provider running reservations for more than 130 airlines globally. This incident reached at least five carriers before anyone noticed.

Binance explained how North Korea stole US$6.34 billion, and the explanation is worse than the silence it replaced. A fake job interview, a poisoned coding assignment, the exchange’s own AI tooling, and an Ethereum delegation feature let PRESSURE CHOLLIMA drain wallets after withdrawals were frozen.
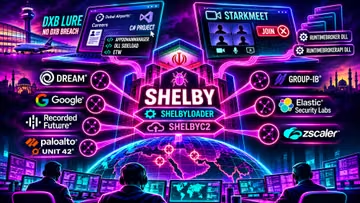
A fake job from Dubai Airports, a video app that never works, and a gigabyte gone from a Kurdish government cloud. One Iran-nexus espionage operation carries seven vendor names, runs its command-and-control through GitHub, and keeps collecting in the gap between what the industry can see and prove.

Chainalysis identifies the people moving through the blockchain. A breach of its own systems reversed the lens, exposing identity data on the investigators, regulators, and compliance staff who track crypto crime. The firm calls the data non-sensitive and has not explained how the attacker got in.

A former NSA director tells Japan to move faster, and the firm paying him sells the cure. Nihon Cyber Defence calls MIJXDR a fully sovereign, Made in Japan platform, then localizes it into Ukraine. Here, sovereignty is a label bought with public money, and the architecture is nowhere in sight.

The FBI has formally named North Korea for the US$6.3 billion Binance theft, the largest in history, confirming an attribution the tradecraft already pointed to. One question is answered. How the attacker turned Binance’s own signing systems against it is not.

NIST built ML-KEM to protect the world’s data from a future quantum computer. North Korea’s Lazarus found an advantage in the present, running the same post-quantum mathematics inside operational malware before most enterprises have migrated. The standard did not fail. It worked for the wrong side.

North Korea stole US$6.3 billion from Binance in roughly twenty minutes, the largest cryptocurrency theft in history. No private key had to leak. The attacker seized the machinery turning Binance’s intent into valid signatures, and ten blockchains moved as one.

For years, the surveillance state called metadata harmless. Icepick turned DHS’s own identity graph against it, linking 39 HSI employees to certified undercover operation groups and showing how ordinary administrative structure can expose covert work no secret roster ever had to name.

Airbnb charges like a hotel and then hands you the cleaning. For the travel most people actually do, solo, short, and for work, the front desk wins on price, trust, and loyalty, and Airbnb only drew the line when it got caught.
Free. Open access. Independent daily cyber security analysis, available to everyone.
Standard. Complete access. Every written analysis, every member-only deep dive, and the full archive.
Premium intelligence. Formal cyber threat intelligence reporting, downloadable data, and practical training.
Co-Founder
2024-Current
Director, Threat Intelligence Strategy, APJ & META
2019-2024
Senior Security Advisor
2013-2019
Chief, Cyber Security
2008-2013
Senior Systems Engineer
2005-2008
Co-Founder
2000-2005
Security Operations Center Supervisor
2000-2005
Telecommunications & Cyber Security
1990-1999