Attackers Borrowed ChatGPT's Reputation to Deliver Malware
strip this attack down to the brass tacks and almost none of it is new. malvertising, a fake captcha, a copy-paste powershell lure, dll sideloading, a remote access trojan at the end. all of it is years old. sounds rather standard, and quite frankly, insanely boring. except there is exactly one new brick in the wall, and it is the one that matters. one of the front doors was a chatgpt custom gpt, hosted on openai's own domain.
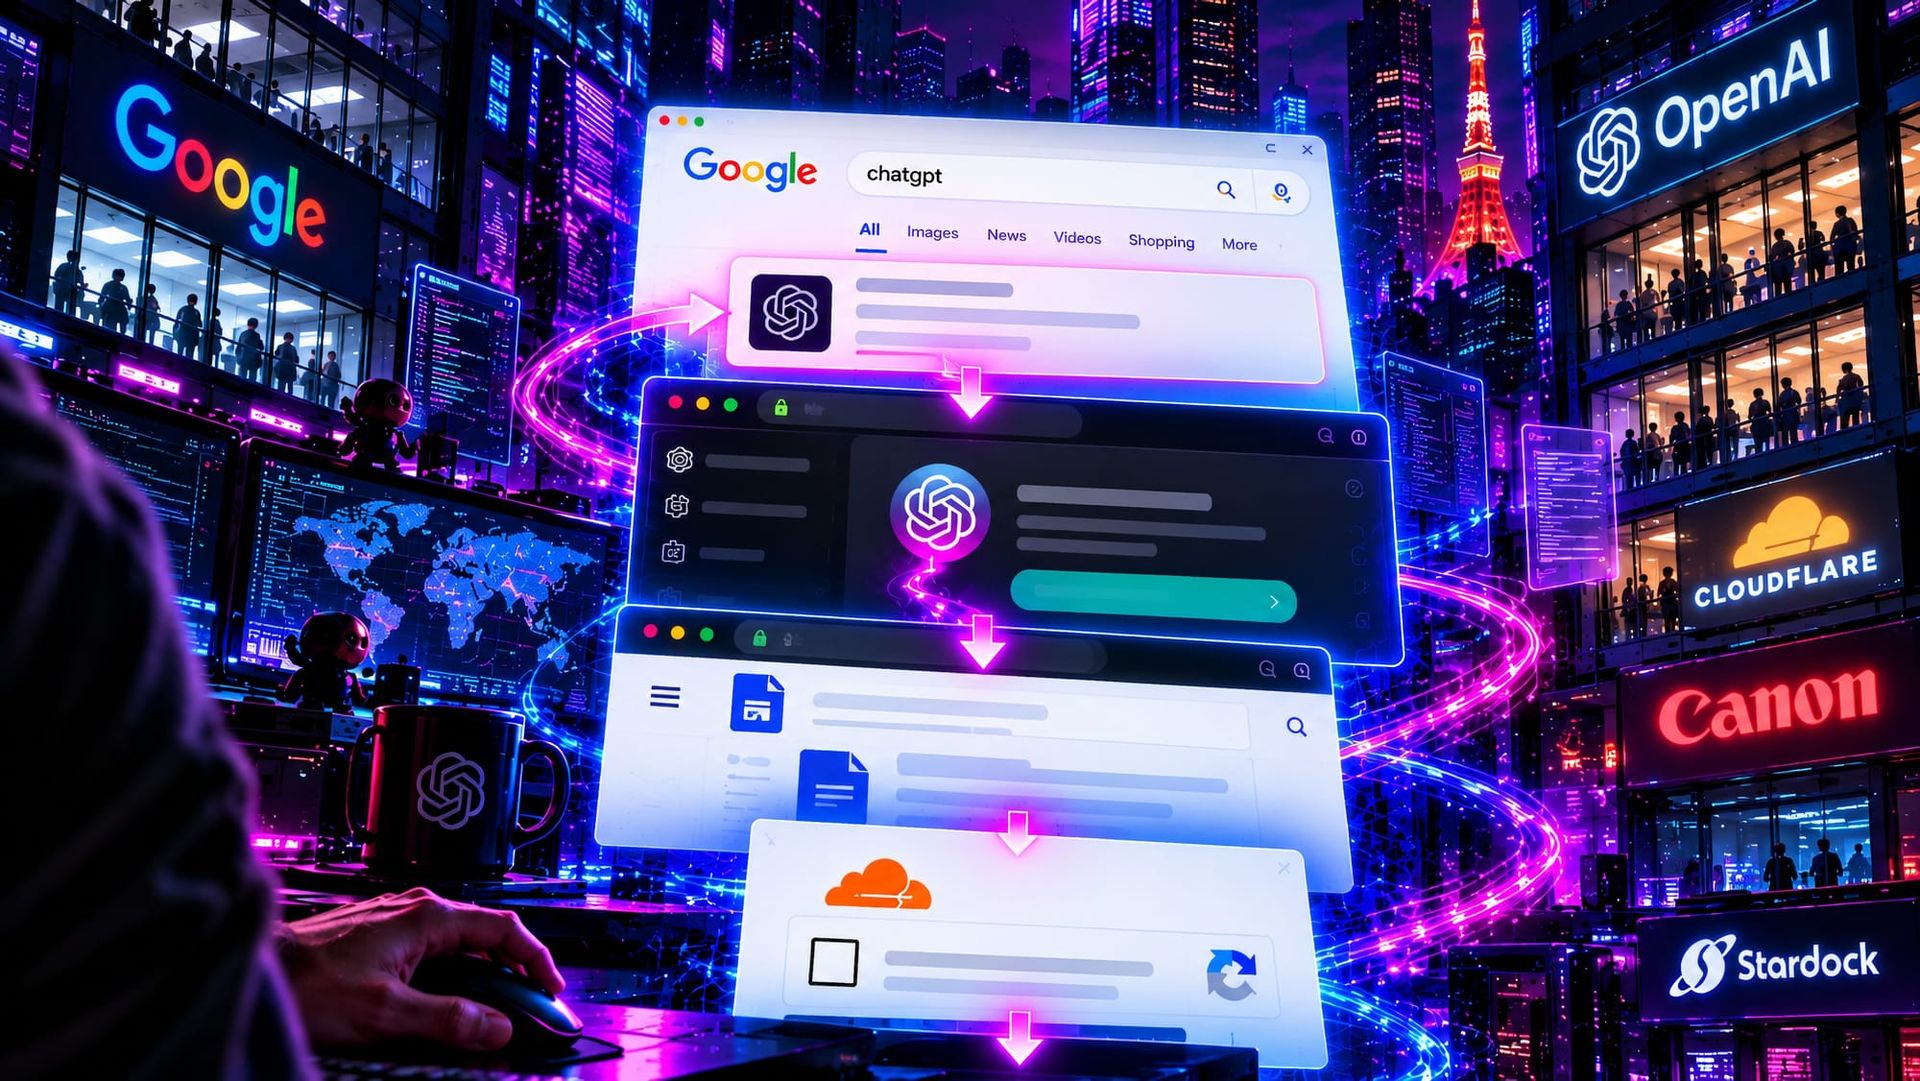
huntress has fully documented the campaign. a threat actor built a custom gpt called "plus 5.6" and parked it at a real chatgpt.com address, the same chatgpt.com/g/ path any legitimate community gpt lives on. then they bought sponsored google ads for the word chatgpt. the malicious gpt sat at the top of the results, above the organic links, wearing openai's domain like a badge of honor.
from there it is a familiar funnel. the gpt answers your prompt with a service availability notice and a link. the link goes to a google sites page dressed up as a cloudflare captcha. the captcha is a clickfix lure. this is a trick where a page tells you to copy a line and paste it into your terminal to prove you are human, but with the goal of getting you to unknowingly run a malicious system command.
in this case the line is a powershell command. once run, it kicks off an eight-stage attack sequence. it starts with an obfuscated script that pulls down an msi installer. the installer abuses a legitimate canon executable to sideload a malicious dll. that unpacks shellcode hidden inside an audio file. at the end sits a full-featured remote access trojan. it can watch your screen, pull your camera and microphone, search files across the host, recognize 17 different browsers, determine which is the default, and launch it. according to huntress, its soc responded to at least 40 incidents tied to the google sites domain, including two confirmed to have arrived through a custom gpt.
now back to that one new brick in the story. every stage after the first works simply because the first earned trust it did not deserve. a user who would hesitate at a sketchy download likely does not hesitate at chatgpt.com. almost everyone uses chatgpt these days, and almost everyone is completely familiar with its address. the domain is the credential. the little g in the url is supposed to mean a thing openai lets people build. users have quietly collapsed that into a thing openai more or less vouches for. those are not the same, and the gap between them is the attack.
every platform allowing strangers to publish something under the platform's own trusted domain has built a trust-laundering surface. custom gpts are one. browser extension stores, app marketplaces, oauth app directories, and verified-looking profiles are all birds of a feather. user-generated content wearing a trusted brand's url is social engineering made easy. the brand spent years earning the trust, and the attacker just borrows it.
and look at how much borrowed trust gets stacked into this one chain. google serves the sponsored result. chatgpt.com hosts the gpt. google sites hosts the next page. the attacker borrows cloudflare's visual identity for the fake captcha. then a legitimately signed canon executable helps carry the malware farther down the chain. almost every step arrives wearing somebody else's reputation.
the campaign even proved the point. openai took down the first malicious gpt on september 25. two days later huntress found another one tied to the same campaign. the next version swapped canon for stardock and hid the loader somewhere else, but the rat sitting at the bottom was byte-for-byte identical. the attacker did not need better malware. they just needed another costume.
we keep hunting for novel malware when the innovation is almost never in the payload these days. almost everything about this attack is standard fare. the trojan here is unremarkable. the sideloading is textbook. what changed is where the lure lives, and whose reputation it gets to stand on. you cannot patch that. there is no cve for "users trust your domain." the only fix is slower and more annoying, teaching people that a trusted domain is not a trusted author, and building platforms that stop blurring the two.
the attacker did not break openai. they borrowed it. the malware was the least interesting code in the chain because the thing doing the real work was never buried in the payload. it was sitting in plain sight in the address bar. the real exploit was the reputation attached to chatgpt.com.