China Phished the People Who Write America's AI Rules
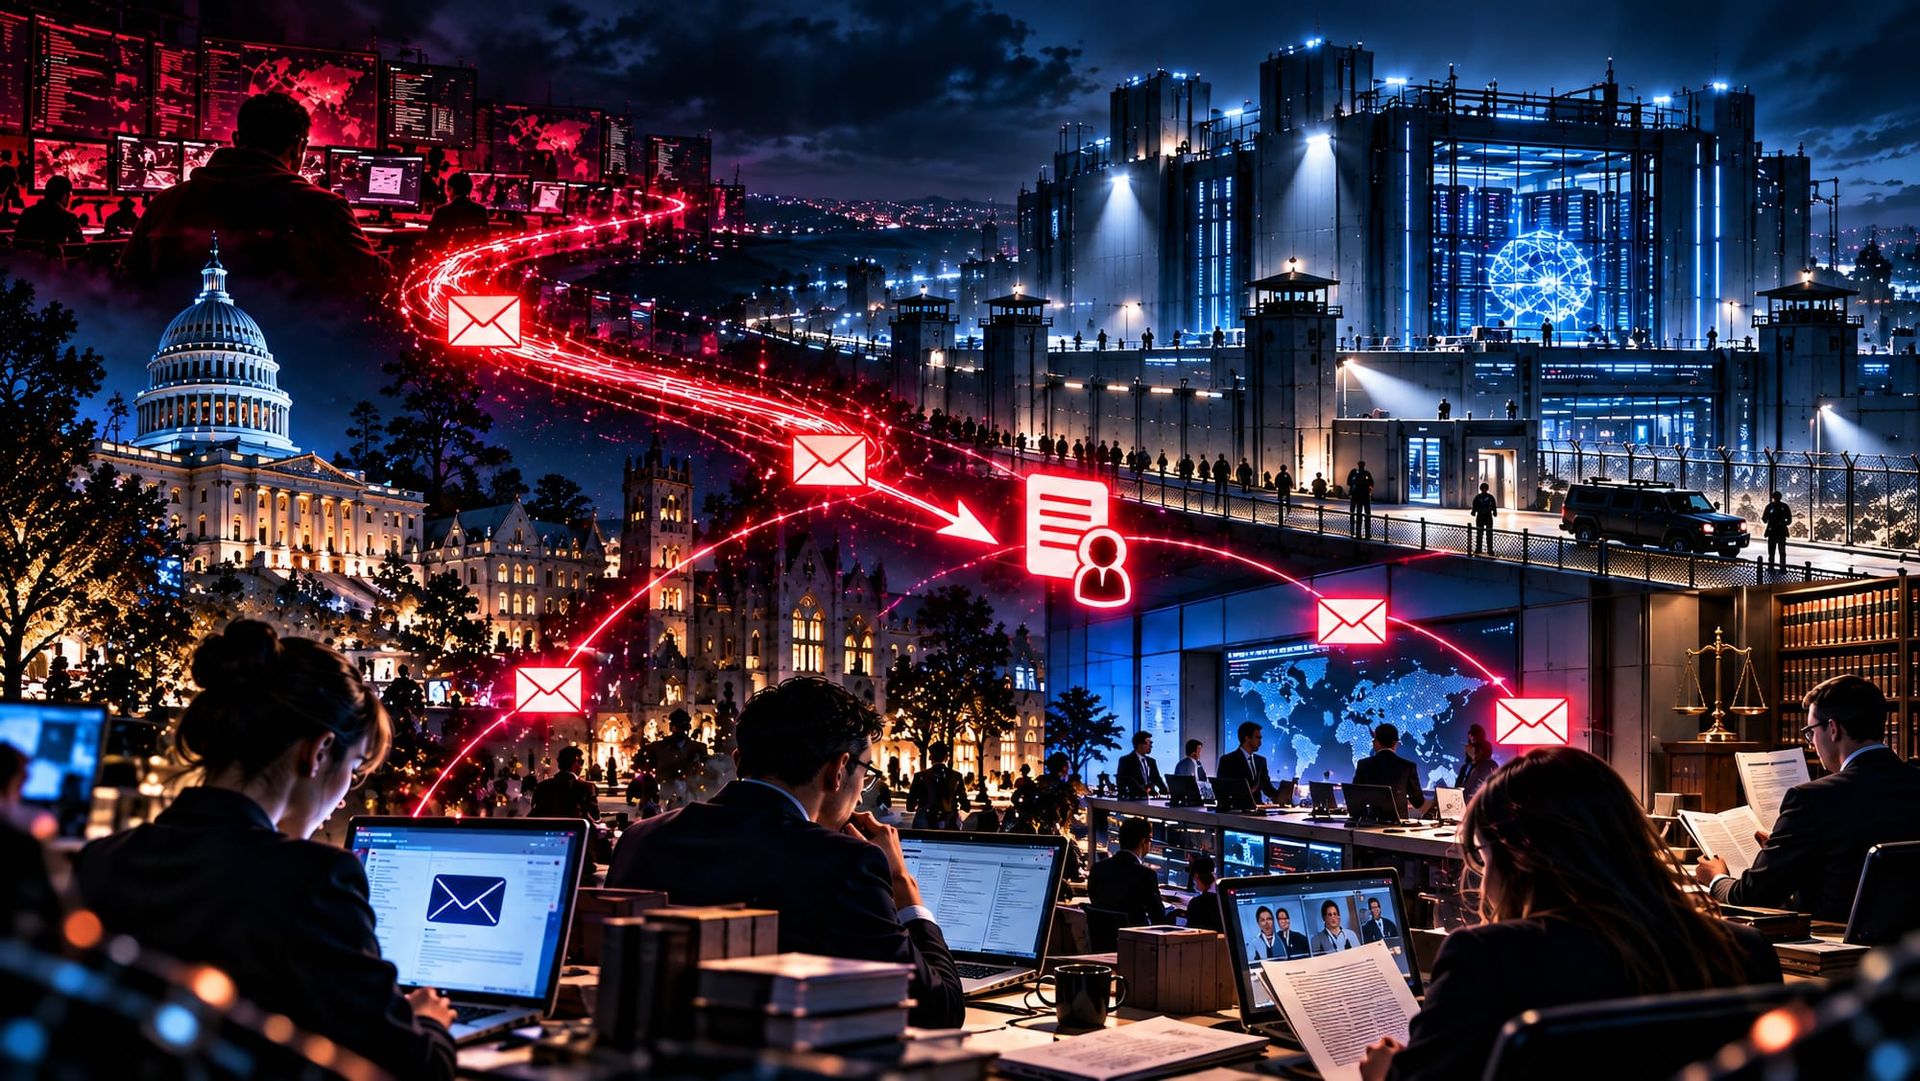
if you wanted to know where american ai policy is going next, you might assume the obvious target is one of the frontier labs. ta419 took a different route. proofpoint says the china-aligned espionage adversary targeted the people surrounding the technology instead. they went after ai policy experts at u.s. think tanks, universities, and law firms.
the people it impersonated included a former white house science official, a former state department chief economist, and a senior employee at anthropic. in this campaign, ta419 did not go after the ai labs themselves. it went after the policy brains around them, and got in by borrowing the faces those experts already trust.
the frontier labs are hard targets. they are well funded, heavily monitored, have solid cyber security controls, and know they sit near the top of every serious threat actor's targeting list. the analyst at a think tank working through export-control scenarios is a considerably softer target, and often may even be a more valuable one.
that analyst knows where u.s. policy is heading long before it becomes public. if you want to understand what the united states will actually do about ai, model distillation, and export controls, your best bet may not be breaching a lab at all. you need to get inside the conversations shaping the decisions. that is not merely theft of a secret. it is getting inside the adversary's decision loop.
for the phishing campaign, ta419 did not blast out generic spam. it opened with harmless, flattering outreach. invitations to join an advisory committee. requests to contribute to a report on ai export controls. one analyst at a u.s. think tank received an email titled "request for feedback on military integration of claude."
reuters identified another target as alex engler, who leads the penn center on media, technology, and democracy. he became suspicious and checked the outreach through people in his professional network. proofpoint told reuters the recent effort targeted fewer than 10 people across only a handful of organizations.
that small number matters. espionage does not need scale when every person on the list sits close to a decision you care about.
once a target engaged, the trap followed a modern playbook. the tradecraft used a shortened link, a cloudflare turnstile check behind a fake onedrive loading screen, then an attacker-controlled page built around a browser-in-the-browser lure and a real-time adversary-in-the-middle proxy.
the proxy relayed the genuine microsoft authentication flow, including multi-factor authentication and conditional-access checks, while capturing the password and resulting session cookie. a stolen session cookie can let the attacker reuse an already authenticated session without forcing the victim through multi-factor authentication again. the victim can see what looks like a normal successful login while the attacker walks away with access.
notice what ta419 did not do here? it did not go hunting for a zero-day in one of the bazillion microsoft products riddled with security issues. it did not breach the think tank's network. it merely borrowed a person.
the entire intrusion rode on the trust attached to a real human being's name. this is the same way other campaigns ride on a trusted domain, except here the trusted object was a person. the credential was not technical. it was social. a former white house official does not need to be involved at all for their identity to become the most effective payload in the attack chain.
proofpoint tracks ta419 as a china-nexus, espionage-motivated threat actor. its report stops short of tying the activity directly to the chinese government, although it assesses the targeting likely supports broader chinese intelligence objectives. it also did not name compromised victims or confirm whether any accounts were successfully taken over.
this is a campaign built to steal access to the u.s. ai policy conversation, caught in the act, not a confirmed breach with a body count. the specific ai campaign focused on u.s. organizations, while proofpoint says ta419 has also targeted people tied to japan-based think tanks, defense contractors, universities, and law firms since at least 2025.
the targeting itself is nothing novel. governments have gone after think tanks, academics, lawyers, former officials, and policy advisers for decades because those communities sit between classified intelligence and public policy. what is different here is how strategically important that layer has become around ai.
we defend the frontier labs like fortresses, but the policy ecosystem surrounding them has no equivalent perimeter. it is scattered across think tanks, universities, law firms, former officials, advisers, researchers, and ordinary cloud inboxes. the real perimeter around ai policy is not a firewall. it is a trust graph.
the model weights are not the only thing worth stealing. knowing what the united states intends to do about ai may be just as valuable, and the people holding pieces of that answer are considerably easier to phish than a frontier lab.
intelligence also becomes more valuable before the decision is public. who is arguing for tighter export controls, which proposal is gaining support, where the internal disagreement sits, and which people actually influence the outcome can matter months before anything reaches a press conference or the federal register. that is pre-decisional intelligence. you are not merely learning the policy. you are watching the policy form.
ta419 understood something our defensive instincts still resist. you can put the model weights behind layers of controls and lock the compute inside a fortress, but policy still gets built by people talking to other people.
the crown jewels are no longer only the technology. they are the decisions forming around it. the model tells you what america can build. the inbox tells you what america plans to do about it.