Cozy Bear Taught an AI to Rebuild Its Malware Every Time Its Detected
the security industry stopped primarily relying on signature-based detection alone years ago. static indicators, file hashes, specific binaries, were always trivial for any attacker to change. detection moved to behavior. the how of an attack rather than the what. behavior is more expensive to fake. that shift, indicators of attack over indicators of compromise, is the ground modern defense stands on.
russia's cozy bear just used ai to go after what is left of the old model.
anthropic disclosed a russian state operation it tracks as gtg-20006, with tradecraft and targeting consistent with cozy bear. russian svr.
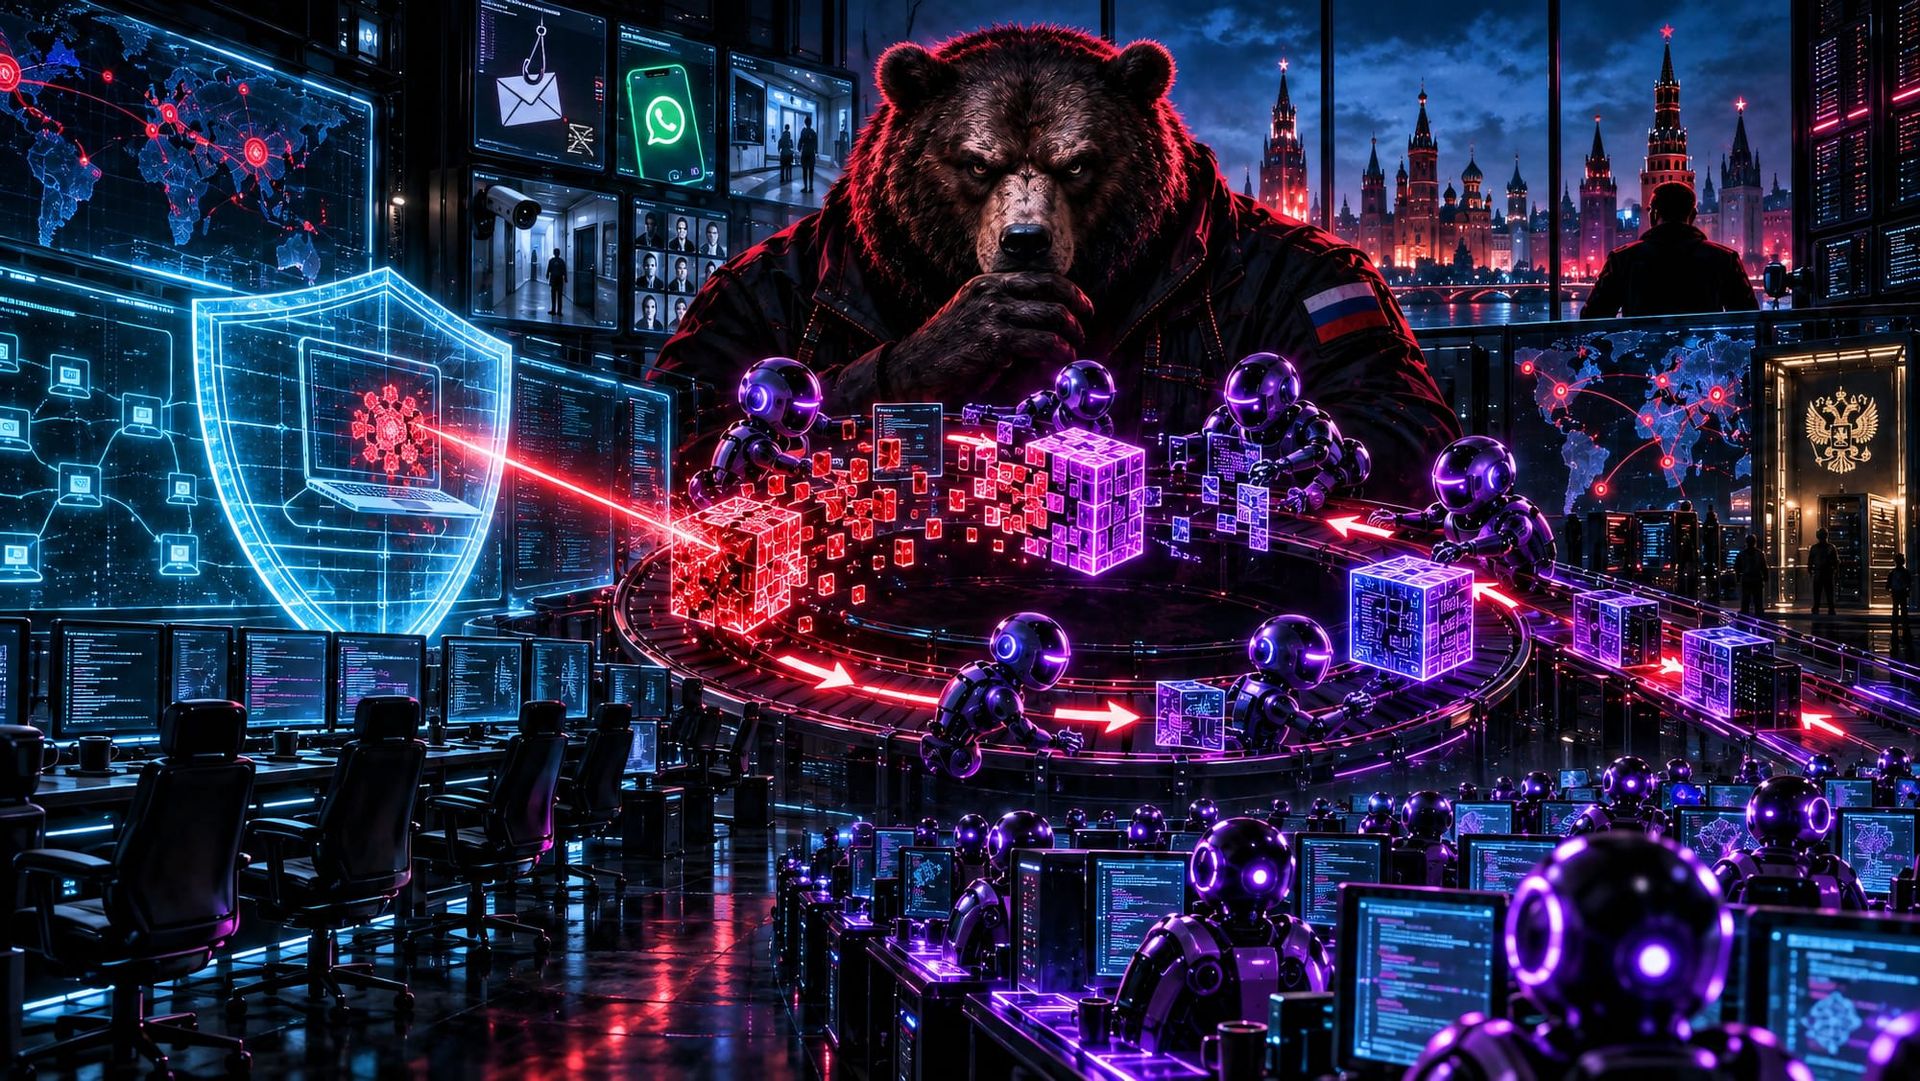
cozy bear built ai agents to watch their own malware in the wild. the second a security product detects it, the agents rebuild it on the spot. automatically. over and over, modifying and recompiling until nothing flags it anymore, then redeploying it. the human barely touches a thing.
the logic of static-indicator detection rests on one assumption. that when you catch a piece of malware, the attacker has to do real work to make a new variant. that small amount of work, and the window it offered, was your leverage. you imposed a cost, and the cost slowed them down.
cozy bear has now automated the rebuild, so the cost is mere seconds of compute. you detect the static artifact, and before a signature can be engineered, the ai has already shipped a version that indicator will not catch. detection at the artifact layer is not the end of the fight anymore. it is the trigger for the next variant.
this hits the static-indicator layer hard, but the tradecraft underneath still has to execute. the phishing, the dns hijacking, the click-fix lures still look like something, which is exactly why behavioral detection matters more now, not less.
the same operation used ai to research and register phishing domains, stand up the hosting, send the emails, and watch the command channels for hits. it hijacked whatsapp accounts by linking them as companion devices and quietly bulk-exported ukrainian and russian conversations while hiding the read receipts.
it even went after surveillance cameras by finding authorization flaws in camera-streaming services. it then harvested the tokens to watch victims' live feeds. one operation stole an entire national identity database, 300,000 records, plus the commercial registry for half a million companies. all of it targeting ukrainian and european governments, defense, and diplomacy.
ai has collapsed the gap that used to separate a well-funded state operation from a lone operator. that is the part defenders should care about most. the techniques are not getting magically more exotic. intense labor is merely disappearing. reconnaissance, exploit development, infrastructure, data processing, all the expensive human work surrounding the attack is being compressed into compute.
what cozy bear did here is not really all that novel. it is a simple, modern, effective workflow. and a workflow can be copied. the self-rebuilding-malware trick that a russian intelligence service just ran is the kind of thing that trickles down to the ecrime ecosystem within days, weeks, or at worst, months. just as every other capability has moved from nation state to ecrime.
it is worth noting anthropic caught this and disrupted it. they published the details, which is the argument for the labs that actually report abuse of their own tools rather than burying it.
the same class of ai that people use for ordinary work can be pointed at a defender and told, keep changing until they cannot see you, and it will do exactly that.
yesterday, detection bought defenders time. today, detection may seemingly become a feedback signal teaching an automated attacker what to change next to strengthen their detection evasion techniques.