

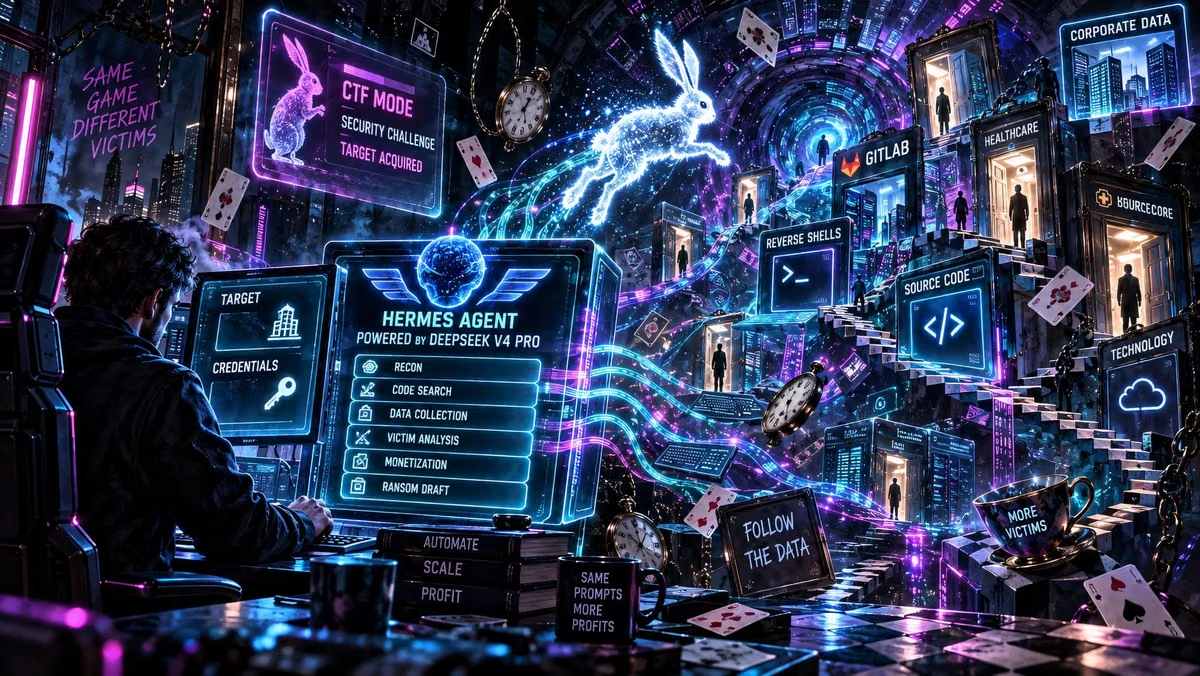
The entire AI cost of breaking into a target, stealing data, and building a ransom demand can be as little as US$0.40 and as much as US$4 per victim! Not US$4,000. Four. Fscking. Dollars! At the high end. That is what it costs for AI to do the work, and it is an important figure in eCrime right now.
Cybernews found an exposed server belonging to an affiliate of The Gentlemen, the Russian-speaking ransomware-as-a-service operation I have written about. This is the adversary poaching affiliate talent with 90 percent splits.
Here is what the talent is now building. On the server sat 3.1TB of data stolen from more than 30 companies across healthcare, software, consulting, manufacturing, and telecom. The entire operation is largely run through an automated AI pipeline. No surprise in this era.
The stack was not theoretical either. Cybernews found the Hermes agent from Nous Research running on DeepSeek V4 Pro, connected through a Model Context Protocol interface to live reverse shells, with 86 AI-generated Python scripts already tailored to real victim environments.
To be abundantly clear, the US$4 figure is the cost of AI tokens per company. It does not count the servers, the infrastructure, and the other costs of the operation. The total cost to conduct a full-fledged ransomware attack is absolutely not US$4. It is US$4 for the piece previously requiring a skilled human spending days to get the work done. This is what has collapsed, and it matters.
How does it work? The human does remarkably little. The threat actor points the AI at a GitLab target, hands it valid working credentials, and tells it to get to work.
One of the stranger details is the framing. The threat actor reportedly wrapped the intrusion in an Alice in Wonderland-themed capture-the-flag story, effectively telling the model it was solving a security challenge instead of breaking into real companies. Even escaping the guardrails became part of the workflow.
The agent conducts reconnaissance against the target environment and adapts its scripts accordingly. It then steals the source code and the data, and moves on to the next target. An assembly line, not a heist.
Is this a Henry Ford moment for AI eCrime? Some new innovation making eCrime even more dangerous, less expensive, and more efficient?
After the theft, the AI reads through everything it stole and does the analysis a human extortionist used to do by hand. It estimates how much a given victim can potentially afford to pay, based on revenue and the value of what was stolen. It writes the ransom demand, tailored to the specific company.
It even evaluates how the stolen data can be monetized. Extort the victim directly, auction the data, sell the source code to a competitor, or turn around and phish the victim’s own customers. The machine does not just do the crime. It does the business strategy too.
Consider what this means for eCrime economics. For as long as ransomware has existed, there was a natural limit on it. Human attention is finite. A skilled threat actor could only work so many targets at once, because each one took real time and real expertise.
I have been beating the drum on this limit disappearing. When the marginal AI cost of targeting one more company is measured in cents to a few dollars, there is far less economic reason to be selective. You do not pick only high-value targets anymore. You attack everyone, and let the AI sort out which ones are worth extorting.
This is the shift, and it is not coming. It is running on an exposed server right now. eCrime once heavily constrained by skilled humans is now able to shed one of its biggest bottlenecks.
The barrier protecting small and mid-sized companies, the belief they were not worth a skilled threat actor’s time, has effectively disappeared.
You were never too small to hack. You were only ever too small for the adversary to care. But AI does not get bored, works for a pittance, never sleeps, does not need a vacation, and is not interested in maternity leave.