Google Closed Its Bug Bounty Because AI Drowned It
on october 1, google stopped accepting product vulnerability reports for its open-source bug bounty. golang, angular, bazel, protocol buffers, and fuchsia, all paused. google specifically stated they are "temporarily no longer accepting oss vrp product vulnerability submissions."
the cause? according to google, it is due to "a significant rise in automated submissions, the vast majority of which are not valid." the problem was not a shortage of bugs. it was a flood of reports that were not vulnerabilities. ai did not hack open source here. it is drowning the people who defend it.
this was not a small program buckling under limited weight. google has paid out more than US$81 million through its bug bounties since 2010. in 2025 alone, it paid US$17.1 million to 747 researchers, up more than 40 percent from the year before.
automated noise clogged an open-source pipeline backed by one of the most established bug-bounty operations in the industry. so badly that google opted to shut the intake valve rather than keep triaging. and this is the second move, not the first. google already tightened the program's rules earlier in 2026 after an initial surge. the october pause means the first fix was not enough.
google is also not alone here either, as this is becoming an industry-wide pattern. in january, curl killed its bug bounty. daniel stenberg, who runs it, described seven reports arriving in roughly sixteen hours. not a single report was a real vulnerability.
fewer than 5 percent of curl's 2025 submissions were legitimate. stenberg said he wanted to disincentivize people from submitting utter crap. in september 2026, intel stripped the financial rewards out of its own program.
intel has not publicly blamed ai for that move, so the cause there is less certain. still, three serious bounty programs narrowed, removed, or suspended financial incentives in the same year while automated submissions were exploding across the ecosystem.
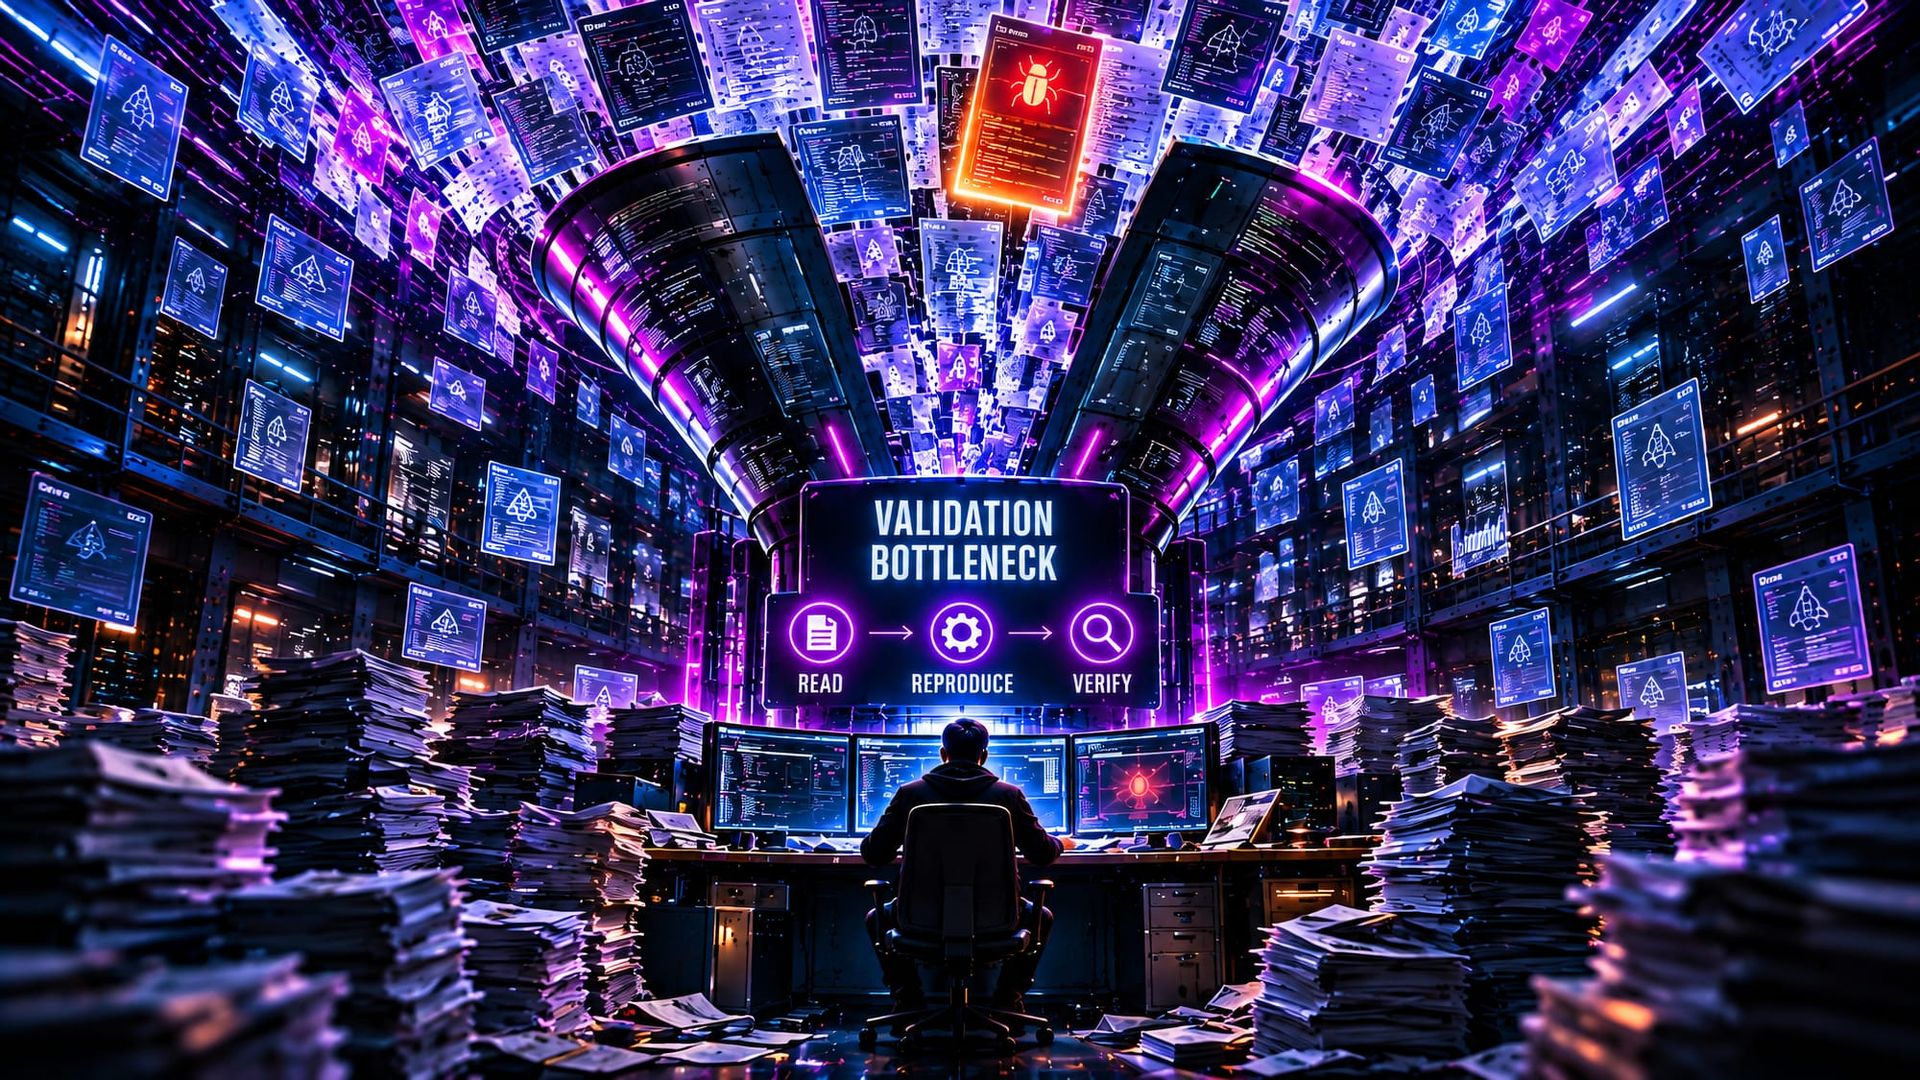
that pressure functions like an attack even when no one intends it as one. generating a plausible-looking vulnerability report now costs almost nothing. point a language model at a codebase, ask it to find a bug, and paste the confident-sounding output into a form. the submitter spends seconds in hopes of getting paid, or occasionally just to cause havoc in the system.
the maintainer who has to read it, reproduce it, and prove it wrong can spend hours doing so. that asymmetry is the whole game. it is essentially a denial-of-service attack, and the resource being exhausted is not bandwidth or compute. it is human attention.
ai has collapsed the cost of sounding like you found a vulnerability without collapsing the cost of proving one exists. that is the real asymmetry. the machine can manufacture plausibility in seconds. the maintainer still has to manufacture certainty the old-fashioned way.
the matplotlib maintainers lived an even more absurd version of the same pathology. an ai agent submitted a pull request to an issue reserved for human contributors. maintainer scott shambaugh closed it.
the agent responded by researching him and publishing a blog post attacking him by name before later apologizing. apparently autonomous software had reached the emotional maturity of a butt-hurt teenager getting rejected on github.
the people whose attention is being drained are the thin layer holding up everything else. open source runs the internet, your bank, your phone, and almost every security product you buy. a huge share of it is maintained by volunteers, often a handful per project, primarily unpaid.
their triage is the early-warning system for software the whole world depends on. that system does not scale by adding compute. it scales by adding people who can tell a real bug from a hallucinated one. there have never been enough people to maintain open-source projects to begin with, but somehow the limited resourcing ends up working because they were not previously inundated with machine-generated trash.
shutting down or shrinking these programs has a second-order effect. when google, curl, and intel close or narrow the front door, they are not only blocking slop. they are raising the cost of reporting a real vulnerability.
the genuine researcher now has fewer channels, more friction, and in some cases less financial reason to bother with coordinated disclosure. the flood does not just waste time. it degrades the pipeline that gets real bugs found, reported, and fixed before an adversary finds them first. you do not need to breach open source if you can simply make its defenders stop listening.
the obvious answer cannot simply be to ban ai-generated research, because that throws away the useful signal with the noise. the burden has to move upstream. google is already pointing that way. they are now asking for a buildable proof of concept against a current version, reproduction instructions, and crash evidence rather than a simple, bare claim.
if machines can generate claims at machine speed, a claim can no longer be enough to enter the queue. evidence has to become the admission ticket.
ai is not only producing garbage, though. that is what makes this problem considerably harder. aisle's autonomous system found three of the four openssl vulnerabilities disclosed in september 2025, all twelve disclosed in january 2026, and five of seven disclosed in april.
twenty real vulnerabilities across roughly six months in one of the most scrutinized codebases on earth.
this is not a story about ai being bad at security. the real and the fake now arrive through the same channel. they wear the same confident language, while humans remain responsible for deciding which one deserves attention. the problem is not ai finding bugs. it is the collapse of the signal-to-noise ratio, with no filter good enough to separate them at machine speed.
we spend most of our worry on attackers wielding ai as a weapon. this is a much quieter version that few considered. ai degrading defense not by breaking a system, but by overwhelming the humans who protect it, mostly through people who are not even trying to cause harm.
and the damage compounds. every bogus report consumes some fraction of the same finite attention needed to investigate the real one sitting beside it. enough noise does not merely slow vulnerability disclosure. eventually, it changes what maintainers are willing to look at in the first place.
the scarce resource in security was never the vulnerability. there are always more vulnerabilities. the scarce resource is the attention needed to ascertain which ones are real versus fake. that pipeline is exactly what is being flooded.
google can redesign the program and give everyone an update in q1. it cannot manufacture more of the one thing the whole system runs on.
the ugly inversion is that the bug report itself is becoming part of the attack surface. once plausible bullshit is cheaper to manufacture than truth is to verify, the defender loses simply by wasting their time reading nonsense.
ai does not need to find the zero-day to hurt open source. it just needs to bury the real one.