Your Biggest Data Leak Is an Employee Being Helpful
according to data check point published in its august 2026 cyber threat landscape report, ransomware has nearly doubled this year. the most interesting number in the report is not about threat actors. it is about a company's own employees, and what they are pasting into chatbots like claude, chatgpt, grok, and more.
let's start with the attacks, because the trend is ugly and clear. organizations faced an average of 2,422 cyber attacks per week in august, up 22% year-over-year. ransomware hit 1,042 attacks for the month, close to double where it was this time in 2025. phishing crept up too. now roughly 1 in every 112 emails is out to get you. the external threat is not slowing down. it is relentlessly compounding.
check point also tracks how enterprises use generative ai, and the finding is easy to misread. 86% of organizations regularly using genai were hit by high-risk prompt activity. that may sound like an attack statistic, but it is not.
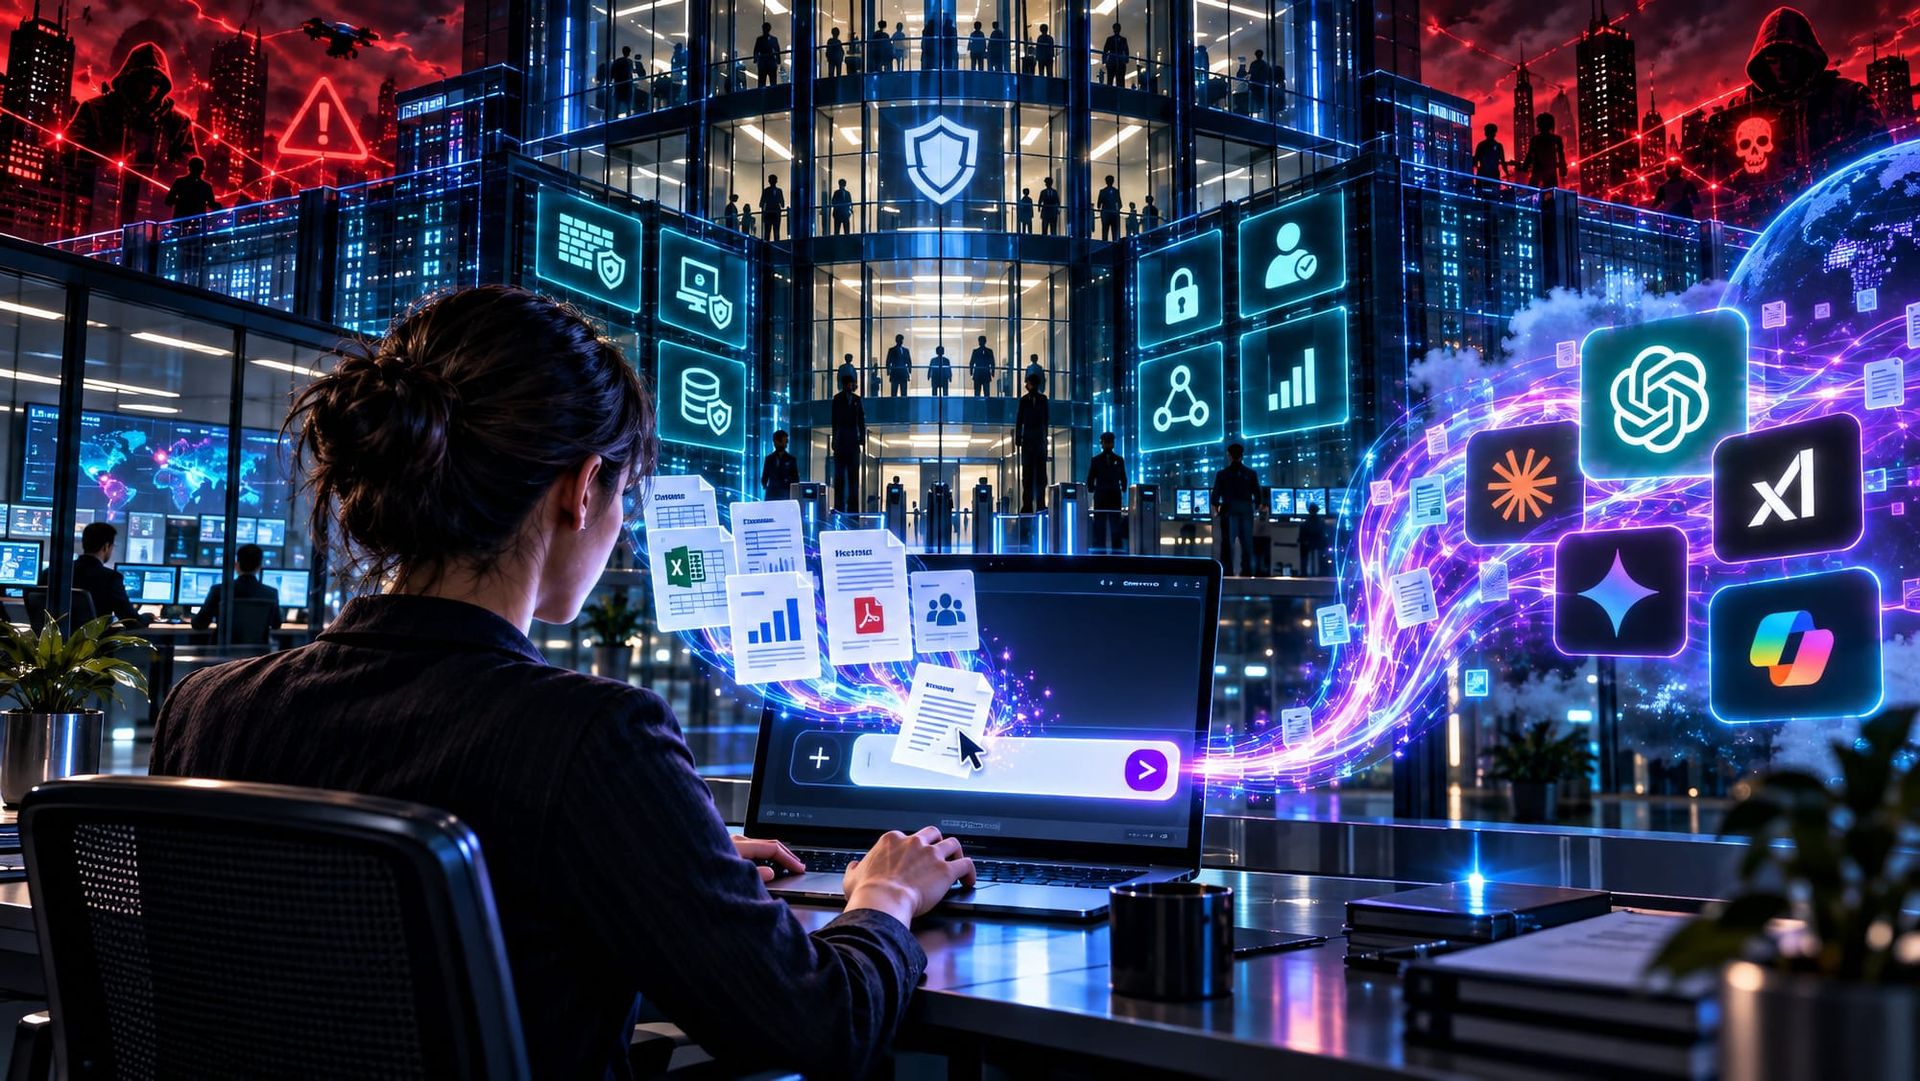
the risk here is not attackers using ai, and it is not flaws in the models. it is what employees are actively typing into the prompt. sensitive customer records. confidential financial data. confidential legal documents. infrastructure details. hr files. check point saw network and it infrastructure data in 67% of affected organizations, financial data in 65%, legal and regulatory material in 64%, hr data in 59%, and pii in 57%. all copied straight into third-party ai tools sitting outside the company's traditional security boundary.
the counterintuitive part of this is the rate of risky prompts actually fell in august. it is the lowest in months, 1 in 43. so people are getting slightly more careful per prompt. but the exposure still spread to 86% of ai-using organizations. why? because usage exploded.
the average user generated 106 prompts in august, up from 78 in june, across an average of seven different ai tools per company. the per-prompt risk dropped, and the total risk went up anyway. there is simply so much more prompting happening. people are being slightly more careful per prompt, but they are prompting far more often, which adds up to more exposure.
everyone is watching the ransomware number climb, and they should because it is treacherously high. but one of the fastest-growing ways sensitive corporate data leaves the building right now is not a hacker breaking in and exfiltrating documents. it is an employee trying to be helpful. someone pastes a contract into a chatbot to summarize it. maybe they drop a customer list in it to clean it up. that data is now sitting in a third party's system, outside every control the company spent money to build.
and it does not feel like a breach, which is exactly why it is dangerous. a ransomware attack announces itself. inadvertently malicious ai use leaves no alarm, no ransom note, no incident to respond to. just a slow, invisible drip of the company's most sensitive material into tools nobody is monitoring, one helpful prompt at a time. the healthcare sector is worst, with 1 in every 25 prompts carrying sensitive data. think about what "sensitive" means in healthcare.
one honest note on the source. this is check point's data, and check point sells prevention. the framing naturally points toward buying more of their security tooling. the numbers are credible and they match what others are seeing. just exercise some critical thinking skills, and read any vendor's threat report knowing it doubles as a sales pitch.
the takeaway is not to ban the tools. that ship sailed, and in any event the productivity is real. it is that most companies deployed generative ai to their whole workforce before they built a single rule about what could go into it.
the attack surface everyone is watching is the network. the one quietly leaking the most right now is the text box.
companies spent decades building walls around their data. then they put a blinking cursor inside those walls and invited every employee to carry pieces of the company through it.
the new exfiltration channel has a send button.