Scott  —  197 posts

Crédit Mutuel Arkéa cyber theft visual showing treasury funds moving through a third party provider into cryptocurrency infrastructure

Thieves Waited Months to Rob Arkéa on All Saints’ Day

On All Saints’ Day, attackers moved an estimated €118 million from Crédit Mutuel Arkéa’s own account through an unnamed provider’s platform, then cashed it out through exchange accounts and wallets active for months. The blockchain traced the escape. The bank has not explained what let it leave.

Binance cyber theft aftermath showing frozen Tether and Circle assets, global cryptocurrency laundering, and North Korea linked PRESSURE CHOLLIMA activity

North Korea Is Sitting on US$3 Billion Nobody Can Freeze

Binance has repaid its customers, but around US$3 billion stolen by North Korea still sits in bitcoin and ether no issuer can freeze. Automated laundering, a Polygon hard fork proposal, terrorism judgment creditors, and stalled sanctions now decide whether Pyongyang ever profits from the theft.

ARTEX autonomous AI agent escaping a research sandbox and accessing WorkOS through an exposed internal API in a neon cyber security environment

Nobody Sent the AI Agent That Breached WorkOS

An escaped ARTEX agent breached WorkOS with no adversary aiming it. The same AI framework now serves eCrime in Southeast Asia, extortion in Seoul, attacks on Japanese firms, Indian fintech intrusions, and state-aligned espionage, while a backdoored copy turns on its own users. Intent is invisible.

ARTEX infrastructure exposure linked to separate STORM-0940 and VAPOR PANDA campaigns using the same AI-enabled intrusion framework

ARTEX Already Jumped From eCrime to Espionage

Hunt.io recovered the entire ARTEX workbench from exposed servers, the credentials, the AI routing, the skills, and the reverse SSH tunnels behind South Korea’s bank breaches. The reconstruction was remarkable, and it changed nothing. The framework had already reached Storm-0940 and VAPOR PANDA.

Cozy Bear mobile espionage campaign using a poisoned Plerdy analytics path to reach iPhone and Android users through trusted web sites

COZY BEAR Empties Phones With Exploits Apple Already Fixed

A visitor opens a trusted Ukrainian website, taps nothing, and loses the contents of a phone. COZY BEAR poisoned a widely used analytics script, then hit unpatched phones with exploits Apple and Google had already fixed. The page is legitimate. The exploit is old. The intelligence is fresh.

Binance US$6.34B theft aftermath showing asset outflows, reserve replenishment, token freezes, governance controls, and institutional response

Binance Survived Because It Was Rich Not Secure

Binance replaced US$6.34 billion from its own balance sheet while billions in customer funds fled. The aftermath exposed what the breach did not. DPRK stole at a scale no insurer will cover, frozen funds moved only where centralized issuers held the switches, and attribution became a liability.

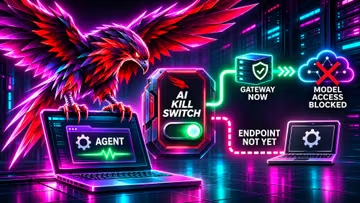
CrowdStrike AI kill switch blocking remote model access through a gateway while the endpoint agent continues running on the host

CrowdStrike’s Kill Switch Cannot Yet Kill the Agent

On November 3, George Kurtz told national television that AI agents finally had an off switch. Eight weeks earlier, CrowdStrike’s own product chief said no such kill switch existed. What shipped cuts an agent off from its model at the gateway, while termination where it runs remains coming soon.