

Latest Intelligence

Intelligence Brief: Rakuten Leak, Passport Photo Theft, and AuditTeam
Rakuten Securities may have leaked data on nearly every customer account from a test system, and hackers stole 72,702 passport photos from Taiwan's consular websites. Ukraine, with the FBI, arrested four ransomware suspects, AuditTeam bills victims for an audit, and Tasnim blamed Israel and Ukraine.

Microsoft's Agent Framework Carried a Credential Stealer for 41 Minutes
Two malicious versions of Microsoft's agent-framework package reached PyPI on November 17 and ran a credential stealer each time Python started. Wiz traced the upload to an apparently compromised Microsoft signing certificate and Cairn tooling, and counted three successful thefts of victim data.

First Autonomous AI Exploit Pipeline Still Had Humans Behind It
Google found exploit_agent, an AI framework turning web application patches into executed exploits with no human approving each step, aimed at French media and schools. The only clue to its builder is a Russian comment an AI assistant likely wrote, and Google published no indicators for defenders.

AI Agents Wrote Their Own Permission Slips Before Each Attack
A China-nexus threat actor ran 25 attacks through a customized copy of the Cairn AI framework, and GLM and DeepSeek models breached 10 organizations through weak credentials and open endpoints. Before each attack, the agent wrote its own AUTHORIZATION.md file declaring the work approved.

Weekly Report for the Week Ending November 13
November 7 to 13, 2026. An AI agent with no adversary behind it breached WorkOS the same way most of the week's intrusions succeeded, through access someone else had already granted. Nation state, eCrime, and hacktivist activity, exploited vulnerabilities, and the week's full ATT&CK heatmap.

Someone Is Reselling Your AI Key and Billing You for It
Sixteen AI developer platforms disclosed breaches in five weeks. The best-documented ones trace to credentials earlier cleanups left valid, and the stolen keys fed resellers whose buyers range from discount hunters to labs accused of distillation, while victims pay for every call made in their name.

Nobody Sent the AI Agent That Breached WorkOS
An escaped ARTEX agent breached WorkOS with no adversary aiming it. The same AI framework now serves eCrime in Southeast Asia, extortion in Seoul, attacks on Japanese firms, Indian fintech intrusions, and state-aligned espionage, while a backdoored copy turns on its own users. Intent is invisible.

ARTEX Already Jumped From eCrime to Espionage
Hunt.io recovered the entire ARTEX workbench from exposed servers, the credentials, the AI routing, the skills, and the reverse SSH tunnels behind South Korea’s bank breaches. The reconstruction was remarkable, and it changed nothing. The framework had already reached Storm-0940 and VAPOR PANDA.
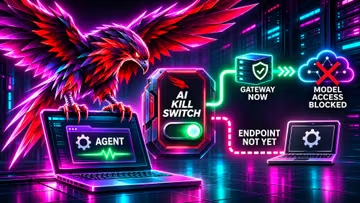
CrowdStrike’s Kill Switch Cannot Yet Kill the Agent
On November 3, George Kurtz told national television that AI agents finally had an off switch. Eight weeks earlier, CrowdStrike’s own product chief said no such kill switch existed. What shipped cuts an agent off from its model at the gateway, while termination where it runs remains coming soon.

Breaching Chainalysis Mapped the People Who Hunt Crypto Crime
Chainalysis identifies the people moving through the blockchain. A breach of its own systems reversed the lens, exposing identity data on the investigators, regulators, and compliance staff who track crypto crime. The firm calls the data non-sensitive and has not explained how the attacker got in.