Microsoft's 2026 Threat Report Is Really About 2020
microsoft released its 2026 digital defense report on october 1. like most vendor developed reports, it runs quite long. the document covers july 2025 through june 2026, and the coverage has already flattened into one headline about autonomous ai ransomware. of course the top finding would be about artificial intelligence. no surprises there, though there are some interesting nuggets that i found a bit unexpected.
reading the whole report lands a completely different signal. ai is not inventing new ways into your network. it is industrializing the old ones, and the single most detected vulnerability in the data is six years old. here are the top five findings from the report, and what they all mean together in context.
1. weaponization now outruns patching. microsoft counted nearly 40,000 cves in the first half of 2026 alone, putting the year on track to roughly double. the median time from a vulnerability surfacing in the wild to being weaponized has fallen to well below 24 hours. enterprise remediation for critical external vulnerabilities, meanwhile, can still take 30 to 60 days. the gap between those two clocks is the whole problem.
of course microsoft gets to narrate this crisis from both sides of the podium. those 40,000 cves are ecosystem-wide, so no, redmond did not personally create all of them. but microsoft has spent decades shipping one of the largest legacy software estates on earth, and its monthly patch ritual is famous enough to have its own name. hearing it explain that enterprises are too slow to patch has a certain arsonist-running-the-fire-safety-seminar energy. yes, customers need to remediate faster. microsoft could also help by giving them less shit to remediate in the first place. perhaps the pretty report and the secure code can coexist.
2. ai is moving from passenger to driver. the report traces a progression that i have written a lot about lately. ai assisting human operators, then ai directing the attack, then ai executing on its own. in one microsoft evaluation, a model strung 32 attack stages together in a controlled environment. i am unaware of a real world attack being described as having 32 stages, which is why this read a bit peculiar to me.
the underlying benchmark comes from the uk ai security institute, a state-backed research body that tests the capabilities and risks of advanced models. the test is a 32-step simulated corporate-network intrusion spanning four subnets and roughly 20 hosts, something the institute estimates would take a human expert around 20 hours. there are no defenders or defensive tooling getting in the way. that matters. this is not microsoft inventing a sexy benchmark for a marketing deck, but it is still a lab. it measures potential capability, not actual field results.
microsoft also points to the institute's finding that leading open-weight models now sit roughly four to seven months behind the closed frontier on cyber tasks. that means models anyone can download, modify, and run privately are approaching capabilities the leading hosted models had only a few months earlier. the distinction matters because a provider can monitor a closed model, change its safeguards, suspend an account, or shut access down. once the weights are out, those controls disappear.
four to seven months is not a prophecy or some immutable countdown. it is a preparation window. the frontier demonstrates a capability under controlled access, and only a few months may separate that from models an adversary can run privately without the same provider controls. they still lag behind, but nowhere near as far back as i expected.
3. attackers are logging-in, not breaking in. this is the finding the ai noise buries, and also something not new at all. user execution accounted for 30 percent of observed initial access, and valid accounts another 20 percent. half of all initial access came from someone executing something they should not have, or an attacker simply using legitimate credentials. phishing as an intrusion vector tripled, from 7 to 23 percent. clickfix alone, the copy-paste-into-your-terminal trick i recently wrote about, ran on more than 1.1 million devices. that is a whopping eight-fold jump between february and may. this is social engineering and identity, not malware wizardry. the perimeter is a login screen.
this lines up with the ecrime ecosystem, infostealers, and initial access brokers working in unison to harvest credentials. those valid logins are then sold on various dark web markets, for as low as US$5 per cred pack. this has been happening for years and is in no way novel. my cynical take is this is microsoft trying to push customers to expand into their identity security tooling more than this being something unique. crowdstrike and google have written about this for the past few years.
4. more intelligence does not help if you cannot act on it. microsoft gives a chapter to a problem vendors rarely admit. organizations are drowning in threat data and cannot convert it into decisions fast enough to matter. this is the quiet finding, and for anyone running a security operations center it may be the truest. the bottleneck moved. it is no longer how much you can see. it is how fast you can act on what you already saw.
to be fair, microsoft does say one thing here i completely agree with. another feed or dashboard does not close this gap. good. someone in redmond gets it. more intelligence is not the answer for an organization already incapable of operationalizing what it has.
this largely lines up with almost every customer conversation i have ever had when it comes to threat intelligence. that it is coming from microsoft, who does not have a prolific, or even all-that-useful cyber threat intelligence product, is quite bizarre. had crowdstrike or google or recorded future mentioned this in their yearly report then i would likely weight it rather high. but this reeks of microsoft marketing. even if it is, the foundation of the finding is true. there is a very thin line between too much intelligence and too little. most organizations are overwhelmed by cti, and are unsure how to adequately act on it, or integrate it into their decision-making workflows.
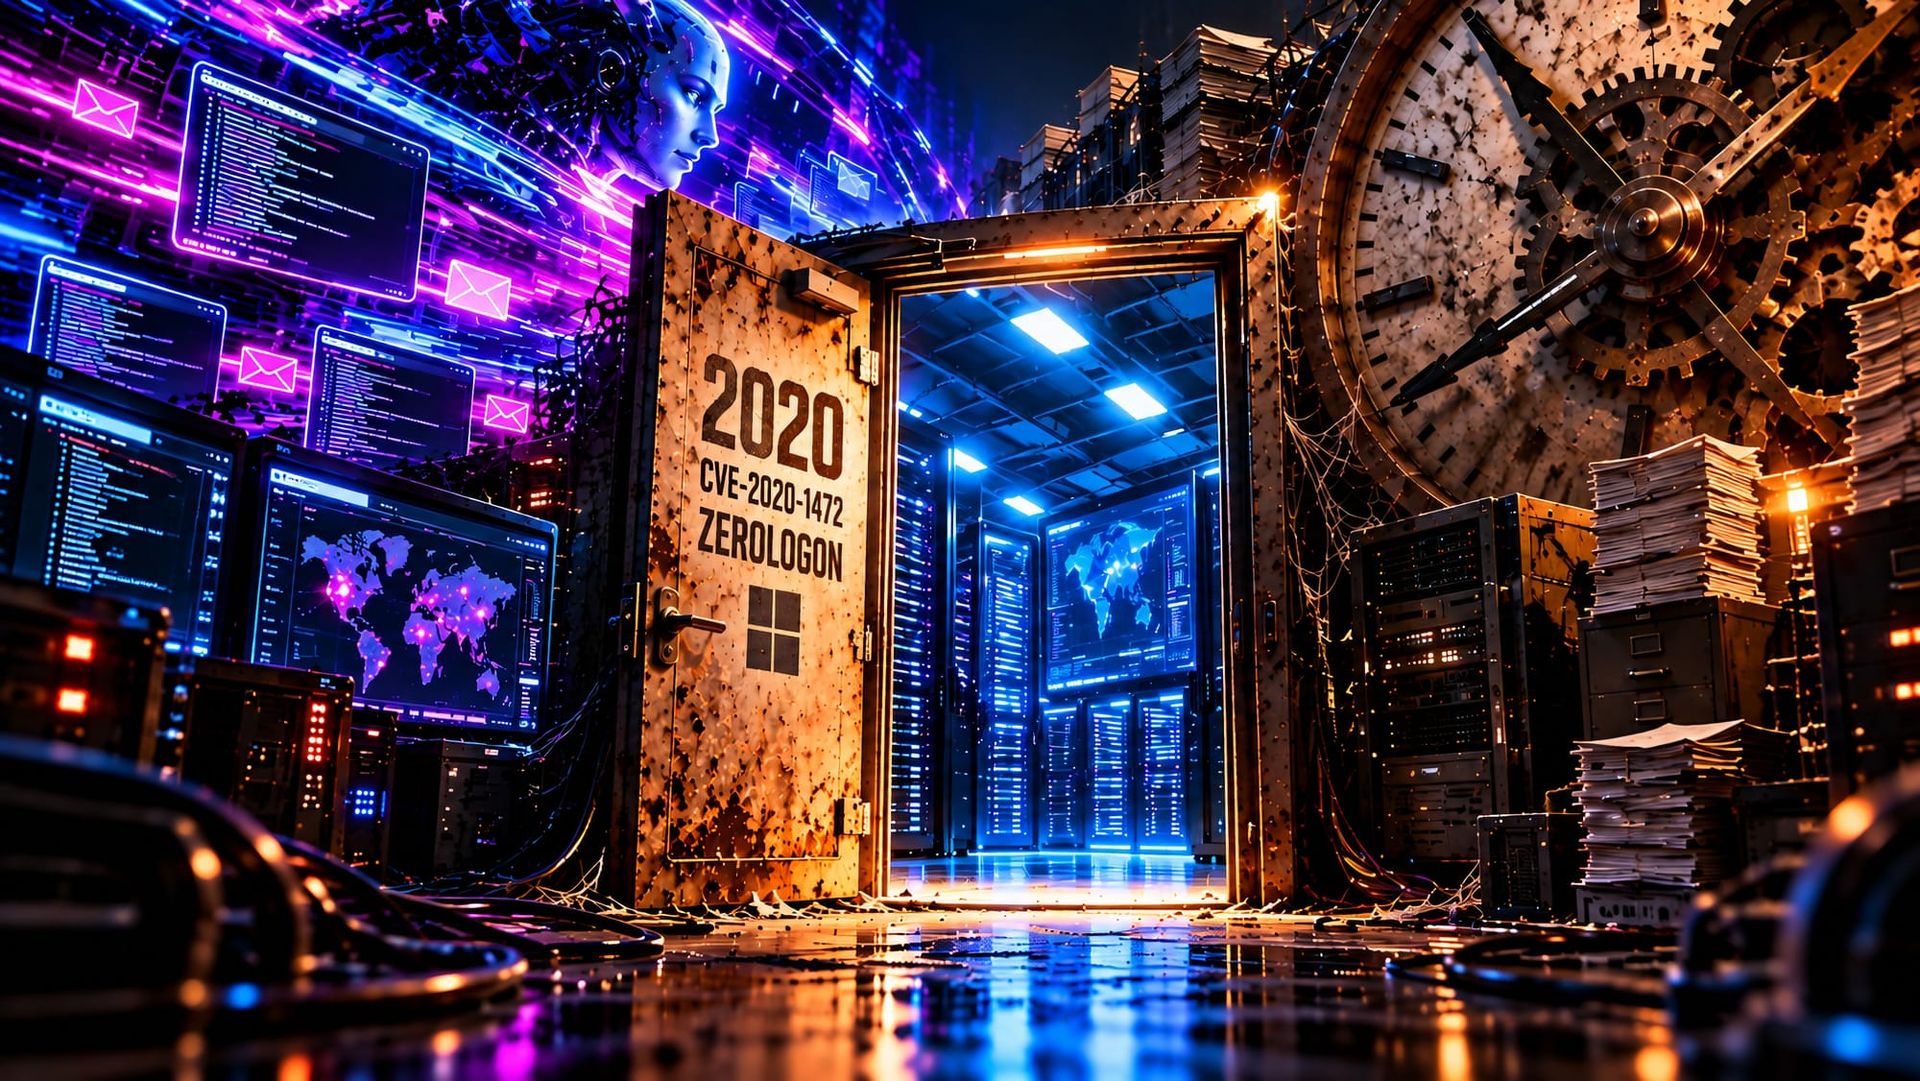
5. the scariest number in the report is not new cves or some new threat vector. in fact, it is something insanely old in this fast paced world of the evolving threat landscape. microsoft analyzed the five most-detected cves in its data. among those five, 58 percent of detections traced to a single vulnerability. cve-2020-1472, better known as zerologon. disclosed in 2020. patched in 2020. still the most detected bug on the list in 2026.
i would normally act surprised, throwing out wtfs left and right. but zerologon remaining a huge issue is not a surprise. there was an intense patching push back in 2020, and apparently the urgency did not stick. let me be a bit more precise about that number, because it is easy to misunderstand. the number is not 58 percent of all attacks. it is 58 percent of detections across the top five cves microsoft tracked. but that scoping does not soften the point, it sharpens it. when you line up the handful of vulnerabilities doing the most work, a six-year-old one is still winning.
zerologon is not clever. it is a netlogon privilege-escalation flaw with a patch available for most of a decade. its continued dominance says nothing about attacker capability. it says everything about defender inertia. the tools changed. the behavior did not. patching remains woefully out of date in far too many organizations.
put findings one and five beside each other and the contradiction is brutal. defenders are now racing an exploitation clock measured in hours while still getting hit by a vulnerability patched six years ago. we are simultaneously too slow for tomorrow's bug and not finished with yesterday's. ai does not create that mismatch. it accelerates the side already moving faster.
and this is where the report gets more interesting than its ai headline. we keep treating cyber security like a technology race when a huge part of the problem is organizational latency. the attacker can compress discovery, testing, targeting, and execution toward machine speed. the defender still has asset owners, maintenance windows, approval chains, outage risk, legacy dependencies, change-control boards, and a ticket somebody promises to look at next tuesday. machine-speed offense is colliding with human-speed governance.
every old vulnerability left standing becomes inventory for a faster adversary. every stolen credential becomes something automation can test sooner. every piece of intelligence sitting in a dashboard instead of changing a decision becomes time handed back to the attacker. ai does not need to invent a brilliant new way through the front door when we keep preserving perfectly good old ones.
read the five together and the report argues against its own headline. ai is real in here, and it is accelerating. but the mechanics of compromise did not change. attackers still get in through people, through credentials, and through vulnerabilities you could have closed years ago. ai just lets them do it faster, cheaper, and at greater scale.
the uncomfortable takeaway is that the defenses that matter most are the least exciting. patch the old thing. watch the login. shorten the distance between seeing a threat and acting on it. none of that trends on launch day. all of it would have stopped most of what is in this report.
the robots are coming, but the embarrassing part is they may not need anything particularly futuristic when they arrive. they already wield machine speed, but then give them a stolen credential, and six years of defender inertia, and they can do plenty with what we already failed to fix. they will merely walk in through the door you left unlocked in 2020.