Scott  —  197 posts

Pressure Chollima attack on Binance visualized through a fake job interview, compromised developer access, EIP 7702, and the US$6.34B theft

Binance Explained Its Record Heist and the Answer Is Worse

Binance explained how North Korea stole US$6.34 billion, and the explanation is worse than the silence it replaced. A fake job interview, a poisoned coding assignment, the exchange’s own AI tooling, and an Ethereum delegation feature let PRESSURE CHOLLIMA drain wallets after withdrawals were frozen.

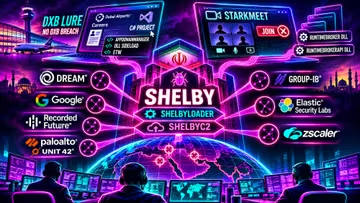
DarkBlinders espionage campaign using fake recruitment and StarkMeet lures, Shelby malware, GitHub C2, and seven security vendor tracking views

DarkBlinders Shows Why Threat Actor Naming is a Hall of Mirrors

A fake job from Dubai Airports, a video app that never works, and a gigabyte gone from a Kurdish government cloud. One Iran-nexus espionage operation carries seven vendor names, runs its command-and-control through GitHub, and keeps collecting in the gap between what the industry can see and prove.

Chainalysis cyber security investigation platform showing a protected intelligence core surrounded by exposed customer identity data and professional user networks

Breaching Chainalysis Mapped the People Who Hunt Crypto Crime

Chainalysis identifies the people moving through the blockchain. A breach of its own systems reversed the lens, exposing identity data on the investigators, regulators, and compliance staff who track crypto crime. The firm calls the data non-sensitive and has not explained how the attacker got in.

Japan cyber sovereignty concept showing MIJXDR wrapped in Sovereign branding, institutional leadership, investment flows, and hidden infrastructure dependencies

Nihon Cyber Defence Is Selling Japan the Idea of Sovereignty

A former NSA director tells Japan to move faster, and the firm paying him sells the cure. Nihon Cyber Defence calls MIJXDR a fully sovereign, Made in Japan platform, then localizes it into Ukraine. Here, sovereignty is a label bought with public money, and the architecture is nowhere in sight.

DHS identity directory search for CUC revealing a mission graph linking 41K+ records, 55K+ access groups, and 39 HSI profiles

Metadata Unmasked the Undercover Agents

For years, the surveillance state called metadata harmless. Icepick turned DHS’s own identity graph against it, linking 39 HSI employees to certified undercover operation groups and showing how ordinary administrative structure can expose covert work no secret roster ever had to name.