Scott  —  197 posts

Your ATM Was Encrypted, Until It Was Not

A researcher found nine ways to strip the encryption off some ATMs, including a fail state mounting the disk in plaintext. The flaws are patched. The unsettling part is where else this software hides, buried in products across banking, healthcare, and government, which may never learn it was broken.

McKesson Was Breached by a Phone Call, Not a Zero-Day

ShinyHunters claims it stole 284 million patient records from McKesson, which moves a third of North America's prescriptions. Read the number carefully. Records, not patients. McKesson confirmed a breach, not the figure, and the data now sits behind a log-in a convincing voice on the phone can open.

PLUMP SPIDER Makes the Bank Rob Itself

Most financial eCrime is theft. PLUMP SPIDER does something worse. The Brazil-based adversary gets inside a bank's own software and pushes fraudulent transfers through the real payment rails, in a real customer's name, so the fraud looks exactly like a legitimate transaction to every control.

You Never Chose the Company Leaking Your Face

More than 153 million driver's license records are allegedly for sale on the dark web for US$100, traced to an identity verification vendor most victims never heard of. You cannot change your face or your date of birth. And lawmakers want to make this exact model mandatory for using the internet.

Your Car Got Hacked Because It Is a Computer Nobody Was Watching

The first known malware built for car dashboards did not go after your brakes. It hijacked the update app, turned the head unit into a proxy botnet node, and rented out your car's internet connection for ad fraud. The car was never the point. The always-online, unwatched computer inside it was.

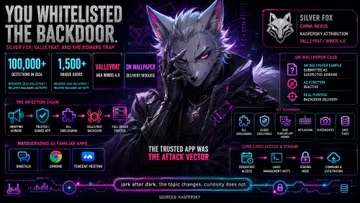
You Whitelisted the Malware Yourself

The China-nexus threat actor Silver Fox hid a full-control backdoor inside a real Chinese wallpaper app, the kind of harmless adware nobody takes seriously. That is exactly why it worked. The disguise was so convincing the ads never even ran, and the missing ads were the tell giving it away.

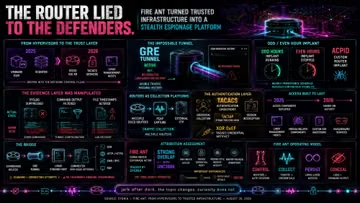
Most Dangerous Intrusions Quietly Turn the Alarms Off

Most threat actors try not to get caught. Fire Ant breaks in, then disables the cameras and edits the tapes. The China-nexus adversary turned Cisco routers into spying platforms, suppressed the logs, and altered what administrators were even allowed to see on their own devices. The logs lied.

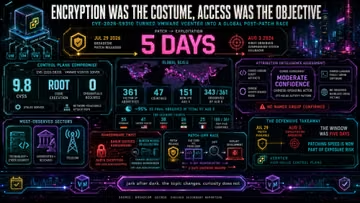
Encryption Was the Costume, Access Was the Objective

A critical VMware vCenter flaw was patched on July 29. Five days later, a suspected China-nexus threat actor was already inside, across 361 IPs in 47 countries. It ended in ransomware, but QUIRSO says it was likely a smokescreen. The encryption was the costume. The access was the objective.