Your Ransomware Negotiator Might Be Working Both Sides
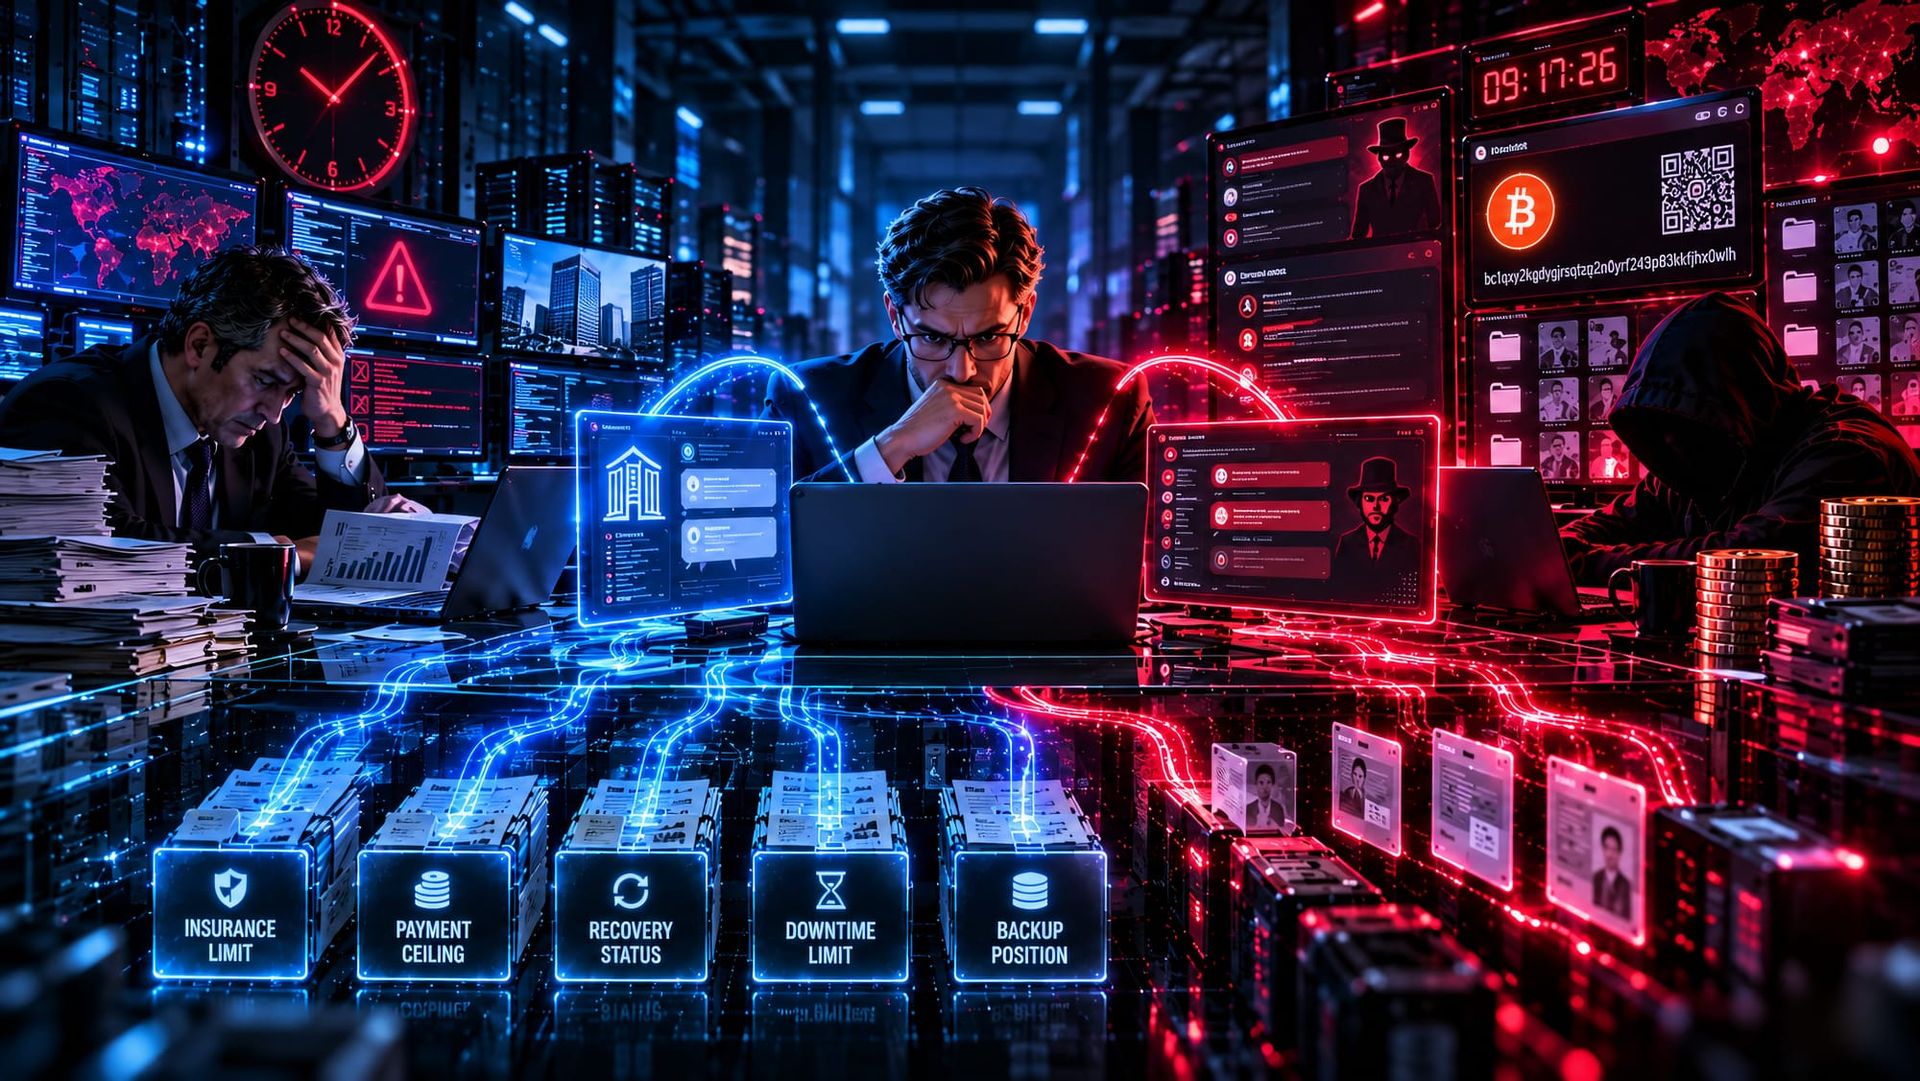
the ransomware negotiation business runs on a single promise. when an organization is having the worst week of its corporate life, locked out of its own systems and staring at a countdown, the negotiator is the one party in the room allegedly with no stake in the outcome beyond getting the client through the distress. that neutrality is supposed to be the entire product. this month the fbi arrested a man whose case, if the allegations hold, describes the exact failure the model was built to prevent.
edward dubrovsky, a 54-year-old canadian cyber security executive, was arrested by the fbi and charged with threatening to disclose stolen data and with interfering with interstate commerce through extortion. he was a managing partner and chief operating officer at the incident response firm cypfer. prosecutors have asked he remain in custody pending trial and the records stay sealed. cypfer, which has not been accused of wrongdoing, says it learned of the arrest from the media. the company is apparently unaware of it being a target, and that its business does not include making or facilitating ransomware payments. nothing yet has been proven. at this point these are allegations.
the headlines have fused two things the reporting has kept separate. investigators reportedly believe an executive at a large us consulting firm played an active role in running an extortion dedicated leak site called shinywire. the site was live from early may until the middle of october, and listed close to one hundred victims. that executive has not been named and has not been charged.
dubrovsky is not that executive, and the reporting does not say he ran the site. one name so far, but attached to a different set of allegations.
it is the allegations that matter because of the role he held. according to sources cited by krebsonsecurity, signal messages suggest he knew shinyhunters had stolen fbi data and said nothing to the bureau before the group threatened to leak it. whether or not that holds up remains to be seen. the shape of the accusation is what the industry has quietly feared, because its own incentives make that shape possible.
how does the ransomware negotiation industry function? some firms charge flat retainers, some charge a percentage of the final amount paid. the negotiator is supposed to argue the threat actor down. yet a percentage fee quietly rewards the person for leaving the payment large. no wrongdoing is required for that to corrode trust. the incentive sits inside the transaction.
this is no longer a theoretical conflict. earlier this year angelo martino, a former ransomware negotiator, pleaded guilty to conspiracy to commit extortion. he had been feeding blackcat actors confidential details about the clients he was negotiating for. that meant their insurance policy limits and their internal negotiation positions. his clients did not know he was doing this, and neither did his own employer. across five victim negotiations he sold the other side the one thing the victim was paying him to protect. the attackers paid him for the information. in a separate strand, he admitted helping deploy the actual ransomware itself. law enforcement has since seized about US$10 million from him.
this month prosecutors separately charged monstercloud owner zohar pinhasi with wire fraud. they allege he told victims not to pay the ransom, promising he could recover their data with his own proprietary decryption tools. however, no such tools existed. he was quietly paying the attackers for their decryptors, more than US$8 million in total. then he billed his clients more than US$19 million for the recovery. in one case the ransom ran roughly US$8,200 yet the client was billed about US$150,000. dubrovsky does not create the structural question. his case arrives after the structure has already shown, more than once, where it breaks.
the issue with this ransomware negotiation industry is the victim cannot reliably check the negotiator to ensure they are doing what they are paid to accomplish. the client is non-technical, frightened, and on a clock. that client hands its most sensitive decision to an outside expert precisely because it cannot judge the threat itself. every piece of leverage sits on the professional’s side of the table. an industry built on that asymmetry does not get to act surprised when the asymmetry is abused.
before a negotiation even starts, the responder already knows the victim’s insurance ceiling, its internal maximum, its recovery position, and how many days it can afford to remain dead in the water. the threat actor, working only from the extortion channel, is guessing at all of it. the victim’s walk-away number is the single most valuable fact in the room, and the negotiator holds that card. that is exactly what martino handed blackcat. pass that number across and everything after it is theater, because the attacker already knows the floor it has to hold.
independence is one of the variables deciding whether the extortion economy works. coveware, which negotiates these cases, has tracked the share of victims who pay falling to record lows, now under a third, and the adversaries are starting to feel the pressure. an honest intermediary who tells a client it can recover without paying directly suppresses attacker revenue, and a compromised one can push the number back the other way. the person in the middle is a lever, and the extortionists know which way they want it pulled.
i have written before that you can seize the servers but not the business model. the same truth runs the other way. law enforcement has spent years taking down infrastructure, arresting administrators, and seizing dedicated leak sites. the ecosystem has absorbed every blow because the money and the structure outlast the arrests. seizures damage the machinery. insiders expose the relationships that keep it running. the evidence against dubrovsky reportedly came from one arrested man’s chat history.
the allegation that a responder knew about a theft of federal data and stayed silent points at a gap the field has never really closed. a lawyer enters a profession with formal duties to the client and the court. a doctor enters one with licensing and a duty of care. ransomware negotiation has no comparable profession-wide license or uniform standard governing the role. the obligations that do exist come from contracts, from sanctions law, or from whatever profession a given negotiator happens to come from.
sanctions law is the sharpest of those. paying some sanctioned ransomware threat actors can itself break the law. the u.s. treasury’s office of foreign assets control has warned that victims and the firms acting for them can be held responsible. a compromised negotiator can do more than betray a client. it can route one straight into legal exposure.
none of it requires dubrovsky to be guilty. the case may collapse. the chats may be misread, the anonymous sources may be wrong, and the sealed file may tell a different story than the leaks about it. the structural point survives either verdict. an unregulated, self-policing industry sells trust as its core product while holding more leverage over its clients than almost any other professional service, yet carrying fewer uniform obligations than most of them. it has been asking the world to take that trust on faith, and faith works right up until the first time it does not.
the organizations that hire these firms are not buying technical skill alone. they are buying the belief that the person on their side of the table is only on their side. that belief has been cheap for a long time.
the shinywire operator is still unnamed, dubrovsky is still only charged, and the role still has no profession-wide license. the bill for cheap trust is finally being itemized, and the people least equipped to read it are the ones who will go on paying it.
the extortionist never asked to be trusted. only the negotiator did.