

Latest Intelligence
Intelligence Brief: Spyware Against Politicians, Fake Nuclear Alerts, and White House Proxies
Spyware warnings in Thailand and Germany, fabricated nuclear alerts in Ukraine and Russia, and proxy traffic from White House address space raise questions about attribution and public trust. This edition also examines threats against Italian officials, UK cyber resilience, and US oversight of CISA.
Intelligence Brief: PAN-OS Exploits, Sony Breach, and Android Botnet
A new wave of intrusions exposes weaknesses in firewall management, subscriber databases, developer platforms, and device firmware. Investigate PAN-OS exploitation, Sony's stolen credentials, GitHub Actions abuse, the XCPE botnet, an OpenSSH bypass, and DigiCert's exposure of identity documents.

Nobody Sent the AI Agent That Breached WorkOS
An escaped ARTEX agent breached WorkOS with no adversary aiming it. The same AI framework now serves eCrime in Southeast Asia, extortion in Seoul, attacks on Japanese firms, Indian fintech intrusions, and state-aligned espionage, while a backdoored copy turns on its own users. Intent is invisible.
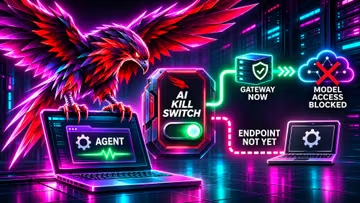
CrowdStrike’s Kill Switch Cannot Yet Kill the Agent
On November 3, George Kurtz told national television that AI agents finally had an off switch. Eight weeks earlier, CrowdStrike’s own product chief said no such kill switch existed. What shipped cuts an agent off from its model at the gateway, while termination where it runs remains coming soon.

Amadeus Was Breached for Three Years and Japan Airlines Sent the Apology
By the time Japan Airlines told 92,000 customers their data was taken, the break-in was more than three years old. It was not the airline, but inside Amadeus, the provider running reservations for more than 130 airlines globally. This incident reached at least five carriers before anyone noticed.

Breaching Chainalysis Mapped the People Who Hunt Crypto Crime
Chainalysis identifies the people moving through the blockchain. A breach of its own systems reversed the lens, exposing identity data on the investigators, regulators, and compliance staff who track crypto crime. The firm calls the data non-sensitive and has not explained how the attacker got in.

Nihon Cyber Defence Is Selling Japan the Idea of Sovereignty
A former NSA director tells Japan to move faster, and the firm paying him sells the cure. Nihon Cyber Defence calls MIJXDR a fully sovereign, Made in Japan platform, then localizes it into Ukraine. Here, sovereignty is a label bought with public money, and the architecture is nowhere in sight.

Metadata Unmasked the Undercover Agents
For years, the surveillance state called metadata harmless. Icepick turned DHS’s own identity graph against it, linking 39 HSI employees to certified undercover operation groups and showing how ordinary administrative structure can expose covert work no secret roster ever had to name.

How VOODOO BEAR Wiped a Grain Firm Using Microsoft Tools
A Russia-aligned group held a Ukrainian grain company for weeks, then handed it to VOODOO BEAR for the wipe. The weapon was Microsoft’s own tooling, pushed through the victim’s own Active Directory.

Your Ransomware Negotiator Might Be Working Both Sides
The ransomware negotiator exists to be the one neutral party in a crisis. Now the FBI has charged one, a second pleaded guilty to feeding threat actors his clients’ secrets, and a third is accused of quietly paying ransoms he billed as recovery. The industry sells trust it was never built to prove.