
Latest Intelligence

Threat Actor Asked AI Where to Sell Stolen Data Then to Write His Résumé
A lone threat actor pointed an open-source Chinese AI agent at South Korean banks and let cheap language models do the scaling. Then he asked one of those models to write his résumé. CrowdStrike recovered all of it, and the same memory that powered the attack documented the operator behind it.

China Paid UK Academics to Build Its Spy Tradecraft
MI5 named a Chinese front that funded more than 100 UK academics to build AI and espionage tradecraft for the Ministry of State Security. No breach, no malware, just a grant. China did not hack the research. It bought it, and many academics never knew who was behind it.

China Phished the People Who Write America's AI Rules
To learn where US AI policy is heading, you do not breach a frontier lab. You phish the analysts who shape it. China-aligned TA419 did that, impersonating a former White House official and an Anthropic employee. The model tells you what America can build. The inbox tells you what it plans to do.

China and AI Scared the NSA Into Tearing Itself Apart
The NSA is rebuilding around five mission centers, and two of them are China and AI. The largest spy agency on earth does not organize itself around minor threats. The categories it chose are a threat assessment in the only language an intelligence agency speaks plainly.

China Hacked the Software that Reads Every Key You Press
UNC3569, a china-nexus group, broke into Windows machines through Sogou, the input tool millions use to type Chinese characters. One crafted link, one click, and a backdoor opened. Tencent patched it fast, but the embedded browser underneath is still ancient and defenseless.

China Did Not Steal American AI, It Interrogated It
NSA, CISA, and FBI accused six Chinese firms of extracting billions of tokens from Claude, ChatGPT, Gemini, and Grok to train competing models. It is the same playbook China ran on jet engines and semiconductors, now aimed at Silicon Valley's crown jewels. The theft looks exactly like ordinary use.
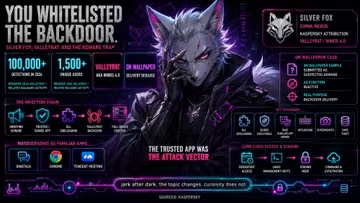
You Whitelisted the Malware Yourself
A China-nexus group hid a full-control backdoor inside a real Chinese wallpaper app, the kind of harmless adware nobody takes seriously. That is exactly why it worked. The disguise was so convincing the ads never even ran, and that was the tell that gave it away.
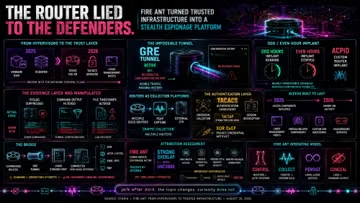
The Most Dangerous Intrusion Is the One That Turns the Alarms Off
Most attackers try not to get caught. Fire Ant breaks in, then disables the cameras and edits the tapes. The China-nexus actor turned Cisco routers into spying platforms, suppressed the logs, and altered what admins were even allowed to see.