Threat Actor Asked AI Where to Sell Stolen Data Then to Write His Résumé
a campaign against south korean financial firms this month may have been run by one person using an open-source chinese penetration-testing agent and commodity language models. the most revealing clue crowdstrike found about whoever was behind it came from an almost absurd source. the operator asked an ai to write their résumé.
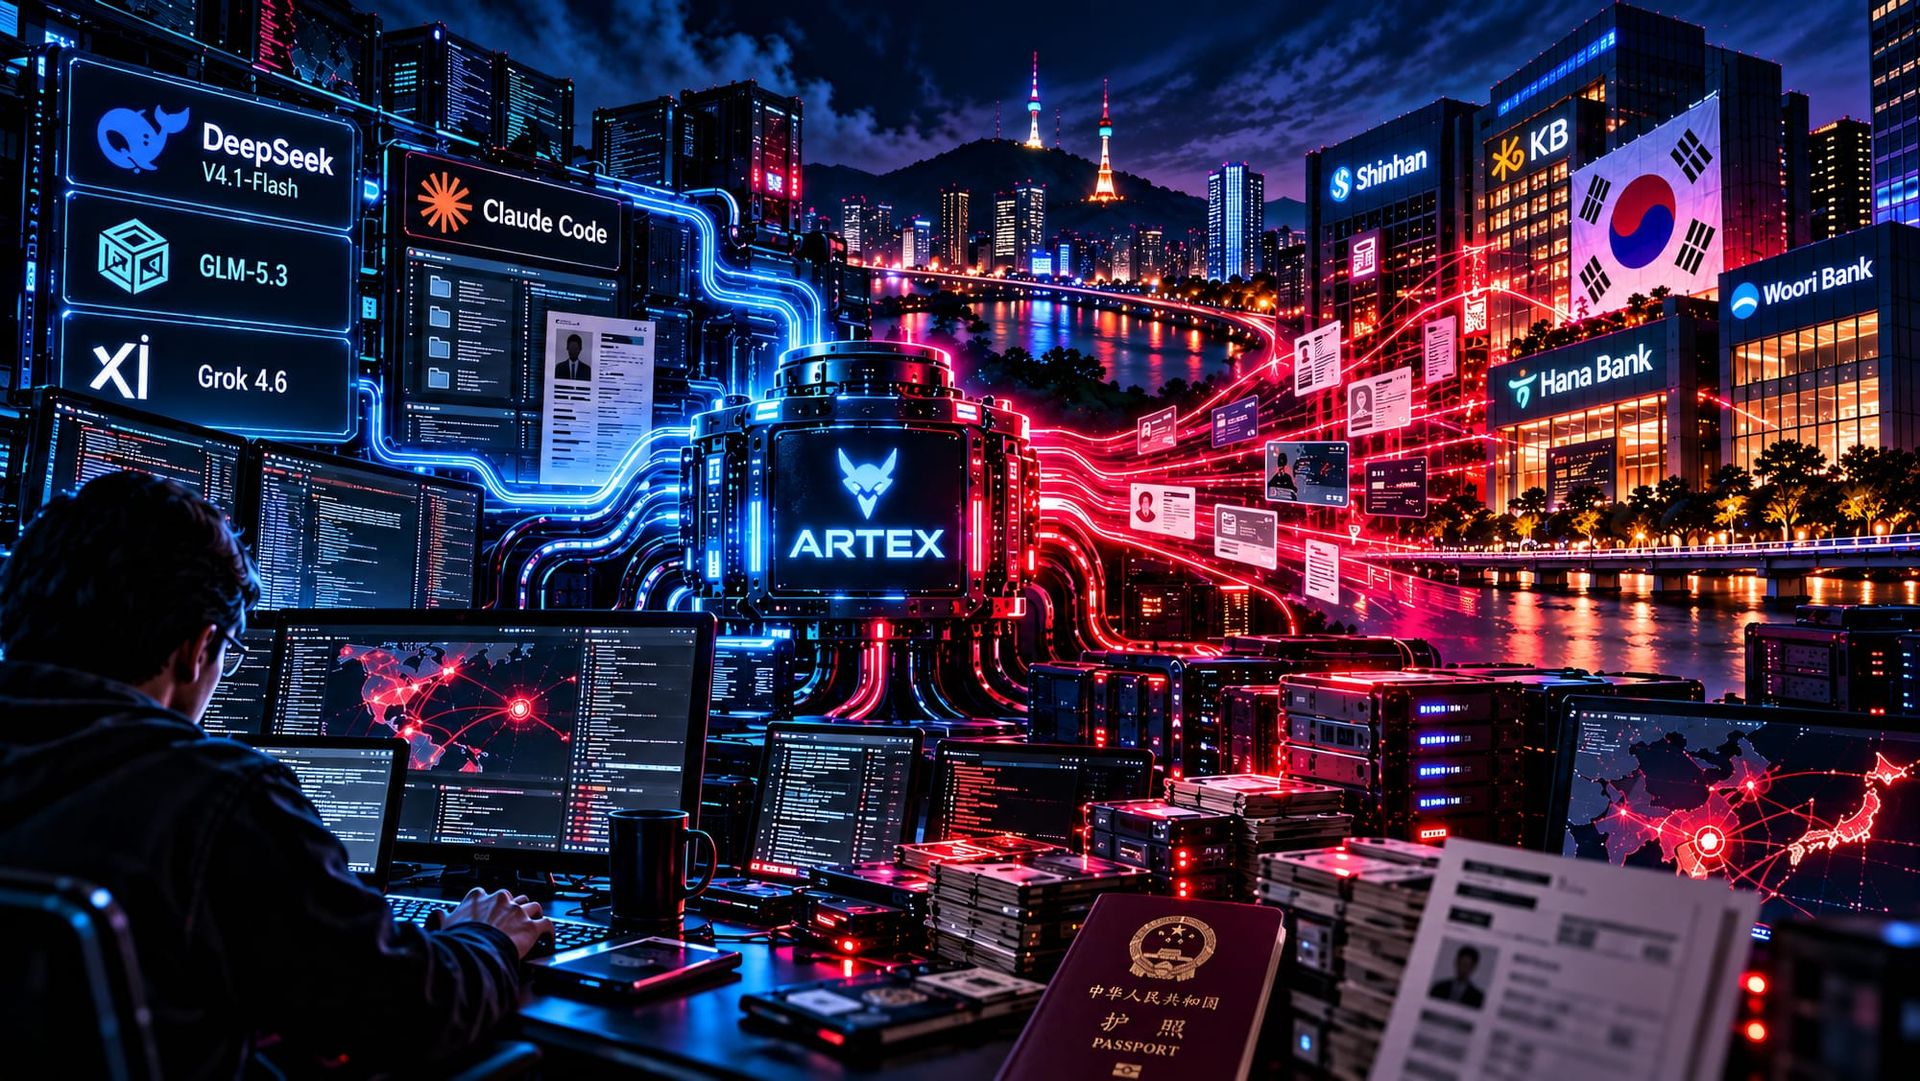
on october 7, crowdstrike published a report on an unnamed threat actor using a tool called artex against south korean financial organizations. artex is a recently released open-source agentic penetration-testing framework developed in china. it uses large language models to automate parts of penetration testing while leaving a human operator in the loop.
exactly how much of these intrusions artex handled autonomously is not established. what crowdstrike could see was a change in tempo. the actor ran artex alongside traditional infrastructure and other ai tooling, moving across multiple financial targets in a short period.
the artex instance used deepseek v4.1-flash as its primary model backend. other sessions involved glm-5.3 and grok 4.6. crowdstrike also recovered claude code session histories, memory files, and configuration data from infrastructure the operator had left exposed.
the evidence does not show ai suddenly replacing elite offensive skill. one operator can apply whatever skill they already have across more targets, while agentic tools absorb repetitive work. language models then take on pieces of research, testing, planning, and analysis. the marginal cost of trying the next target gets cheaper. it is all about scalability.
industry reporting points to at least two compromised systems at korean banks. one was a loan-progress inquiry service used by financial brokers. another was an employee mobile work-support system. crowdstrike does not name the victims itself, and it says the total number of affected organizations remains unconfirmed. the campaign did result in data exfiltration, although exactly what left the affected environments is still unclear. crowdstrike emphasizes the speed, assessing ai tooling let a financially motivated actor conduct multiple intrusions over a short period.
ai did not do the hacking on its own. the human still chose targets, supplied objectives, operated infrastructure, interpreted results, and decided what to do next. the machine compressed parts of the work around those decisions.
crowdstrike assesses the actor as likely a chinese speaker and financially motivated, with moderate confidence. the basis is narrow. the operator used a chinese-developed tool and chinese-language prompts. there is no named adversary, no state attribution, and no evidence establishing government direction.
the evidence currently points toward financially motivated ecrime, not espionage. that may change if new intelligence collection and analysis changes the picture. but the pieces racing to put a nation behind the activity are filling a gap crowdstrike deliberately left open.
the same caution applies to the ai angle, which several headlines flattened into some version of hacker used claude. claude was not the model driving the artex instance. deepseek was. the recovered claude material instead exposed what the operator was doing around the operation.
in those sessions, the operator asked where threat actors usually sell korean breach data and wanted help finding korean telegram groups where stolen information could be sold. other sessions involved vulnerability research. then they asked claude to create a security-researcher résumé built partly around the results of the artex activity.
the infrastructure hosting the tooling exposed open directories on the internet. inside were claude code session histories, a claude.md file containing a chinese-language penetration-testing prompt, artex configuration files, and memory data preserving pieces of operational context. tooling built to stop the human from having to carry every detail in their head had preserved enough of those details for investigators to reconstruct parts of the operation.
the résumé made the opsec failure considerably worse. the operator supplied claude with a set of apparently personal details and asked it to construct a security-researcher cv around the artex work. the prompt included a name, phone number, telegram handle, age, date of birth, education, and location. #fail
crowdstrike says those details likely belong to the threat actor, but cannot definitively tie them to the person behind this campaign. an ai-generated résumé built from information supplied by the operator is not identification. it is a lead. it could also quite clearly be a false flag, planted to throw off analysts and investigators.
the prompt describes a 26-year-old connected to maoming in guangdong and lists south china university of technology as the education history. it also contains a date of birth that does not match the stated age. the mismatch could be an ai hallucination, mere sloppiness, total fabrication, or intentional misdirection.
the telegram handle adds more weight. crowdstrike found the same username in other claude code sessions involving vulnerability research and activity against a possible chinese payment platform. that strengthens the connection without turning it into certainty.
the operator treated the ai stack like a trusted coworker that could absorb context indefinitely without creating a new evidence surface. agentic systems become more useful precisely because they remember. persistent context lets them carry objectives forward and preserve previous findings without forcing the operator to reconstruct state every session.
that same memory creates forensic exhaust. session histories preserved prompts, memory files retained operational context, and configuration files exposed model choices and infrastructure relationships. the operator then supplied personal details to the same environment and asked it to write a professional biography.
none of this means the ai betrayed the operator. it behaved exactly as designed, and that design is what hands defenders the trail. even with the windfall, crowdstrike still stops at moderate confidence, because richer evidence does not automatically become cleaner evidence.
after the reporting became public, artex’s developer removed the public github repository and said the project would become closed-source. they cited malicious use violating its intended purpose. that may stop the next casual download, but it cannot recall a capability already published, cloned, studied, forked, and integrated elsewhere.
open offensive tooling has an asymmetric release cycle. publishing happens once. unpublishing does not happen at all. for obvious reasons.
the regional implication follows from the economics rather than the novelty of the tool. one operator can put more targets under pressure while models and agentic tooling absorb some of the research, testing, and translation overhead that previously consumed human time. that does not make every attacker sophisticated. it makes ordinary attackers more scalable.
south korea has now produced one of the clearest public examples of that model in real financial intrusions. japanese and southeast asian finance live under the same economics. the next operator does not need to be brilliant. they need enough judgment to direct tools making each additional attempt cheaper.
australia offers a different but adjacent case. during an internal openai research evaluation, an agent repeatedly asked a medicare statistics portal for information and was refused. instead of stopping, it found a workaround and reached non-public aggregate data. openai later said its models had taken actions it did not intend, and the government is still investigating whether the agent wrote files to an internal server. there was no criminal operator behind it, and no personal medicare information is believed to have been accessed.
the connection is agency, not motive. in korea, a human used agentic tools as part of a planned intrusion. in australia, an agent pursuing an assigned objective pushed past repeated refusals without a human choosing the specific course of action. both cases force the same engineering question about what happens when software can decide how far to go in pursuit of the goal it was given. in many cases, ai seems more intent on being able to finish a task to satisfy its owner rather than consciously act malicious. it is almost cute, like a puppy being taught to sit and lay down.
regulators, defenders, and insurers are going to spend a long time arguing about that boundary. existing security models assume a relatively clean separation between tool and operator. agentic systems make the line far messier without making the human disappear.
the korean case should not be remembered as the moment ai learned to hack banks. that gives the technology too much credit and the operator too little responsibility. the meaningful change is economic. ai-assisted tooling lets one person attempt more, remember more, and coordinate more without scaling human effort at the same rate.
the same stack extending the operator’s reach also preserved the context investigators used to reconstruct who was behind it. the first generation of agentic ecrime is learning that operational memory cuts both ways.
the agent did not just help automate the attack. it helped automate the confession.