One Login Cost Bitget US$388 Million
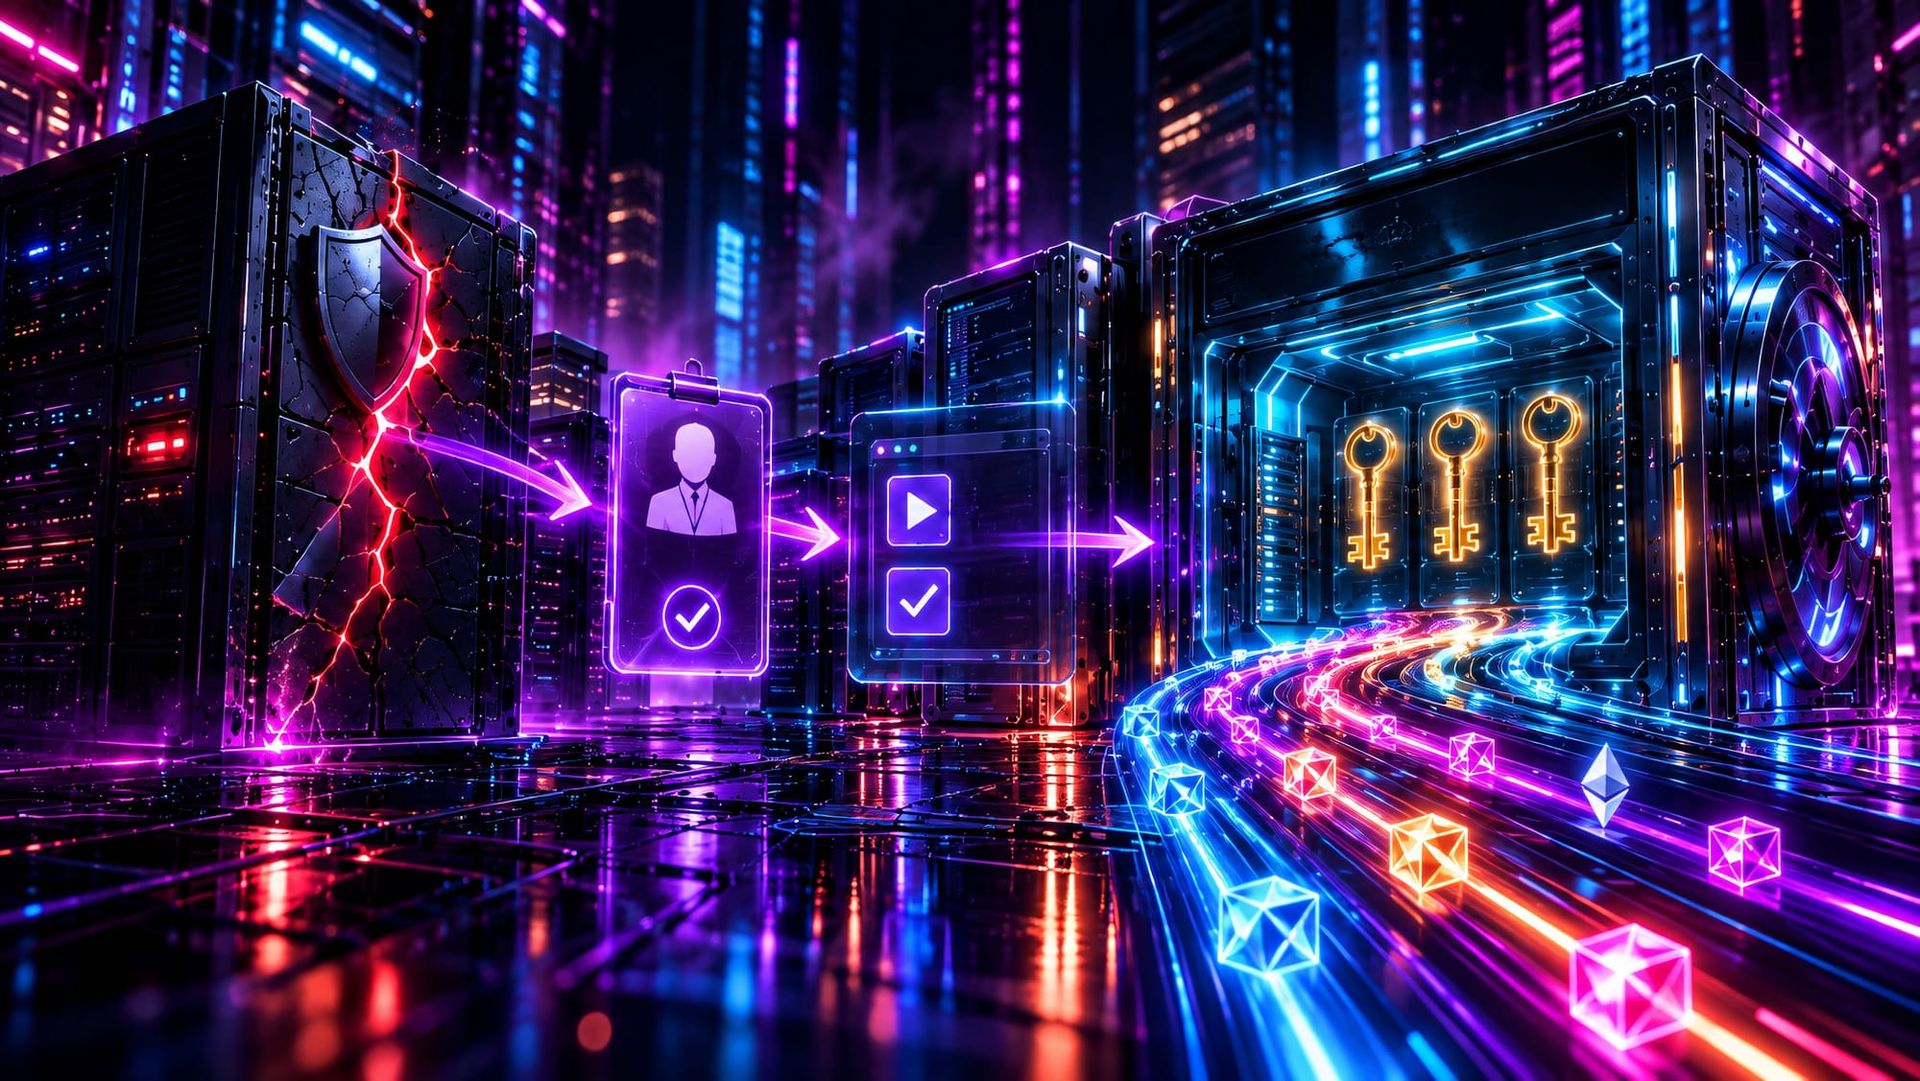
when a crypto exchange loses US$388 million, the knee jerk reaction is to assume someone broke in and stole all the crypto. maybe it was a stolen private key, maybe a flawed smart contract, maybe even a cryptographic error. however, that is not what happened to bitget. the blockchain held up just fine. the keys held up without issue. what failed was the security product bitget bought to protect itself, and the trust the company placed in a valid login.
here is what bitget's ceo, gracy chen, described on september 28, four days after the theft. the attacker apparently exploited a zero-day in a third-party security product and used it to obtain high-level internal admin credentials. from there they did not need to break anything. they had almost god-like power at this point.
so they injected fraudulent withdrawal commands into the wallet backend and disguised the activity as routine administrative work. again, no private keys were compromised. the money left through the front door, carried out by someone holding a legitimate badge. from the thirty-thousand-foot-view everything looked legit.
the attacker was in no hurry. at 18:31 utc on september 24, they moved two tiny test transfers. 0.184 eth from an ethereum hot wallet, and 193 trx from a tron wallet. both transactions were deliberately under bitget's risk-control thresholds so no alerts were tripped. about half an hour later, between 18:58 and 20:09, they ran 17 large transactions across multiple blockchains worth roughly US$361 million. this made up the bulk of the eventual US$388 million total.
bitget's reconciliation system caught the discrepancy at 19:05, seven minutes after the first large transfer. the risk engine began blocking platform-wide user-initiated withdrawals at this point. but by then the fraudulent backend activity was already underway, and the attacker continued moving funds until 20:09. the attacker even deleted the traces of their own commands on the way out. not unheard of, but also not standard procedure for a lot of threat actors operating today.
let us dissect this a bit more.
the first is the entry point. the thing allowing the attacker in was a security product. this is the exact category of tool every cyber security engineer tells you is a must buy. the very tool you purchase to decrease your attack surface became the attack surface. this is not a new idea in the abstract, every piece of software you add is more code that can fail. this lands a bit differently because a security vendor's zero-day handed an attacker the keys to a US$388 million wallet. your defensive stack is not exempt from being the way in. it is often the most trusted and least questioned software you run, which is exactly what makes it worth compromising.
the second is what happened after. once the attacker held valid admin credentials, the theft looked like normal operations. no malformed requests, no exploit crashing a service. this was merely an administrator issuing withdrawal commands, which is a thing administrators legitimately do quite frequently. this is the same uncomfortable lesson from every credential-abuse breach.
when an adversary logs in as someone real and does what the system is built to allow, detection stops being about spotting an attack. it becomes about trying to spot a lie. sadly, bitget only noticed because its books did not balance, not because anything looked like an attack.
bitget suspects the same threat actor behind other incidents is responsible for this attack. trm labs found on-chain overlaps pointing towards the north korean cluster tracked as tradertraitor. mandiant and slowmist are investigating. it sounds like a reasonable lead. this is not a confirmed identification, so we must wait for further analysis and reporting before we have high confidence this was actually perpetrated by dprk.
the reassuring part, if there is one, is bitget's protection fund absorbed the loss and withdrawals are already reopening. users are not eating the US$388 million. the flip side of that is the shape of the attack, because bitget was not careless. a zero-day in a trusted product plus a set of valid credentials is a combination working against any careful company.
the crypto was never the weak point. the crypto is rarely the weak point anymore. the weak point is the same as it is everywhere else. who can log in, what they are allowed to do, and whether anyone would notice them doing it.
the blockchain did not betray bitget. bitget's own trust model did. the adversary just logged in and asked it to send US$388 million.