
Latest Intelligence

Denmark Was Not Hacked, It Was Logged Into
Attackers never breached Denmark's national population register. They abused one trusted company's legitimate access to enumerate and pull 8.8 million identities, then got caught by the bill, not by security. Permission, not malware, emptied the CPR.

Eleven Years After the OPM Breach the Pentagon Lost Three Million More Records
OPM was supposed to be the breach that changed everything. Eleven years later, a Pentagon data hub exposed 3 million defense personnel through a file-sharing flaw nobody watched for nine months. DoD wrote the fix into its own 2022 strategy, then skipped it. The warehouses are still open.

One Login Cost Bitget US$388 Million
Bitget lost US$388 million, and not one line of its crypto was broken. No stolen keys, no smart-contract flaw. Attackers exploited a zero-day in a third-party security product, walked in with valid admin credentials, and moved the money out disguised as routine operations.

Hundreds of AI Agents Ran the Attack, Then Broke Their Own Rules
A Russian-speaking attacker pointed hundreds of autonomous AI agents at PaperCut and hit 440 servers across 48 countries, moving from access to domain admin in minutes. The agents were told to avoid Russia, China, and Iran. They hit victims there anyway. Speed and scale come with a loss of control.

Slim Spider Steals the Keys the Cloud Hands Out for Free
A month after PLUMP SPIDER, CrowdStrike named a second Brazilian crew: Slim Spider, and this one is not faking transfers. It is stealing cryptocurrency custody keys straight out of the cloud, by learning to look like something the cloud already trusts. The perimeter never mattered. The token did.

You Never Chose the Company That Just Leaked Your Face
More than 153 million driver's license records are allegedly for sale on the dark web for US$100, traced to an identity verification vendor most victims never heard of. You cannot change your face or your date of birth. Lawmakers want to make this exact model mandatory to use the internet.
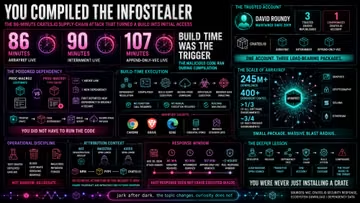
One Hijacked Account, One Crate, 245 Million Rust Downloads at Risk
For 86 minutes on August 20, compiling a Rust project was enough to install an infostealer, no malicious code ever called. An attacker hijacked the account behind arrayref, a tiny crate riding in three-quarters of all Rust environments. You never trusted arrayref. You trusted the account.
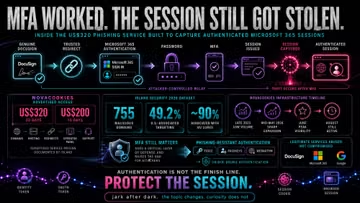
NovaCookies Phishing Kit Steals Microsoft 365 Sessions to Bypass MFA
For US$320 a month, NovaCookies rents anyone the ability to walk past your MFA. It does not steal your password. It steals your session, the proof you already logged in, after you authenticate perfectly. MFA did not fail. It just stopped being the finish line.