Attribution Is a Confidence Game
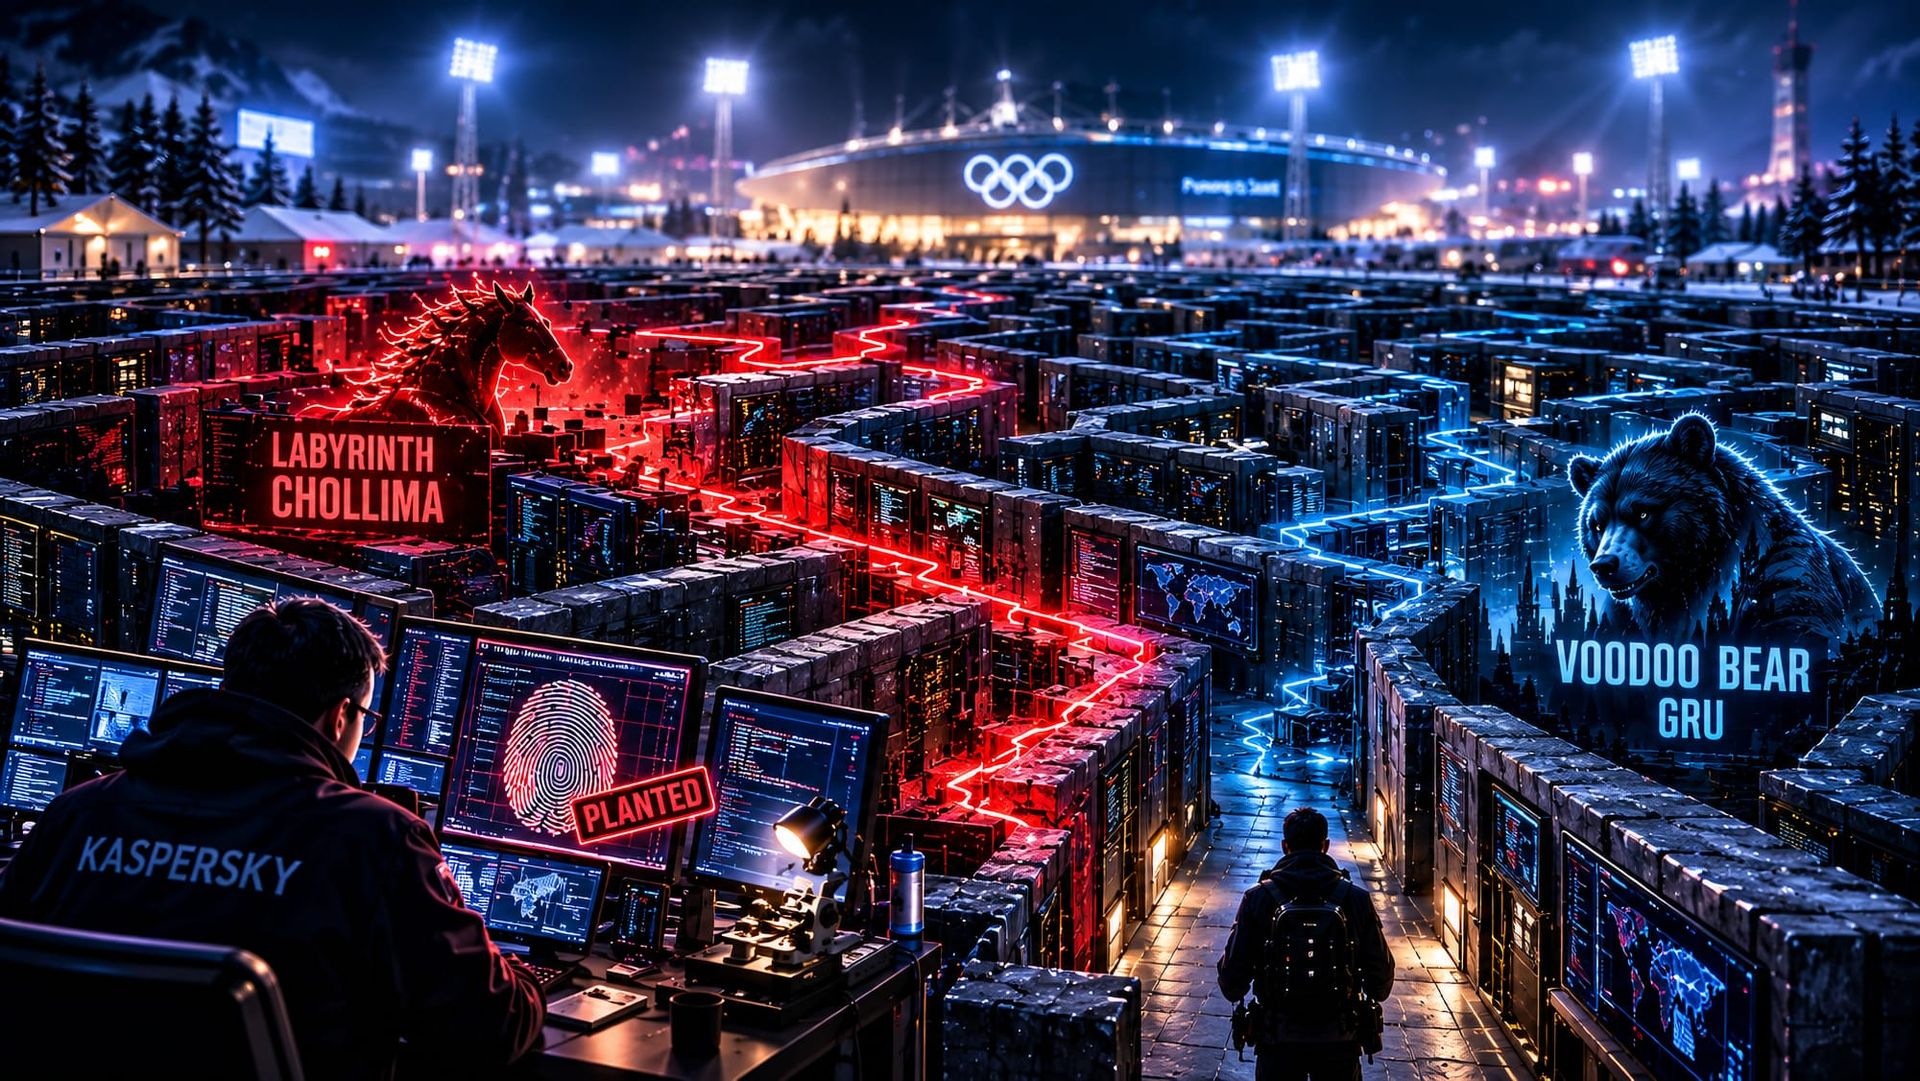
On February 9, 2018, the opening ceremony of the Winter Olympics lit the sky over PyeongChang. Fireworks, a drone swarm overhead, a packed stadium, and a worldwide television audience. A short drive from the stadium, inside a technology operations center, the staff were not watching the show. They were watching systems fail. That night, malware swept through the Games' network during the opening ceremony. It took down wifi, the official website, the ticketing system, and the press center. The organizers kept the ceremony running, and most of the crowd never knew. The malware hit the network once. The false flag was built to hit the investigation next.
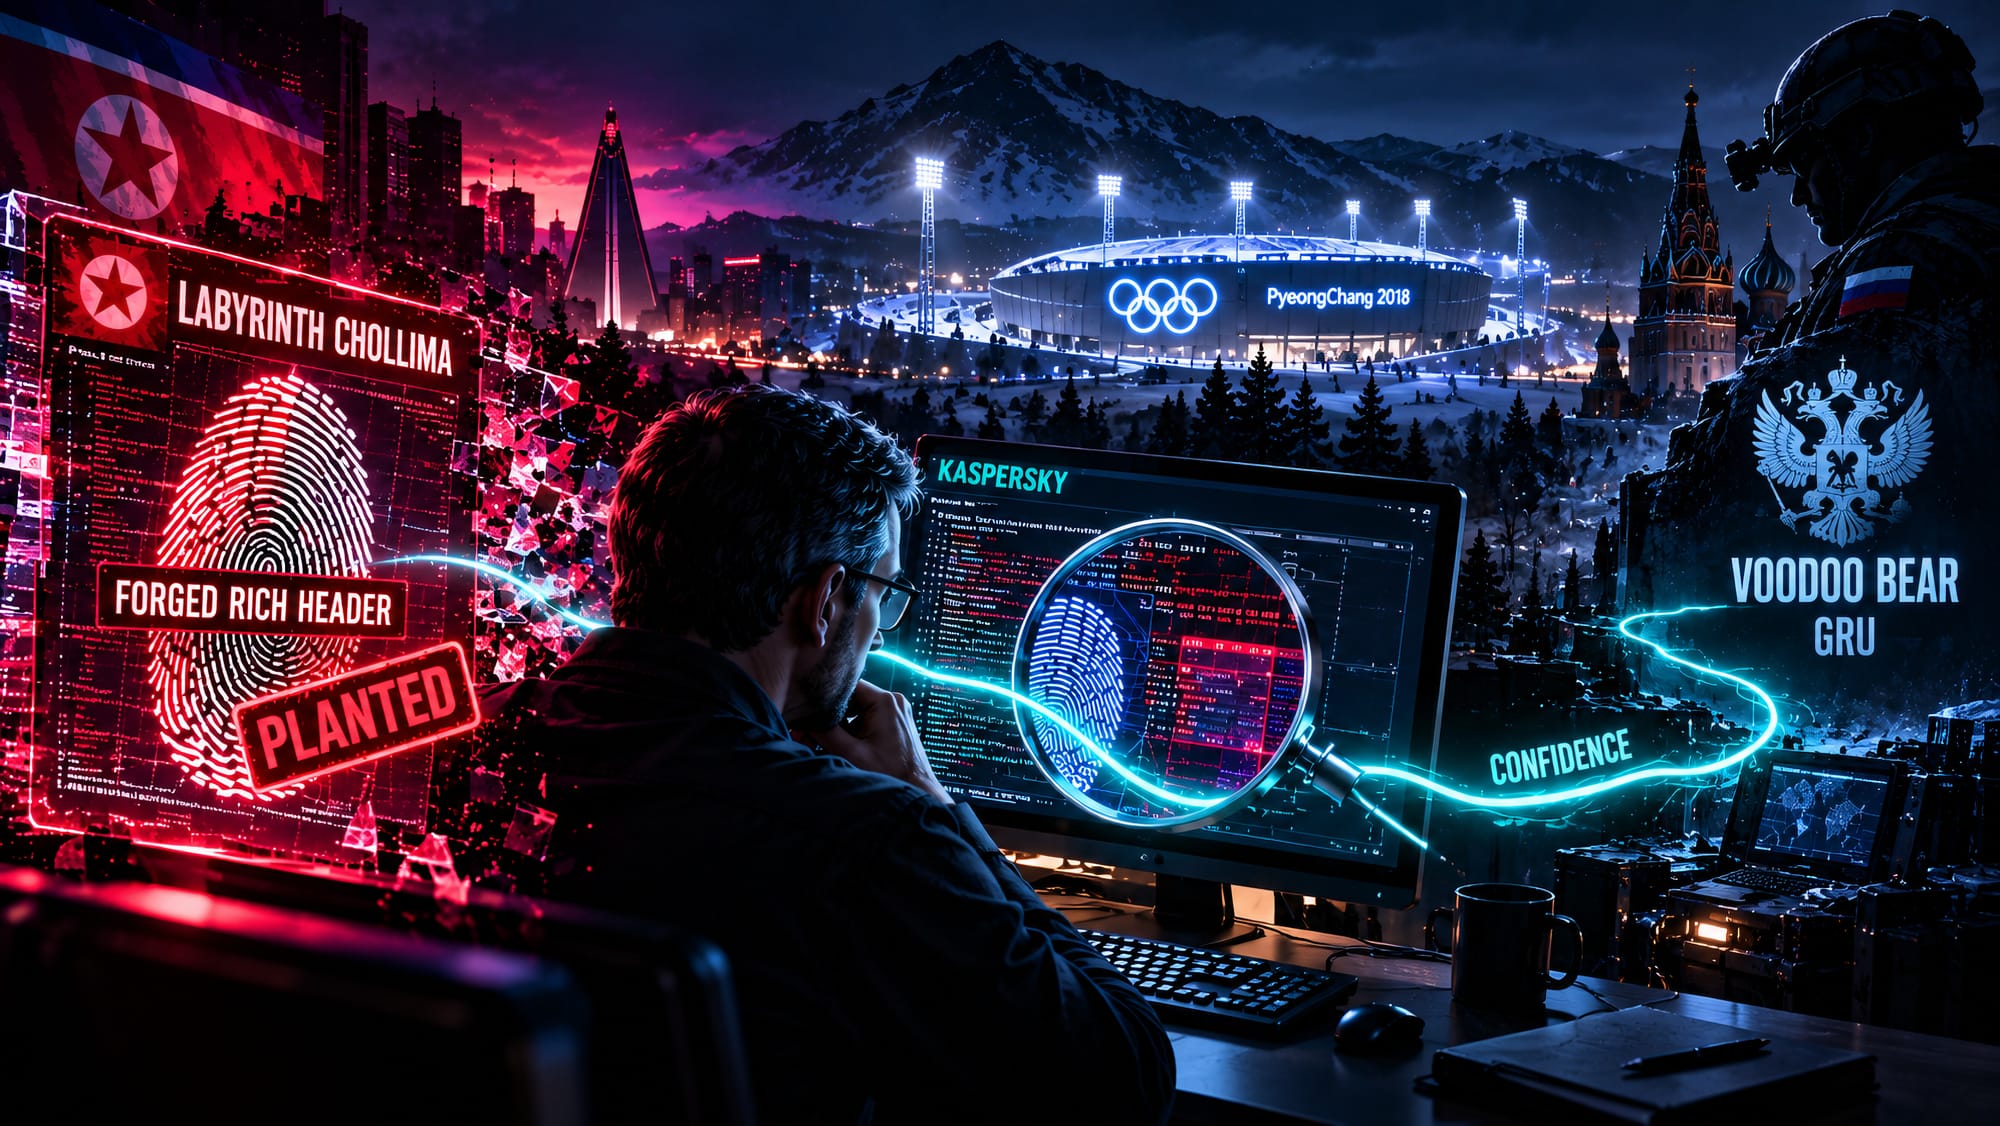
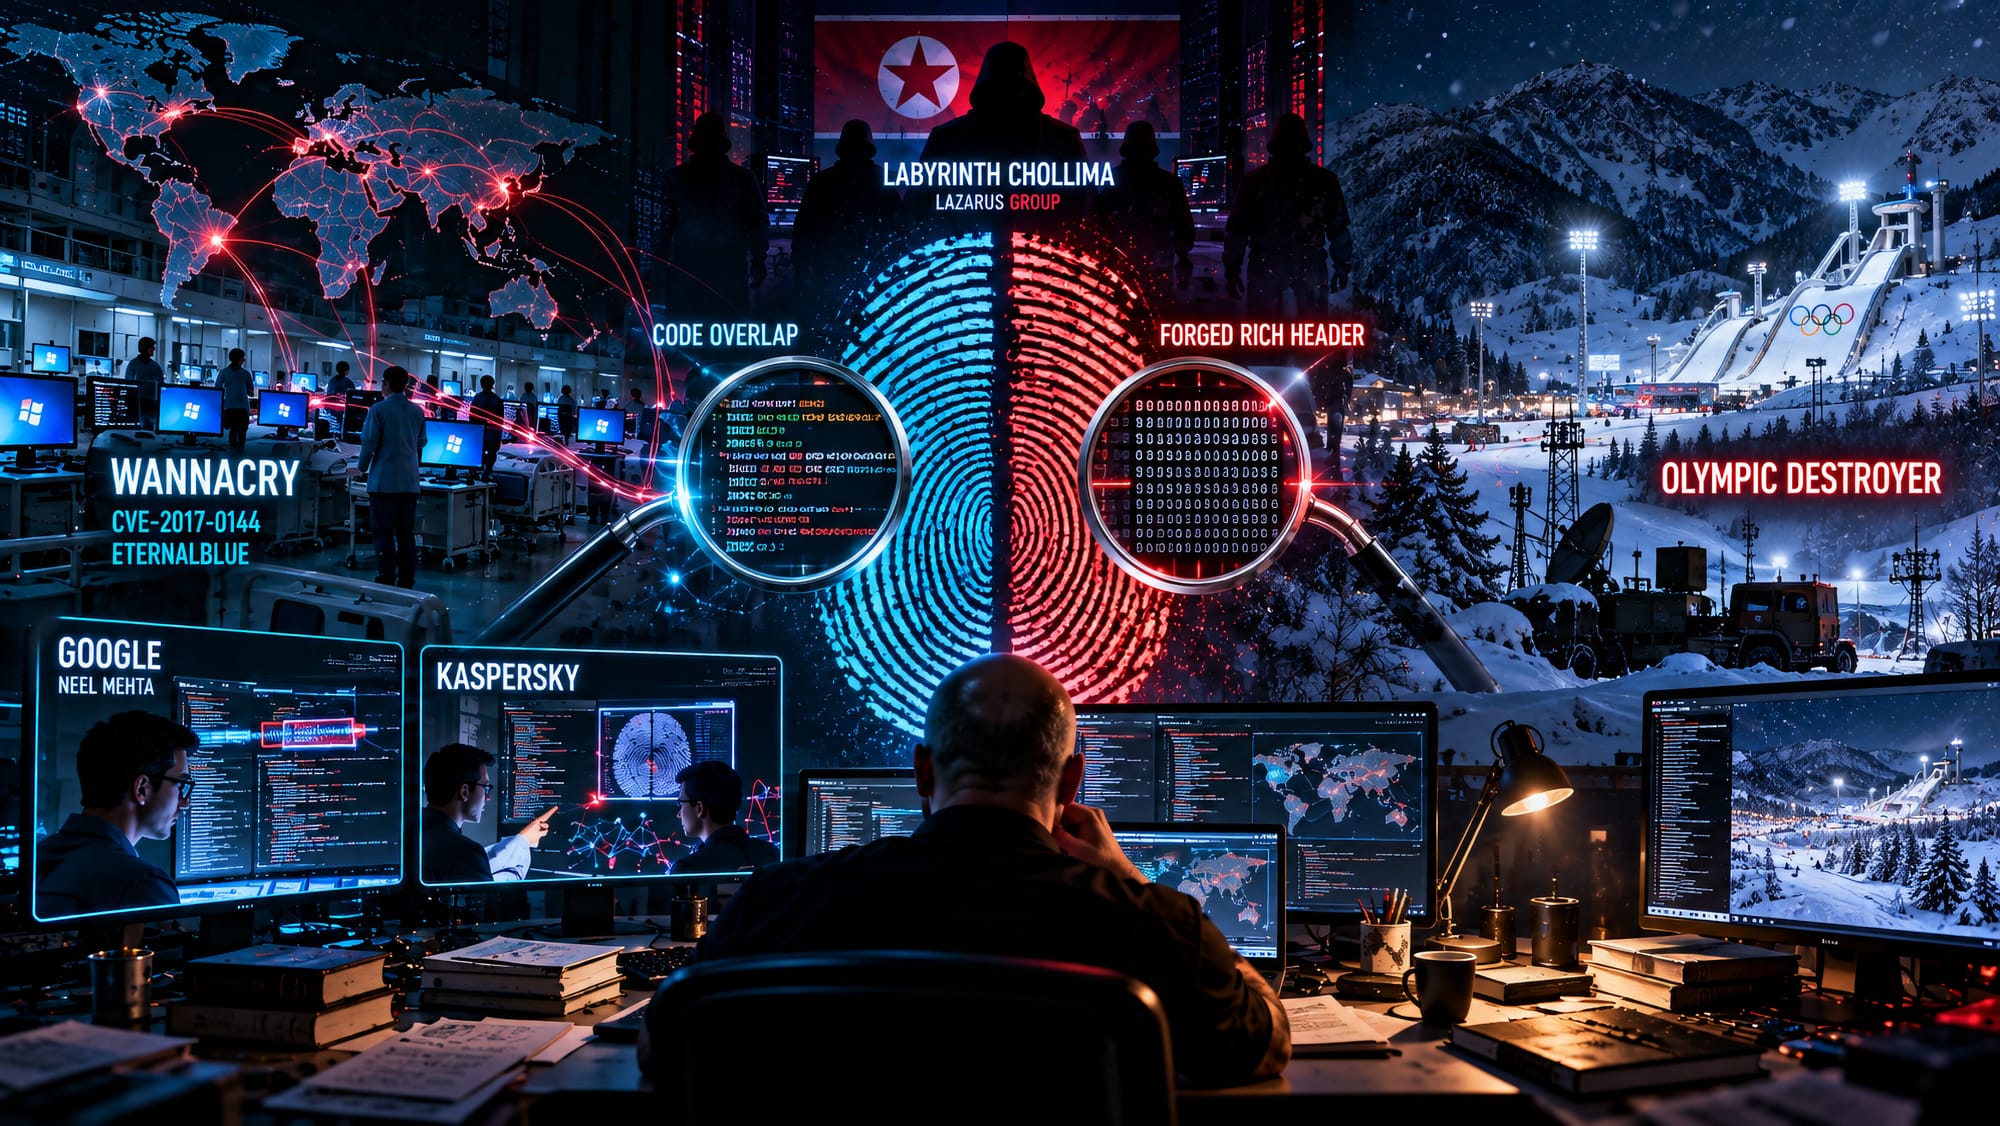
When researchers first pulled the malware apart, a fingerprint inside it pointed cleanly at LABYRINTH CHOLLIMA, also known as The Lazarus Group across the industry, North Korea's best-known offensive actor. CrowdStrike, though, recognizes distinct threat actor groups within the North Korean regime. It was the kind of clue an investigator dreams of finding on the first day. The match was specific, it was early, and it was also a complete lie. Someone had hidden a trap in the evidence, and the trap was built specifically for the analysts.
Attribution Is Navigation
Kaspersky's researchers found the North Korean fingerprint had been forged. When the team first saw the match, it looked too good to be true, a clean alignment with a known North Korean sample, and that is exactly why they held it back rather than rushing it into print. A structure in the binary called the rich header, a compiler artifact analysts routinely use to group related samples, had been hand-tooled to resemble known LABYRINTH CHOLLIMA code while the actual program failed to back up the resemblance. The flag was planted to be found and believed. Months of further work tied the operation to Russia's GRU and the actor CrowdStrike tracks as VOODOO BEAR, also known as Sandworm across the industry. Russia was seemingly acting in retaliation for their exclusion from the Games over state-sponsored doping. In 2020 the United States indicted six GRU officers in connection with that activity.
This is the shape of the whole discipline. Attribution is less the recovery of a fact waiting to be found than navigation through a labyrinth an adversary has built to mislead analysts. Where the most convincing turn may be the one left open to send analysts the wrong way. The myth of Theseus is the right metaphor to consider. The danger is not only the monster at the center. It is losing your way among passages designed to disorient.
Theseus found his way out because Ariadne gave him a thread. In attribution the thread is the confidence statement, low, moderate, or high, trailing behind every claim as a record of how far the reasoning actually reaches. Drop the thread and the exit disappears. What looks like a conclusion is only the story the adversary wanted you to leave with.
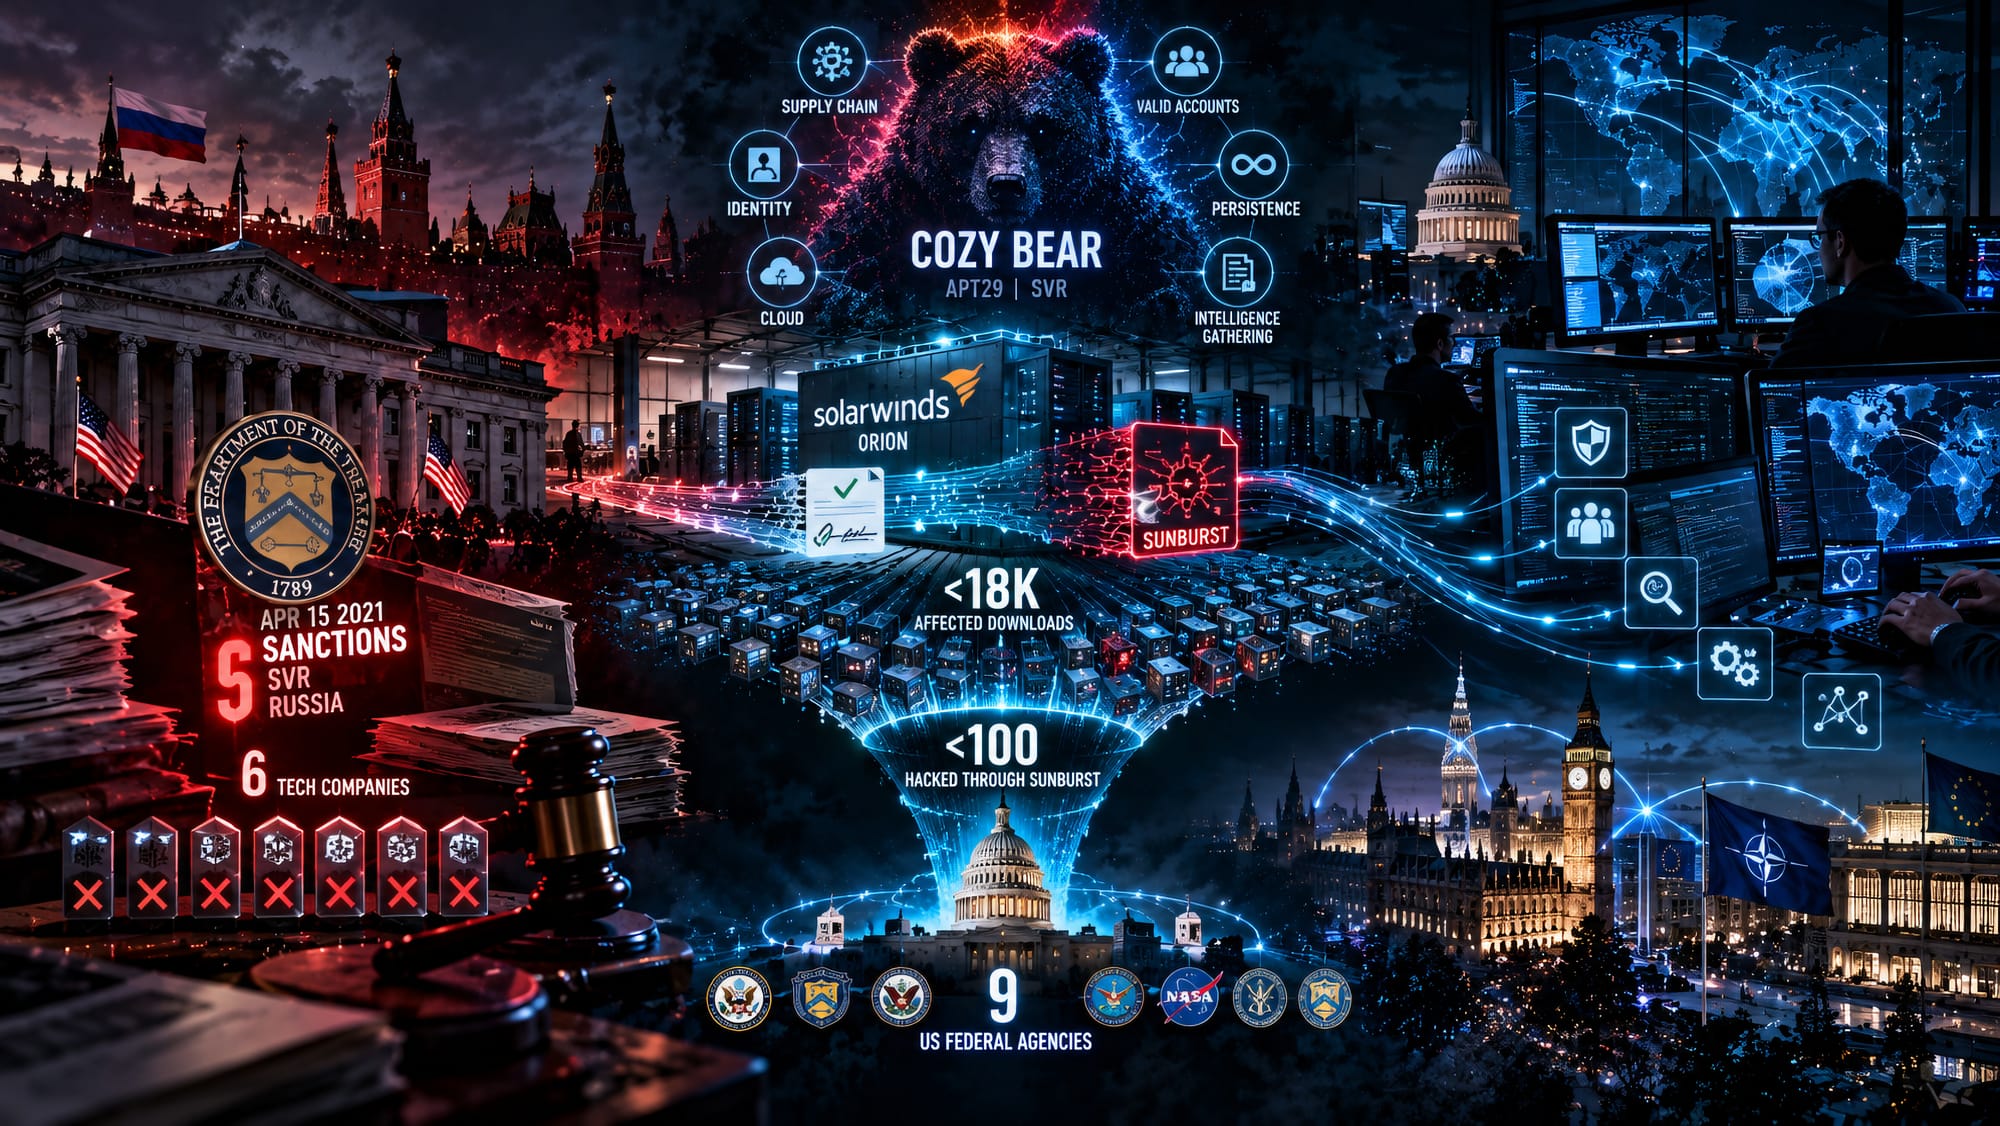
Attribution matters because it moves real levers. When a government imposes sanctions, unseals an indictment, expels diplomats, or answers an intrusion with one of its own, a confidence judgment sits underneath the decision. The United States sanctioned Russia in 2021 over the SolarWinds campaign because its agencies were confident enough to name the SVR. At that level a wrong call becomes a diplomatic incident, or an escalation nobody intended.
The stakes are just as sharp one level down. A defender who knows which adversary is in the network knows which systems it will reach for next, which credentials it will try to steal, and whether it came to spy or to destroy. The same name shapes where a company spends, what an insurer will cover, and whether a breach becomes litigation. Attribution is the hinge between an incident and everything decided because of it. That is why the myths around it are not academic. Each one quietly pushes a real decision toward the wrong answer.
Every Indicator Erodes
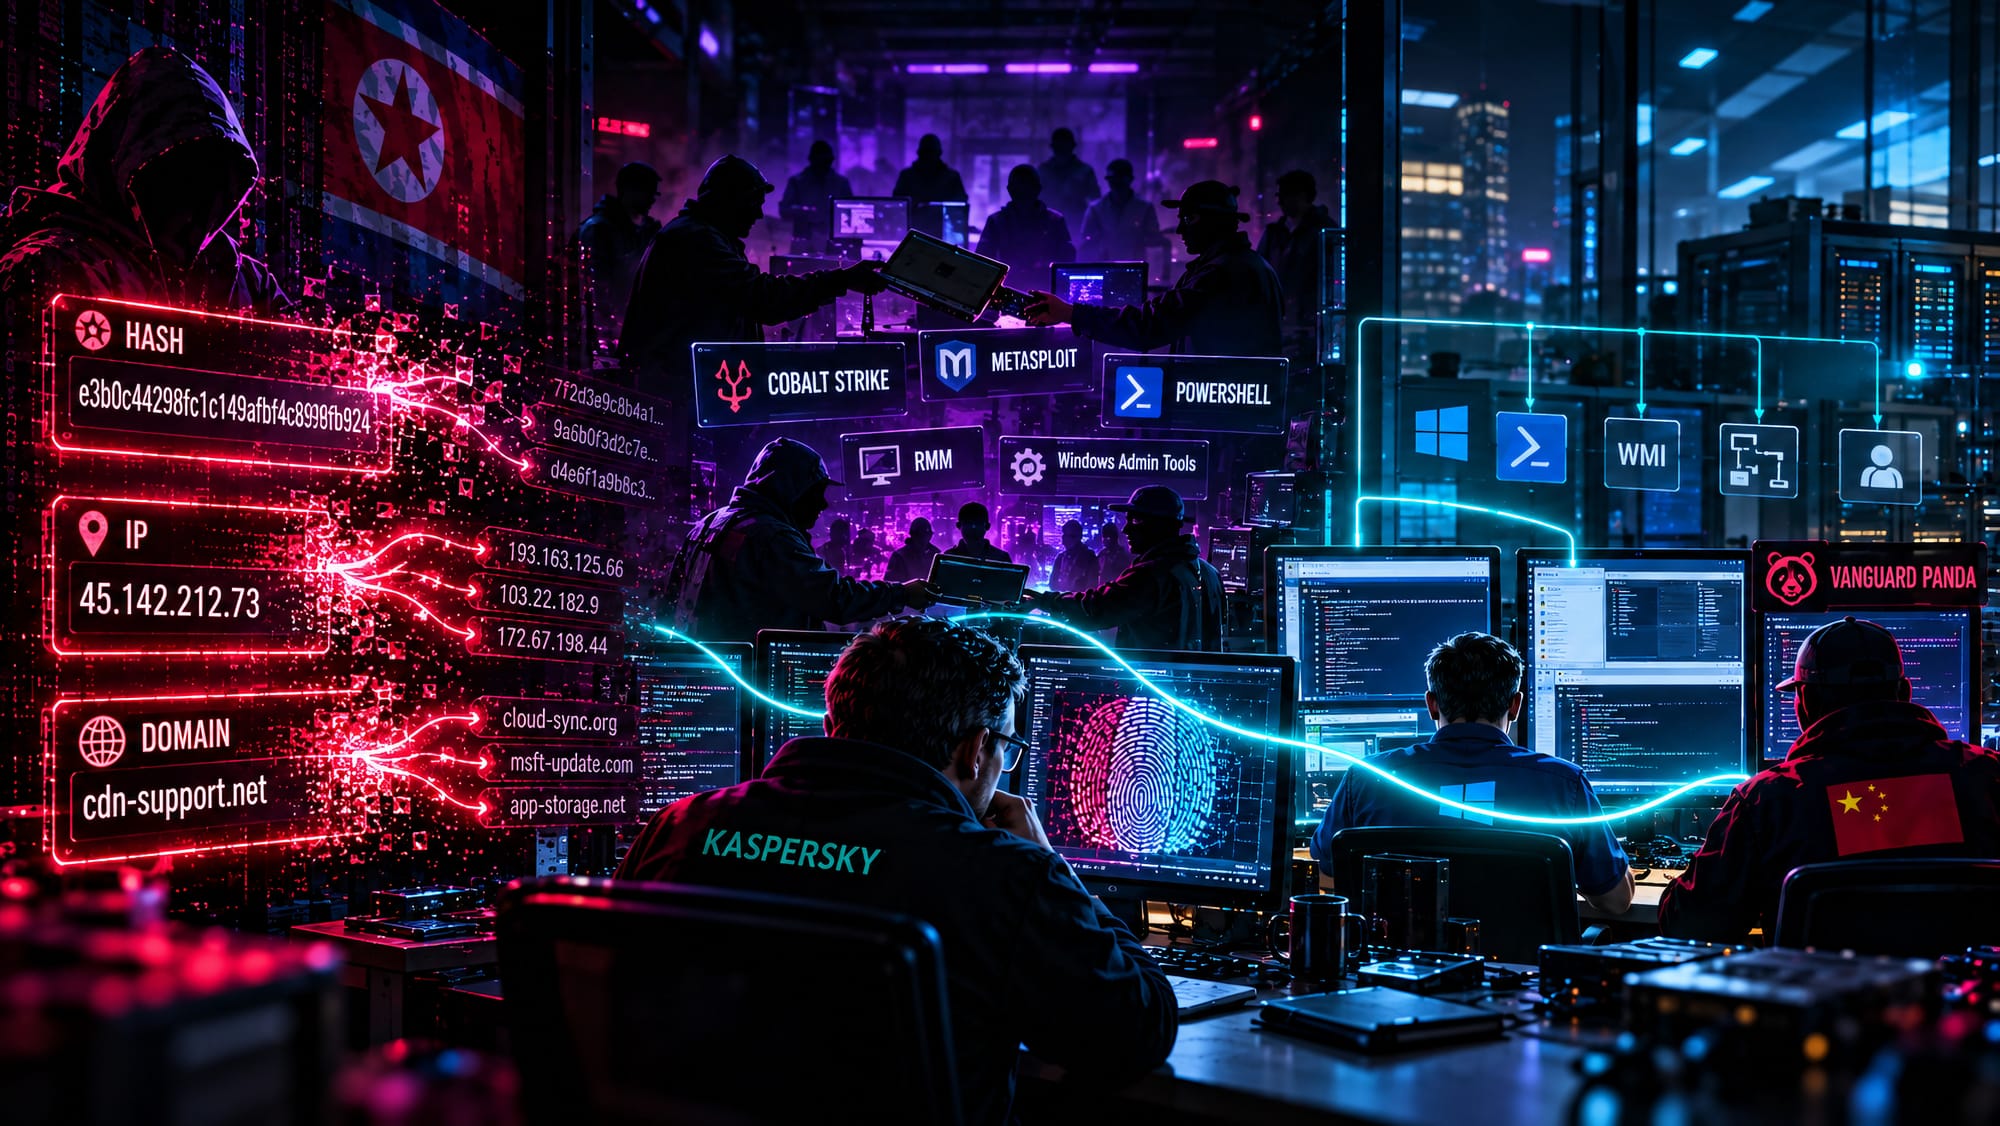
Physical evidence often persists without the offender doing anything to preserve it. Much of an adversary's digital footprint can instead be rotated, overwritten, rented, proxied, or abandoned almost at will. A command-and-control server may stand for an afternoon. A domain can be registered an hour before use and discarded immediately after the operation ceases. Adversaries route traffic through proxies, commercial VPNs, Tor, and bulletproof hosting. They launch attacks from third-party systems they have already compromised. The connection then arrives wearing a victim's address rather than their own infrastructure.
The result is an inversion catching newer analysts. The indicators easiest to collect are the hashes, the IP addresses, and the domains. They cost an adversary the least to change, and they therefore tell an analyst the least. David Bianco's Pyramid of Pain names the asymmetry directly. At the base sit the throwaway artifacts an attacker rotates without a thought. At the top sit the behaviors and tradecraft painful to abandon, more revealing, and far harder to read. An attribution anchored to the base ages in hours or even days. One anchored to the top can hold for years, but only an analyst willing to do the harder reading ever gets there.
The landscape is also crowded, and almost everything in it is shared. A single government may field several offensive teams drawing from the same operators, loaders, and malware families. A tidy cluster of samples therefore rarely maps onto a single group. Commodity tooling circulates on criminal markets and sells to state and non-state buyers alike. Cobalt Strike, Metasploit derivatives, and leaked post-exploitation frameworks show up in intrusions run by wildly different hands.
Nowhere is this clearer in 2026 than ransomware. The ransomware-as-a-service model has turned the brand on the ransom note into one of the weakest attribution signals available. Affiliates rent the actual ransomware tooling, a dedicated leak site, and a negotiation platform from a highly sophisticated threat actor. They move to a competitor the next quarter when the economics shift. The same affiliate, using the same stolen credentials and the same exposed appliances, can deploy two different brands in two months. Following the logo merely tells you which service was rented. It says almost nothing about who was sitting behind the keyboard, which is the question worth answering.
Even behavior, the sturdiest layer, is eroding. Living-off-the-land tradecraft turns an operating system's own administrative utilities into the attacker's toolkit, leaving activity close to indistinguishable from legitimate work. The clearest modern example is VANGUARD PANDA, also known as Volt Typhoon across the industry. US agencies have described the China-nexus actor burrowing into critical infrastructure with built-in Windows tooling and valid accounts rather than malware. The abuse of legitimate remote monitoring and management (RMM) software does the same from the other direction, wrapping an intrusion in the exact tools a help desk uses every day.
Artificial intelligence raises the ceiling again. Threat actors now use large language models to write and translate their code, generate fluent lures in languages they do not speak, and stand up convincing personas at scale. The same capability points at attribution directly. A model can fabricate the stylistic tells analysts lean on, generate plausible false-flag code, and manufacture the digital exhaust of a persona who never existed. The deception in PyeongChang took skill and time. Some of that capability has been commoditized and is becoming insanely inexpensive.
Poisoned Views
Attribution is also constrained by who can see what, and this is the point vendors are least candid about. A national intelligence service collects across signals, human sources, and diplomatic channels. A commercial firm sees its own slice. Telemetry pooled across many customers works as a kind of signals intelligence, wide in some directions and blind in others. Vendor primary source intelligence rarely reaches the human reporting or diplomatic context a state can fold into the same judgment. That is not a reason to stay silent. It is a reason to mark the edge of what the collection supports and resist the pull to narrate past it.
Agreement does not automatically solve the problem. Three reports reaching the same conclusion may represent three independent lines of evidence. They may equally represent three views of the same telemetry, infrastructure, source reporting, or earlier attribution. Consensus can look stronger than the collection beneath it. Before counting corroboration, an analyst has to ask whether the evidence is actually independent or merely echoing.
The confusion is compounded by names. Every major vendor assigns its own cryptonym. One actor arrives as VANGUARD PANDA, as Volt Typhoon, and as several others depending on who is speaking. A reader trying to reconcile three reports can mistake one group for three or three for one. Recent cross-vendor efforts to map these names against each other help, but the proliferation itself is a hazard. Before anyone can argue about who did something, everyone has to agree on who they are even discussing.
Worse, the fraction you do see may be arranged for you. Deception is not an occasional complication layered onto attribution. It is an operating condition analysts have to assume can exist, because competent adversaries know their work may eventually be examined. PyeongChang showed a false flag planted in code. The same move works in infrastructure.
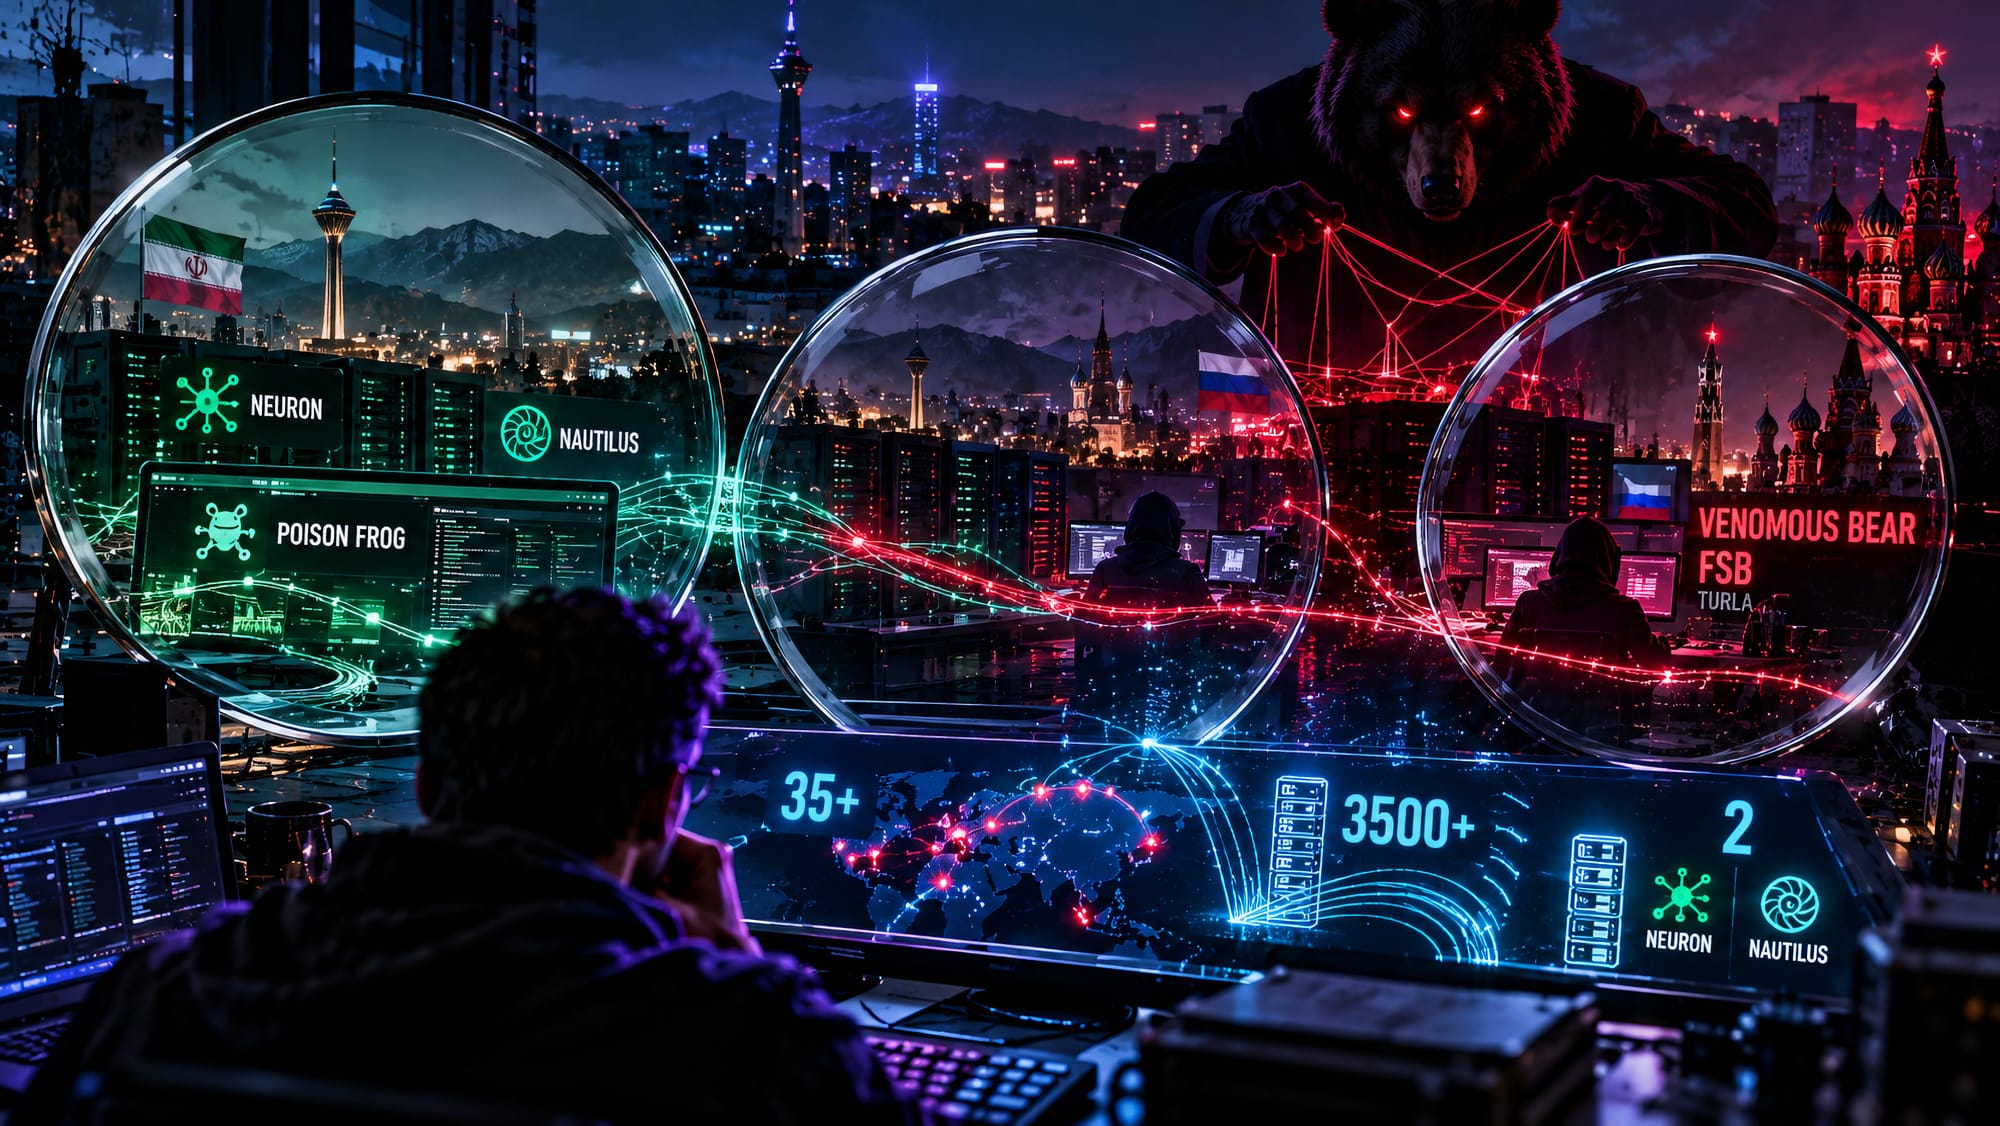
For a stretch, Russia's VENOMOUS BEAR, also known as Turla across the industry, ran operations through Iranian tooling and infrastructure associated with HELIX KITTEN, also known as OilRig. VENOMOUS BEAR had compromised parts of the Iranian operation to get there. Victims and first responders could therefore encounter Iranian infrastructure while the operator behind it was Russian. The British NCSC and US NSA eventually pulled the two apart. An adversary able to borrow another actor's infrastructure can borrow its attribution. An analyst who stops at the first plausible owner has done the adversary's work for free.
The modern variant is subtler. As purely technical indicators decay, analysts lean harder on victimology, the pattern of who gets targeted and when, as a strategic signal. That reasoning is powerful, and it is also a surface an adversary can shape. An actor who understands that investigators now read the target list can choose targets partly for how they will be read. Deception has climbed the pyramid alongside the analysis.
How Attribution Is Actually Built
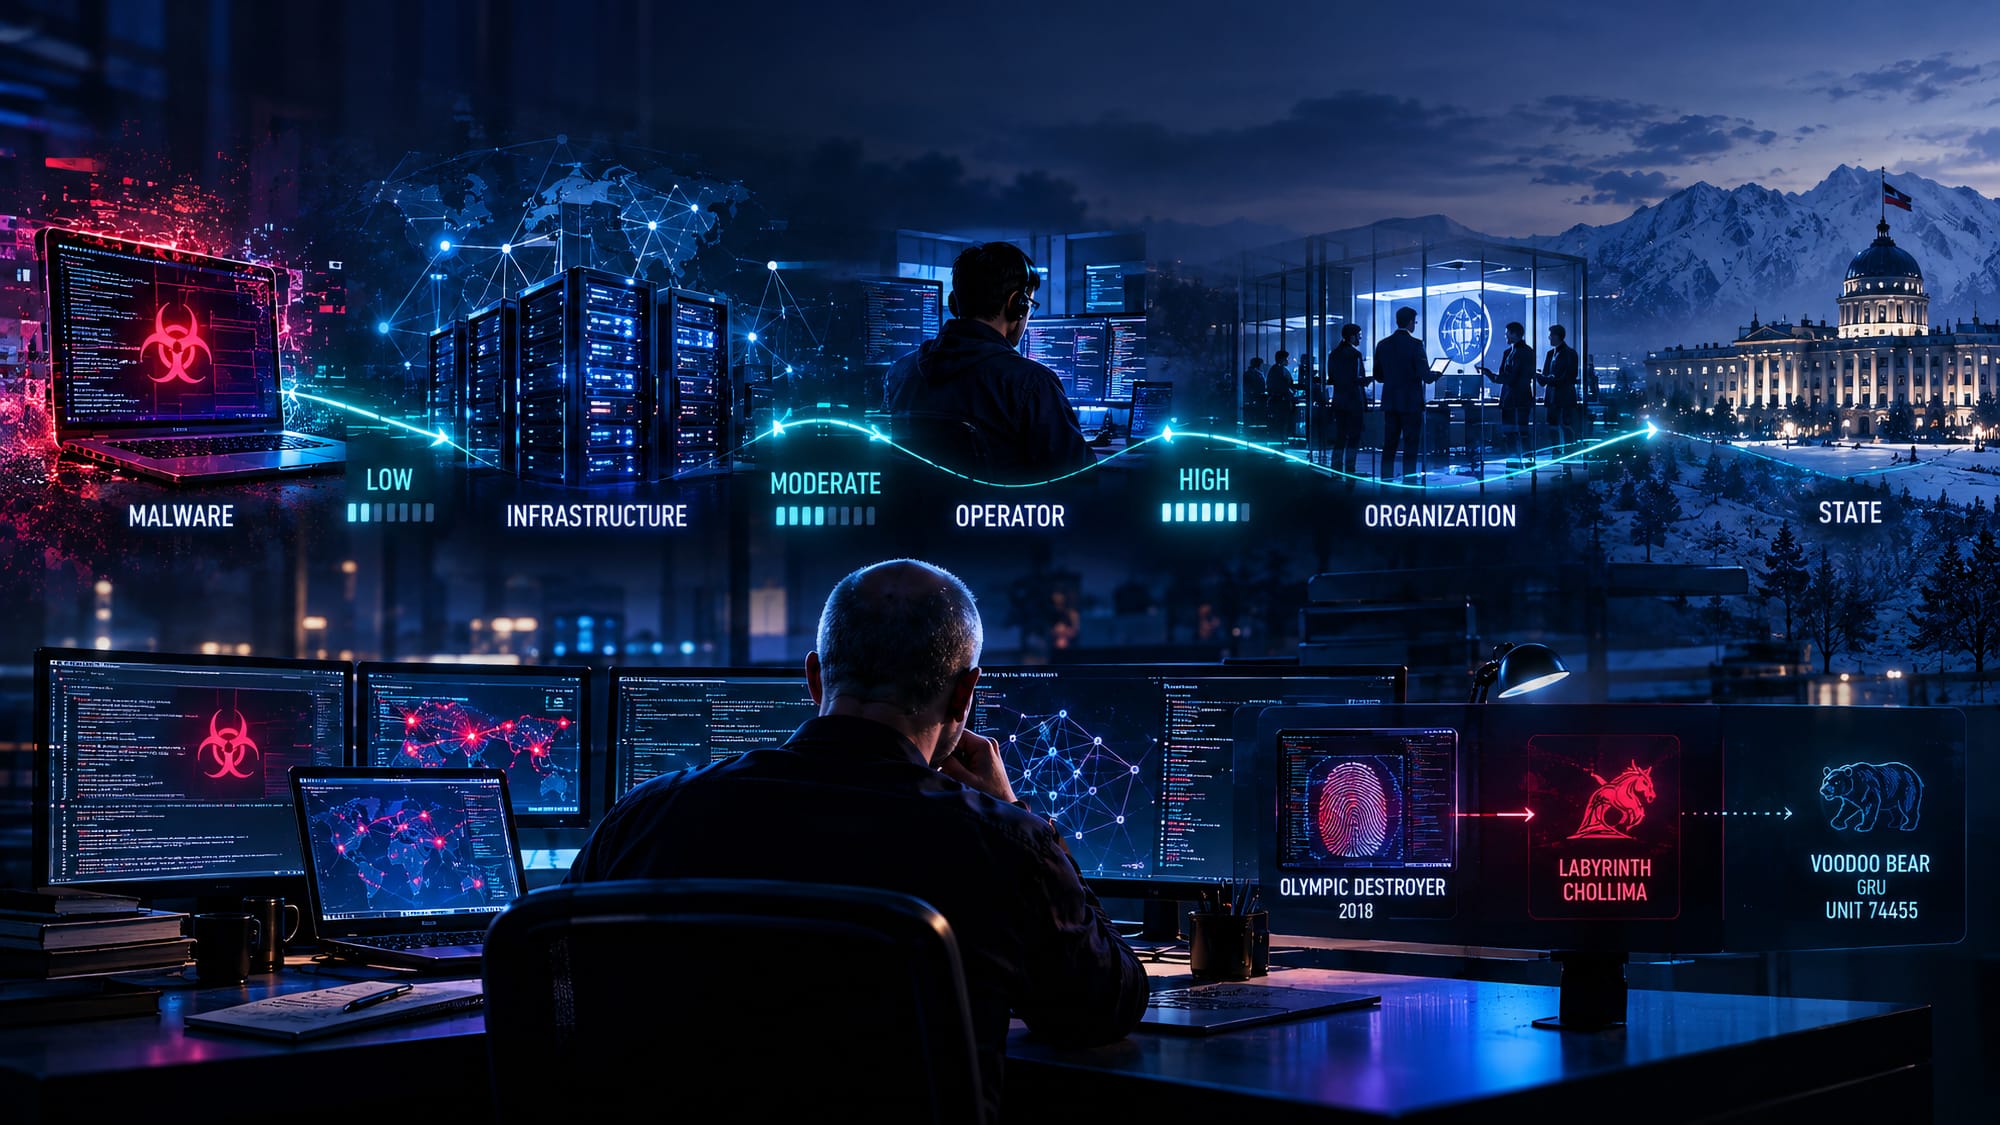
If the maze is this hostile, the honest response is method rather than confidence for its own sake. Serious attribution is layered, not binary. It helps to separate the machine from the persona, the human, and the organization behind them. Tying a sample to infrastructure is a technical finding. Tying that infrastructure to a persona, the persona to a person, and the person to a government is a far longer chain. Every link carries its own confidence. Thomas Rid and Ben Buchanan framed attribution as a craft of graduated judgment, not a single verdict. It works at tactical, operational, and strategic levels at once. Most public argument about it collapses those levels into one yes-or-no question they were never built to answer.
The first discipline is to stop asking who did it as though who were singular. The person who writes the malware may not operate it. The operator may rent infrastructure, work through a contractor, or serve an intelligence requirement set by an organization they never meet. The state benefiting from the collection may not have built any of the tooling.
How far that chain must run depends on the decision it has to support. A defender trying to stop an intrusion may only need to know the same operator has returned and what it is likely to do next. A government considering sanctions, an indictment, or a public accusation needs to travel much farther toward the organization, sponsor, and state. An attribution is complete when the evidence has answered the question the decision actually requires, not when it reaches a flag.
Structure keeps the chain honest. The Diamond Model forces an analyst to account for adversary, capability, infrastructure, and victim together rather than fixating on whichever is loudest. Analysis of Competing Hypotheses comes from Richards Heuer's work for the intelligence community. It requires building the case against a preferred conclusion as rigorously as the case for it. Both are forms of counter-intelligence an analyst applies to their own mind, and the PyeongChang deception is exactly what they defend against. Capable investigators followed the planted trail toward North Korea and China first. They did so not from carelessness, but because the trap was built for the shortcuts a hurried analyst takes.
The harder question is sometimes not what supports a hypothesis, but what should exist if the hypothesis were true and does not. Absence is weak evidence when collection is incomplete, but it still matters. Several absences can pull against an otherwise attractive conclusion. A target set refuses to fit, an operational rhythm breaks, infrastructure behaves unlike the supposed actor, or an expected behavior never appears. Mature attribution counts contradictions, not only matches.
Everything resolves into a confidence statement, and that statement is the deliverable. Low, moderate, or high compresses the entire chain into a signal a decision-maker can use without mistaking a lead for a conclusion. An attribution offered with no confidence level is weaker than one that states it, because it has concealed the one thing a reader most needs in order to weigh it.
A confidence label should not be mistaken for a probability score. High confidence does not secretly mean 90 percent likely, and moderate confidence is not a mathematical midpoint. Confidence describes how much trust the analyst places in the judgment. It reflects the quality, consistency, and limits of the evidence and reasoning underneath. Converting that into false numerical precision does not remove uncertainty. It only hides it behind arithmetic.
Myth: Attribution Delivers Absolute Certainty
The most damaging expectation is the simplest one. People expect attribution to end in proof. It does not, and it cannot. High confidence is a statement about the weight and consistency of evidence across several independent lines, not a claim of infallibility. It means the technical, contextual, and behavioral indicators converge. It means reasonable alternatives have been tested and found wanting, and the judgment is sound enough to act on. It never means the matter is closed beyond revision.
The trap is that even the most concrete-seeming evidence can be manufactured. A photograph of a building, or of an individual at a keyboard, feels like the end of the argument. It is also exactly the sort of artifact a capable adversary can stage, mislabel, or feed to an investigator through a compromised source. Olympic Destroyer's forged fingerprint is the same lesson in miniature. The more convincing a single piece of evidence looks, the more it earns the question of who benefits if you believe it.
WannaCry carried the same warning in a different form. When the ransomware tore through hospitals and companies in May 2017, spreading on the EternalBlue exploit, CVE-2017-0144, the clue that first cracked it was reused code. The Google researcher Neel Mehta spotted an overlap between the early WannaCry samples and malware tied years earlier to North Korea. The link was real, and the United States and United Kingdom eventually attributed the attack to Pyongyang. But reused code is also exactly what a forger copies into a false flag, which is why careful analysts treated the overlap as a strong lead rather than a verdict. The same artifact can be a signature or a plant. Only the surrounding evidence tells you which.
This is why confidence is a spectrum rather than a switch. Treating high confidence as certainty is how analysts get played, because it removes the very doubt that would have caught the deception. The goal is to measure uncertainty, state it, and act in proportion to it, not to escape it.
Myth: Attribution Is Instantaneous
Speed is the next false expectation, and the most seductive after a breach. A major incident creates enormous pressure to name someone inside the news cycle. Executives want an answer. The press wants a headline. The public wants a villain.
Speed does not automatically produce low confidence. What it usually removes is time to collect, contradict, and falsify. Early confidence therefore deserves more scrutiny rather than less. The failure is delivering an early judgment in the language of a settled one. The correction, when it comes, costs more than the delay would have. Rushed attributions often rest on partial collection, formed before contradicting evidence surfaces and before the first plausible story has been stress-tested.
There is a structural reason speed misleads. The evidence available in the first hours sits at the bottom of the Pyramid of Pain, the hashes, the addresses, the file names, the very layer an adversary can fake or borrow most easily. The behavioral and strategic signals that resist forgery take longer to collect and longer to read. So the earliest confident story is usually built on the least trustworthy material, which is backward from how confidence should accrue.
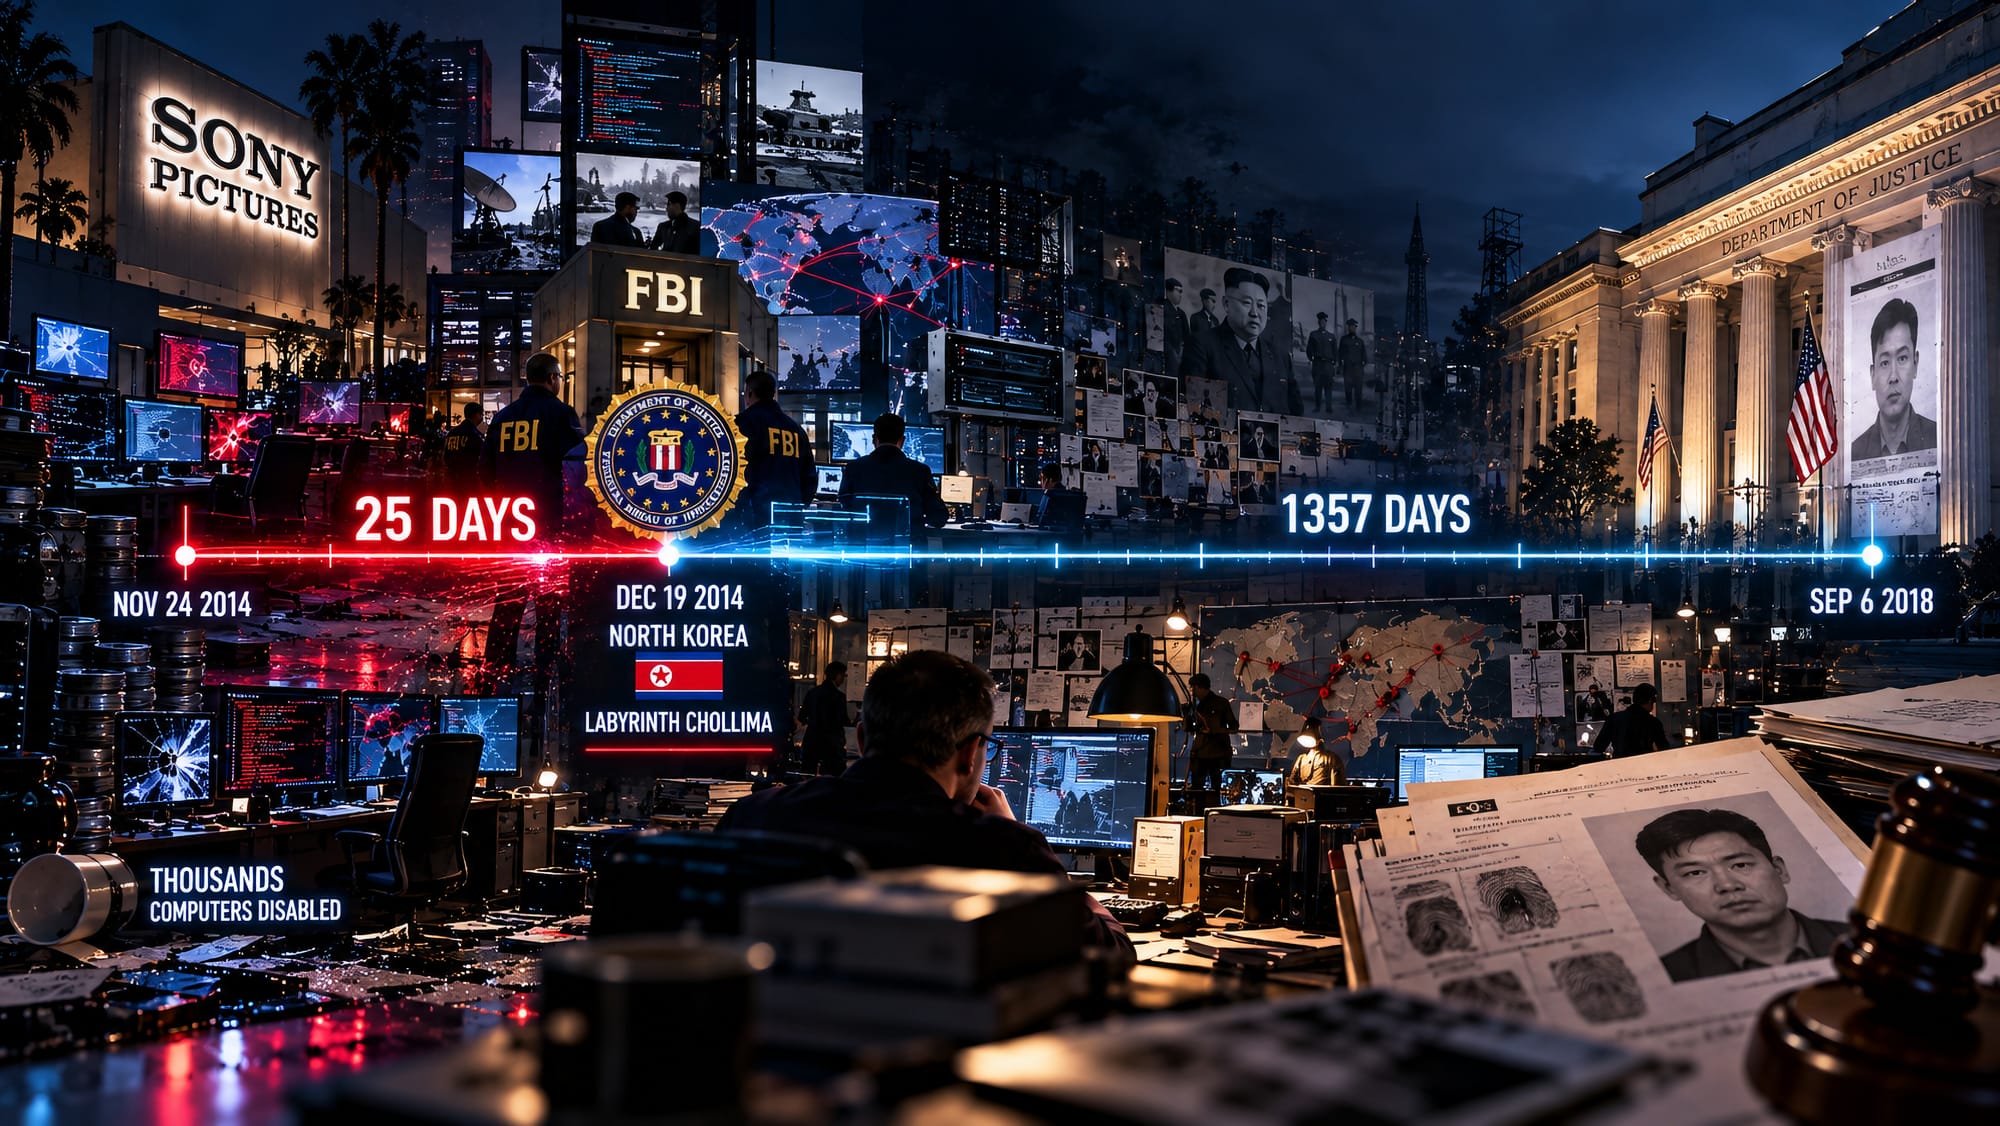
In late 2014, the attack on Sony Pictures put that pressure on open display. Within weeks the FBI publicly attributed the intrusion to North Korea, an unusually fast and unusually public call for the Bureau at the time. The reaction was immediate skepticism. Outside researchers floated insider and hacktivist theories and argued the released evidence was thin. The government held its position, and over the following years the picture firmed up, with a Lazarus developer named in a 2018 indictment. The fast call happened to hold. The speed still guaranteed a public brawl, and only the evidence disclosed with its confidence attached came through it intact.
Patience here is active. It means holding a finding at moderate confidence and continuing to collect. It means telling the people demanding an answer that the honest one is not available yet. In a domain built on deception, the analyst comfortable saying not yet is worth more than the one always ready with a name.
Myth: Attribution Is Only Technical
A related error treats attribution as an engineering problem, solved by collecting enough indicators of compromise. Technical evidence is indispensable and, on its own, half an argument. IP addresses, malware signatures, and logs are the most collectible evidence and, as the Pyramid of Pain makes plain, the most forgeable. Breadcrumbs can be planted. A reused tool can be a shared tool. A language artifact can be a decoy.
What converts technical data into attribution is context. Who gains from the operation, what was actually targeted, how the timing fits the state of relations between two governments, and whether the activity matches an actor's known strategic objectives. A piece of malware tells you how an intrusion happened. Only the geopolitical and historical picture tells you who would want it to happen, and why. Sometimes the two diverge. The technical trail points one way and the strategic context refuses to support it. The correct output is then not a forced answer but a lower confidence and a wider aperture.
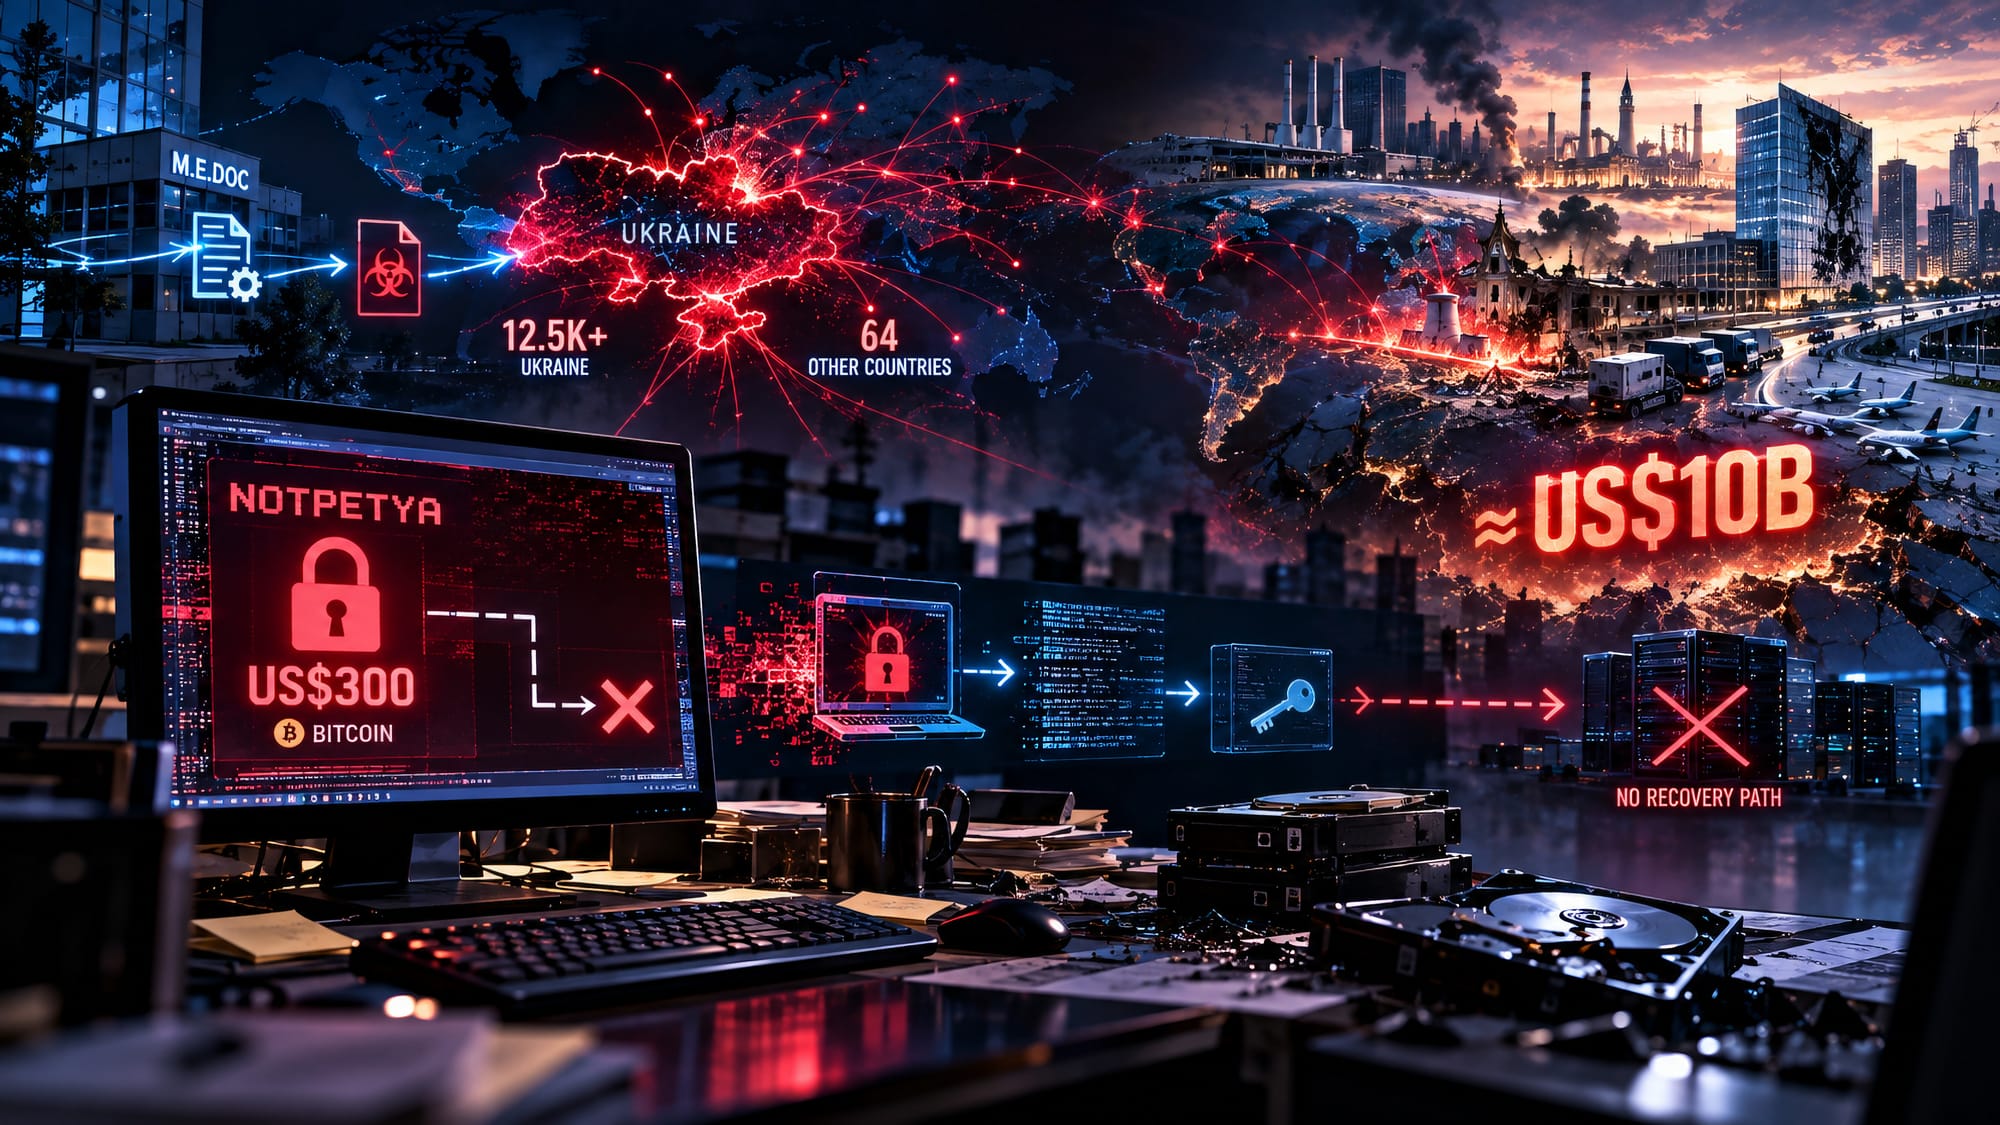
NotPetya showed how far the technical surface and the real intent can diverge. In June 2017 it spread from a compromised update to a Ukrainian accounting package called M.E.Doc, then tore outward using EternalBlue and stolen credentials. On the screen it looked like ransomware, complete with a ransom note and a payment demand. The technical surface said eCrime. The context said otherwise. The payment path was broken by design, recovery was never the point, and the blast radius centered on Ukraine before spilling into multinationals doing business there. Read through the targeting and the timing, the operation was a destructive attack dressed as crime, and governments later attributed it to VOODOO BEAR. The ransom note was the costume. The context was the tell.
Modern tradecraft makes this both worse and more important. As living-off-the-land techniques and shared tooling hollow out the technical layer, the contextual layer carries more of the weight. Victimology is the shape of a target set over time. It has become one of the strongest available signals, precisely because it is harder to fake at scale than a hash. Attribution is an analytic endeavor weaving the technical and the contextual together. Pull either thread out and the weave falls apart.
Myth: Attribution Is Finger-Pointing
Attribution is also widely assumed to exist for the sake of blame. Public naming does serve geopolitical purposes, indictments, sanctions, and the occasional statement meant to deter. But blame is a downstream use, not the purpose. Mistaking it for the purpose distorts the work.
The real value is defensive. Foresight comes from knowing which adversary is in the network, what it wants, what it can do, and what it is likely to do next. An actor's identity carries its whole history, its preferred access routes, its tooling, its patience, and its objectives. That history lets a defender anticipate the next move instead of only cleaning up the last one. Attribution failing to change how a defender prepares was performed for the wrong reason.
The SolarWinds campaign makes the split visible. The sanctions the United States placed on Russia were the blame, the public and political act. The lasting value to defenders was different. Naming the intrusion to COZY BEAR, also known as APT29 across the industry, the SVR actor behind the campaign, handed every other potential target a profile, a preference for patient, quiet espionage, for living inside trusted identity and cloud systems rather than dropping noisy malware. A defender who internalizes that profile knows where to look before COZY BEAR arrives. The indictment punishes the last operation. The actor profile helps you survive the next one.
Confidence constrains what a finding can be used for, but it does not mechanically decide the action. A low-confidence attribution may still justify a cheap and reversible hunt across the environment. A high-confidence one may still be insufficient for a public accusation whose cost of error is strategic. The threshold depends not only on confidence, but on consequence, reversibility, and what happens if the judgment is wrong. Intelligence informs the decision without making it.
Myth: Attribution Is Always Public
Another assumption is that a finished attribution should be announced. Public attribution is a real instrument, able to impose cost and shape behavior, but it is one to use with discernment, not a reflex.
Disclosure carries its own risks. It can burn the sources and methods behind the finding, teaching an adversary exactly what the defender can see. It can escalate a conflict between states. It can invite retaliation against the victim who chose to speak. A low or moderate confidence attribution announced loudly can inflict more damage than the intrusion it describes. An incorrect assessment is very hard to walk back.
The cost of speaking is not abstract. A detailed public report is also a free lesson for the adversary. It tells them which of their tools were caught, which infrastructure was mapped, and often what the defender must have been able to see to catch it. Name an actor with enough technical detail and the tradecraft can change within weeks, the burned toolkit retired and the exposed infrastructure abandoned. Sometimes that disruption is the goal. Sometimes it simply trades a short headline for a harder target next quarter.
When public attribution is done well, it looks deliberate rather than reflexive. In October 2018 the United Kingdom and a group of allies named Russia's GRU for a string of operations in a single coordinated release, timed and backed by partner governments. That is public attribution used as an instrument, chosen for a reason, aligned across capitals, and delivered with the evidence and confidence spelled out. It is the opposite of a vendor racing a blog post out the door hours after an incident to plant a flag in the ground. The decision to speak carried as much weight as the finding itself.
This is where confidence becomes an ethical compass as much as an analytical one. A high-confidence finding with a clear defensive or deterrent purpose may justify going public. A weaker one is often better held, driving internal defense and further collection while the picture firms up. Deciding what to withhold is part of the discipline, not a loss of nerve. The choice to publish should be as deliberate as the attribution itself.
Myth: Attribution Is Immune To Bias
Then there is the belief that rigor makes an analyst objective. It does not. Confirmation bias pulls toward the evidence supporting a favored theory. Anchoring locks onto the first plausible actor and reinterprets everything after through that lens. These are not failures of intelligence. They are properties of human cognition, and the most dangerous adversaries design for them.
Olympic Destroyer is the standing proof. The deception was not aimed at machines. It was aimed at investigators, layered to reward the first story that fit. The flags pointed at North Korea, with echoes suggesting China. Skilled researchers chased those similarities before the GRU came into view. The truth surfaced only because multiple teams kept re-examining evidence the convenient early reading had already explained away. A less stubborn process would have stopped at the planted answer and called it high confidence.
Look closely at why the trap worked. The forged fingerprint did not just point somewhere, it pointed somewhere plausible. North Korea had motive and recent history, so the planted answer slotted neatly into what analysts already half expected. That is the engine of anchoring, a first impression dressed in prior belief, and it is far stronger than a random false lead. The most effective deception does not fight an analyst's expectations. It rents them.
Analysis of Competing Hypotheses, red-teaming, and a second set of eyes with permission to disagree all exist to catch the analyst's own assumptions before an adversary exploits them. The useful posture is skeptical and open at once. It is skeptical enough to distrust the convenient conclusion, and open enough to follow the evidence toward an answer no one expected. An analyst who believes they are immune to bias has already lost to it.
Myth: Attribution Is Settled Once Made
The last myth is that an attribution, once published, is finished. It is not a verdict handed down. It is a standing judgment, alive to new information.
Evidence arrives late. An indictment, a defector, a competitor's report, or a shift in the geopolitics can raise a finding's confidence, lower it, or overturn it. Infrastructure once thought unique turns out to be shared. A group believed distinct turns out to be a cluster, or two groups thought separate collapse into one. Treating last year's attribution as permanent is how stale assessments quietly mislead the defenses built on them.
The North Korean problem shows attribution maturing rather than freezing. For years the industry filed almost everything from the regime under a single umbrella name. As collection deepened, that umbrella came apart into distinct threat actor groups with different missions, the financial theft teams separated from the espionage teams separated from the destructive ones. None of the early work was wasted. It was refined, as a group once treated as one hand resolved into several. An analyst who still treats the regime as a single actor is working from a map the territory outgrew.
Revision is the system working as intended. A sound assessment is written to be revised. Its confidence and its reasoning are exposed, so the next analyst can see precisely what would have to change to move it. Attribution is an ongoing dialogue between the evidence and the analyst, demanding both rigor and the humility to say an earlier judgment no longer holds.
What You Control
None of this makes attribution hopeless. The loudest voices calling it futile are usually selling a different kind of certainty. PyeongChang was attributed correctly in the end. Not by a tool, and not on the first day, but by people who refused the tidy answer and kept laying the thread behind them.
The adversary always builds the maze. Now it builds the maze faster, with shared tooling, living-off-the-land techniques, and machines able to manufacture both code and personas. What the analyst controls is the walk. Mark the turns taken on weak evidence. State the confidence at every link. Say aloud how far the thread actually reaches, and be ready to retrace it when the ground shifts.
You cannot stop an adversary from planting a convincing clue. You can stop that clue from carrying more analytical weight than it has earned.
That honesty, written down as a confidence statement, is the thread leading back out of the labyrinth. The adversary can shape the evidence you see. The analyst controls how far that evidence is allowed to carry the conclusion. Attribution is not the elimination of uncertainty. It is the discipline of refusing to claim more than the evidence has earned.
That discipline is what separates intelligence from a guess wearing someone else's flag.