
Latest Intelligence

Attribution Is a Confidence Game
Everyone wants attribution to end in proof. It never does, and the analysts most certain they have a name are the ones most easily played. Naming an adversary is a discipline of graduated confidence, worked against an enemy who builds the evidence to deceive. Seven myths, taken apart.


ShinyHunters Survived Every Arrest but Now Someone Is Talking
Jordanian authorities detained Rey, an admin who seized the ShinyHunters brand, and he is reportedly helping the FBI. Jailing a member never killed the brand. The leak sites are already back. But a cooperating insider attacks the one thing the collective cannot do without. Trust between its members.

Arresting One Hacker Does Not Kill a Collective
Dutch police arrested a 24-year-old in the ShinyHunters investigation, and the case looks less like a clean win the closer you read it. The evidence tying him to the breaches is a reused alias and a disputed voice, against a collective that has no membership and publicly laughed off the arrest.

Cyber Crime Does Not End at the Intrusion
Everyone treats the attack as the event. The phishing email, the ransomware, the stolen keys. But financially motivated cyber crime does not end at access. The money still has to move, and the blockchain keeps a permanent record of where it went.
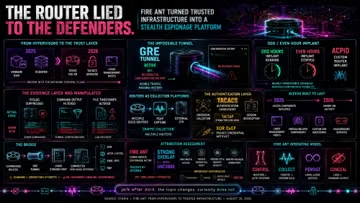
The Most Dangerous Intrusion Is the One That Turns the Alarms Off
Most attackers try not to get caught. Fire Ant breaks in, then disables the cameras and edits the tapes. The China-nexus actor turned Cisco routers into spying platforms, suppressed the logs, and altered what admins were even allowed to see.
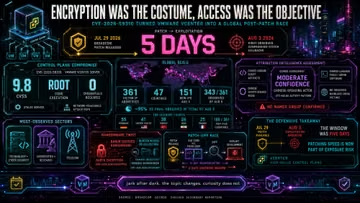
Encryption Was the Costume, Access Was the Objective
A critical VMware vCenter flaw was patched on July 29. Five days later, a suspected China-nexus actor was already inside, across 361 IPs in 47 countries. It ended in ransomware, but QUIRSO says that was likely a smokescreen. The encryption was the costume. The access was the objective.