

Latest Reports
Campaign Analysis

Somebody Is Arming China’s Spies From Panama to Prague
A fake Chrome warning only chosen visitors see, a backdoor inside Latin American carriers, and a Linux rootkit in Asia share one malware framework. Check Point says a supplier arms several Chinese threat actors, ESET sees one adversary, and Trend has caught access itself changing hands.

Turla Spies on Moscow’s Ally and NATO with Nothing to Seize
Turla hid Cereal inside the Exchange servers of a Kazakh and a Romanian government organization, collecting on a Moscow treaty ally and on NATO and EU correspondence without a single command-and-control server, which leaves takedowns, blocklists, and the EU sanctions of July with nothing to seize.

Someone Is Reselling Your AI Key and Billing You for It
Sixteen AI developer platforms disclosed breaches in five weeks. The best-documented ones trace to credentials earlier cleanups left valid, and the stolen keys fed resellers whose buyers range from discount hunters to labs accused of distillation, while victims pay for every call made in their name.

North Korea Is Headhunting the Engineers Who Build Ukraine’s Drones
North Korea is sending fake recruiters after the engineers building Europe’s drones while poisoning the open-source code they rely on. Russia already teaches Pyongyang mass production at Alabuga, so why steal from Europe? Five hypotheses, an ally under surveillance, and the doors Europe keeps open.

ARTEX Already Jumped From eCrime to Espionage
Hunt.io recovered the entire ARTEX workbench from exposed servers, the credentials, the AI routing, the skills, and the reverse SSH tunnels behind South Korea’s bank breaches. The reconstruction was remarkable, and it changed nothing. The framework had already reached Storm-0940 and VAPOR PANDA.

COZY BEAR Empties Phones With Exploits Apple Already Fixed
A visitor opens a trusted Ukrainian website, taps nothing, and loses the contents of a phone. COZY BEAR poisoned a widely used analytics script, then hit unpatched phones with exploits Apple and Google had already fixed. The page is legitimate. The exploit is old. The intelligence is fresh.
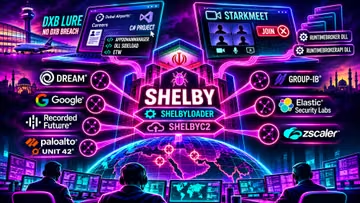
DarkBlinders Shows Why Threat Actor Naming is a Hall of Mirrors
A fake job from Dubai Airports, a video app that never works, and a gigabyte gone from a Kurdish government cloud. One Iran-nexus espionage operation carries seven vendor names, runs its command-and-control through GitHub, and keeps collecting in the gap between what the industry can see and prove.

Tomorrow’s Encryption Is Already Protecting North Korean Malware
NIST built ML-KEM to protect the world’s data from a future quantum computer. North Korea’s Lazarus found an advantage in the present, running the same post-quantum mathematics inside operational malware before most enterprises have migrated. The standard did not fail. It worked for the wrong side.

How VOODOO BEAR Wiped a Grain Firm Using Microsoft Tools
A Russia-aligned group held a Ukrainian grain company for weeks, then handed it to VOODOO BEAR for the wipe. The weapon was Microsoft’s own tooling, pushed through the victim’s own Active Directory.

FANCY BEAR is Mapping How Fast NATO Can Rebuild
A GRU actor spent two months inside a NATO naval shipbuilder, reached a law enforcement agency and an aircraft engine maker alongside it, and did it with a Word macro and off-the-shelf tools. The prize was never the fleet. It was the industrial base deciding how fast the alliance can rebuild.