
Latest Intelligence

Fear of a Breach Is How The Gentlemen Get Paid
The Gentlemen added ten names to its dedicated leak site this month, including Deloitte, KFC, and MoneyGram. None has confirmed a breach and no files have appeared. The ransomware-as-a-service operation does not need the claims proven. It only needs the accusation to travel faster than the evidence.

ShinyHunters Survived Every Arrest but Now Someone Is Talking
Jordanian authorities detained Rey, an admin who seized the ShinyHunters brand, and he is reportedly helping the FBI. Jailing a member never killed the brand. The leak sites are already back. But a cooperating insider attacks the one thing the collective cannot do without. Trust between its members.

Arresting One Hacker Does Not Kill a Collective
Dutch police arrested a 24-year-old in the ShinyHunters investigation, and the case looks less like a clean win the closer you read it. The evidence tying him to the breaches is a reused alias and a disputed voice, against a collective that has no membership and publicly laughed off the arrest.

Revolut Says No One Demanded a Ransom, the Internet Disagrees
A group claiming the Revolut breach demanded US$3 million in Monero, with a 24-hour countdown clock, and never once contacted Revolut directly. The demand was public from the start. That is the inversion worth noticing. The pressure was not a private negotiation. It was everyone else watching.

Four Dollars Is All the AI Costs to Break Into Your Company
An affiliate of The Gentlemen ran an automated AI pipeline that broke into 30-plus companies, stole 3.1TB, and wrote the ransom demands itself. The AI cost per victim was as little as 40 cents. That is not the whole operation, but it is the part that used to take a skilled human days.

A Human Set the Goal, AI Did the Breach in 10 Hours
A ransomware operator used frontier AI to break into an enterprise network and seize root in under 10 hours, work normally taking a human red team two weeks. No zero-day, no novel malware, just known techniques at machine speed. The one thing stopping it was a control forcing a human to sign off.

McKesson Was Breached by a Phone Call, Not a Zero-Day
ShinyHunters claims 284 million patient records stolen from McKesson, which moves a third of North America's prescriptions. Read that carefully: records, not patients. McKesson confirmed a breach, not the number. The healthcare data now sits behind a login a convincing voice can open.
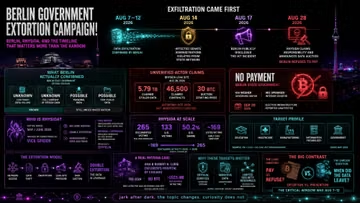
Berlin Won't Pay VICE SPIDER and Here Is Why It Changes Nothing
Berlin refused to pay the ransomware crew that breached its network. Good. But the data was already gone a week before anyone pulled the plug. Refusing to pay is the honorable call, and it does not save you. The failure that mattered happened quietly, days earlier.
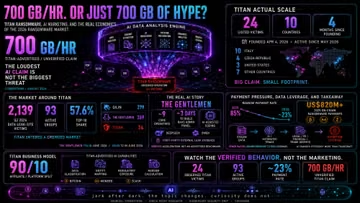
The Ransomware Group Nobody Should Be Worried About Yet
TITAN says its AI reads 700GB of stolen data an hour. The number is unverified marketing, and the group is a nobody: 24 victims in four months against leaders posting 100 a month. The real AI-in-ransomware story is quieter, and it is not TITAN.