

Latest Intelligence

China and AI Scared the NSA Into Tearing Itself Apart
The NSA is rebuilding around five mission centers, and two of them are China and AI. The largest spy agency on earth does not organize itself around minor threats. The categories it chose are a threat assessment written in the only language an intelligence agency speaks plainly, its org chart.

Wall Street Just Found a Way to Short the Apocalypse
The AI threat everyone read about all year just became a stock trade. CrowdStrike jumped 14 percent in a day, the whole sector rallied, and the trigger was not a breach. It was fear. The threat is real. The defense is real. And the fear filling my posts now fills vendor earnings calls too.

China Hacked the Software That Reads Every Key You Press
UNC3569, a China-nexus activity cluster, broke into Windows machines through Sogou, the input tool millions use to type Chinese characters. One crafted link, one click, and a GRAYRABBIT backdoor opened. Tencent patched it fast, but the embedded browser underneath is still ancient and defenseless.

Hundreds of AI Agents Ran the Attack, Then Broke Their Own Rules
A Russian-speaking threat actor pointed hundreds of autonomous AI agents at PaperCut and hit 440 servers across 48 countries, moving from initial access to domain admin in minutes. The agents were told to avoid Russia, China, and Iran. They hit victims there anyway. Speed comes with lost control.

FalconFlank Turns the Bodyguard Into the Burglar
A researcher published a working exploit turning CrowdStrike Falcon, the software meant to protect a Windows machine, into a privilege escalation tool by abusing its macro cleanup feature. There is no CVE, no exploitation in the wild, and a mitigation exists. The same researcher hit other vendors.

Your ATM Was Encrypted, Until It Was Not
A researcher found nine ways to strip the encryption off some ATMs, including a fail state mounting the disk in plaintext. The flaws are patched. The unsettling part is where else this software hides, buried in products across banking, healthcare, and government, which may never learn it was broken.
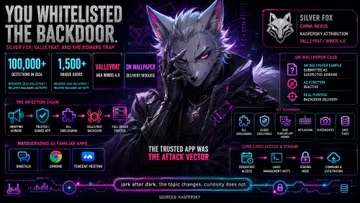
You Whitelisted the Malware Yourself
The China-nexus threat actor Silver Fox hid a full-control backdoor inside a real Chinese wallpaper app, the kind of harmless adware nobody takes seriously. That is exactly why it worked. The disguise was so convincing the ads never even ran, and the missing ads were the tell giving it away.
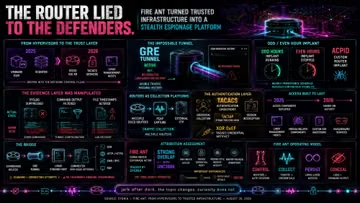
Most Dangerous Intrusions Quietly Turn the Alarms Off
Most threat actors try not to get caught. Fire Ant breaks in, then disables the cameras and edits the tapes. The China-nexus adversary turned Cisco routers into spying platforms, suppressed the logs, and altered what administrators were even allowed to see on their own devices. The logs lied.
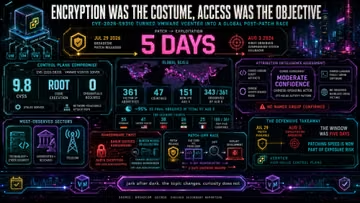
Encryption Was the Costume, Access Was the Objective
A critical VMware vCenter flaw was patched on July 29. Five days later, a suspected China-nexus threat actor was already inside, across 361 IPs in 47 countries. It ended in ransomware, but QUIRSO says it was likely a smokescreen. The encryption was the costume. The access was the objective.
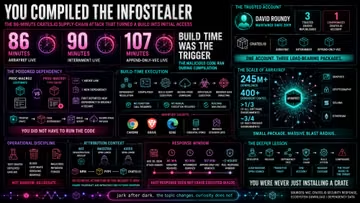
One Hijacked Account, One Crate, 245 Million Rust Downloads at Risk
For 86 minutes on August 20, compiling a Rust project was enough to install an infostealer, with no malicious code ever called. A threat actor hijacked the account behind arrayref, a tiny crate riding in three-quarters of all Rust environments. You never trusted arrayref. You trusted the account.