
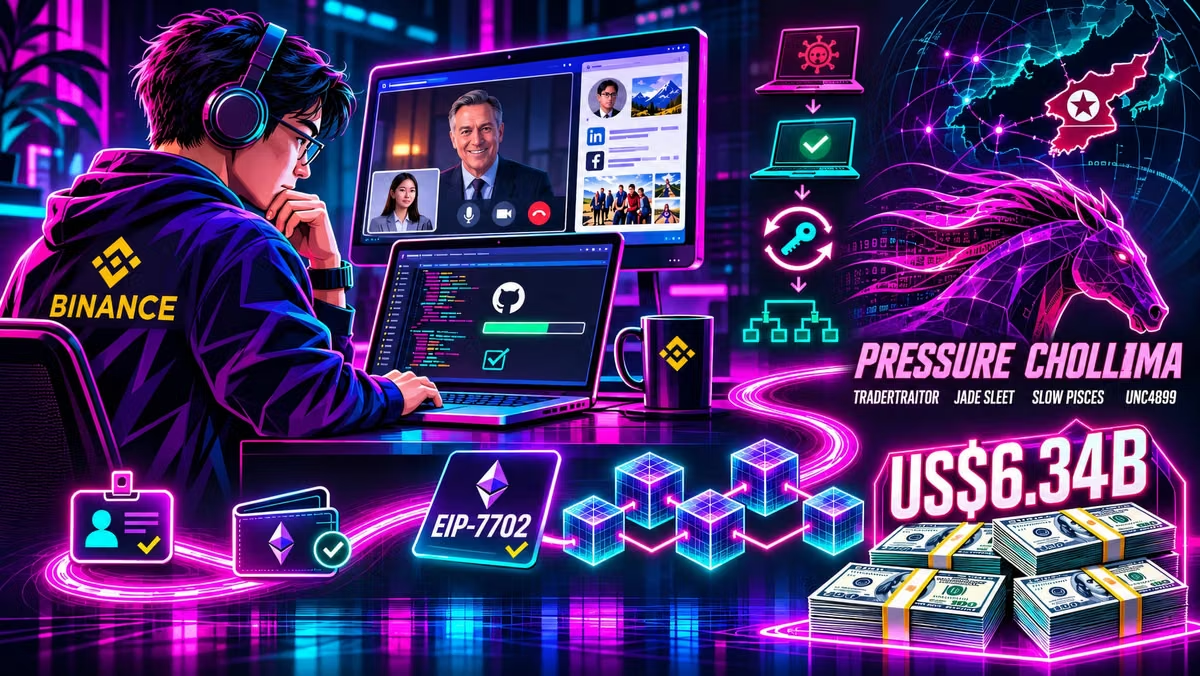
A software engineer reaches the end of a second-round interview in a chat app. The first round had gone well, a live video call with an HR representative who shared a social media profile full of personal photos and videos, the kind of ordinary detail making a stranger feel real. Now the company's supposed CEO wants to see his work. Near the end, the engineer is asked to pull a coding assignment from an online repository and run it on his work laptop.
He does. Code buried inside the project executes during setup. The interview has done its job. North Korea now has the foothold Binance does not see.
This updates our earlier coverage. North Korea drained Binance of US$6.3 billion in a mere twenty minutes and the follow-up noting the FBI named the thief while Binance still could not explain the theft. That second piece left one question open. How. On November 3 Binance published its own preliminary incident report, and the answer is more unsettling than the silence it replaces. Binance says an independent review is still forthcoming, so this is the company's current reconstruction rather than the final forensic word.
Anatomy of a Breach
The operation began before the fake interview. Binance traces an earlier compromise to June 2026, when a wallet DevOps engineer searched for a popular AI coding tool and downloaded a tampered Homebrew installation. Binance's security team caught the anomaly. They replaced the device and rotated the related credentials.
What they could not rotate was knowledge.
By the time Binance removed the access, PRESSURE CHOLLIMA had learned the engineer's role and the identities of colleagues around the wallet infrastructure team. A laptop can be replaced. A credential can be revoked. An organizational map cannot. The first compromise had stopped being access and had become reconnaissance.
That intelligence paid off in September. The adversary approached a second engineer whose job-platform profile advertised his Binance experience, posing as a Project Director at a company existing only for the operation. The fake recruiter arranged two interviews, the first with an alleged HR representative and the second with an ostensible CEO.
Trust was deliberately manufactured. The HR representative ran a live video call and shared personal social media to look human, a step Binance itself calls more advanced than the social engineering it had seen before. Entry is a person, not a zero-day, and the person was selected for the access surrounding him.
The second interview moved to a popular chat app. Near its end, the supposed CEO gave the engineer a coding assignment to download from a repository and run on his work machine.
Binance had already been fighting this campaign class all year. It says its security team detected and prevented 57 suspected North Korea-linked cyber threats during 2026, including fake interviews, malicious developer tools, compromised packages, browser extensions, fake meeting applications, and credential theft. The number exposes the asymmetry. More than fifty-seven successful defenses can work. The adversary still needs only one attack chain to survive long enough.
The malicious assignment delivered custom malware Binance calls "0-day malware," by which it means only that the endpoint protection did not detect it at the time. That describes a detection gap, not an exploited vulnerability. The report identifies no zero-day CVE, no privilege-escalation flaw, and no published hole in macOS or pyenv behind the compromise.
The implant hides inside trusted developer machinery. It creates a 3,414-byte malicious pyenv_ component inside the Homebrew directory, deletes the legitimate 3,344-byte pyenv, renames the replacement, rebuilds the symbolic link, and spawns zsh. The poisoned component can execute commands from an attacker-controlled server. Binance says the code used obfuscation and evasion techniques, then concealed activity and removed traces after execution. Classic sophisticated threat actor behavior. Make no mistake, DPRK is highly advanced, as evidenced by this operation and more.
The path itself helps explain why the attack is uncomfortable. /opt/homebrew is the default Homebrew prefix on Apple Silicon Macs, and Homebrew is built around a local trust model in which its owning account can manage software without sudo. A developer persuaded to execute malicious code may already possess enough privileges to modify the tools living there. No privilege-escalation exploit is described. The adversary makes malicious behavior look like the sort of developer activity the machine exists to perform.
What remains unanswered is why behavioral controls did not catch what signatures missed. Binance does not identify its endpoint security vendor, the policies applied to this machine, any developer exclusions, or the telemetry available during the compromise. It has not published malware hashes, C2 infrastructure, a family name, or a complete reverse engineering report. For now, the public malware story ends with a poisoned developer utility, a shell, an external server, and a security stack that was unable to stop North Korea.
Then the operation turned Binance's own infrastructure against itself. On October 20 the adversary used Engineer B's compromised computer and an internal AI tool to gain control over Wallet DevOps Engineer A and another wallet software engineer, Engineer C. It soon discovered a container deployment permission token on Engineer A's computer.
The AI detail may be one of the most important unanswered questions in the report. Binance does not name the tool, describe its permission model, or explain how it helped one compromised endpoint reach two more engineers. Its remediation is revealing. Binance rebuilt the affected AI tool and strengthened its access controls afterward. The system became part of the attack path, but the public report still does not tell us how much authority it carried.
This is also where the idea of a developer laptop as an ordinary endpoint breaks down. Engineer A's machine held deployment authority. Engineer B's machine could interact with an internal AI system capable of reaching colleagues. Engineer C sat inside the path toward wallet operations. In modern DevOps, the laptop on the desk can be a portable control plane for production.
On October 29, between 17:15 and 19:56 UTC, the adversary accessed Engineer C's computer, used credentials stolen from Engineer A, deployed a container, and triggered the script launching the theft. The published attack chain contained no exotic exploit at its center. Stolen credentials let the adversary log in as the people who already held the keys.
Draining Past Containment
What followed was fast and, for the first containment moves, impossible to stop completely. Between 20:05 and 20:09 UTC, five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address. Solana and Optimism wallets moved roughly 970,500 SOL and 44.2 million OP. An internal alert fired on the large transfers. Then 18,270 BTC left.
The adversary reached Ethereum through EIP-7702, and the control problem changed shape. EIP-7702 allows an externally owned account to delegate certain execution rights to smart-contract code without exposing its private key. Binance says the threat actor used its signing service to grant an attacker-controlled contract partial execution rights over the Binance14 hot wallet.
Binance describes fifty signing operations intended to manipulate the account nonce and establish malicious delegations. The blockchain gives a more precise picture. One type-4 Ethereum transaction carried fifty valid EIP-7702 authorizations signed by Binance14, all pointing to the same attacker-controlled contract and spanning fifty consecutive nonce values from 18,914,775 through 18,914,824. Binance14 was processing transactions fast enough for its nonce to keep moving. When Ethereum evaluated the authorizations, nonce 18,914,809 matched the wallet's live state and took effect. The other forty-nine were ignored. PRESSURE CHOLLIMA had effectively sprayed the moving nonce range, giving itself fifty chances for one permission to land.
The harder question sits inside Binance. Ethereum did not bypass the wallet's authority. It verified a valid Binance14 signature and behaved exactly as EIP-7702 requires. Somehow, the compromised signing path had produced fifty authorizations from the same institutional hot wallet to the same attacker-controlled delegate. Binance now says it is reviewing its signing-policy coverage and hot-wallet controls, but its report does not explain what policy allowed those signatures to be generated or why the pattern did not trigger an alert before one reached the blockchain.
Once it did, suspending withdrawals could no longer stop the whole attack. The malicious delegation already existed as Ethereum state and operated outside Binance's normal withdrawal infrastructure. The company could switch off services it owned. It could not simply delete an authorization the blockchain had already accepted.
The hot wallet also used Multi-Party Computation (MPC), and Binance says there is no evidence of a leaked private key. By design, MPC removes the single key an attacker might steal. During containment, that same design meant there was no single key Binance could reach for to immediately revoke the malicious delegation. The team had to develop a specialized procedure and send a new on-chain authorization.
MPC had removed a single point of cryptographic failure. It had also removed the shortcut of single-key recovery.
At 23:56 UTC the final unauthorized transfer, 2,961.9 ETH, was confirmed on-chain. Fourteen minutes later, at 00:10 UTC on October 30, Binance sent a new authorization from Binance14 to the zero address and cleared the delegation code.
That boundary is easy to miss. The incident began inside corporate infrastructure but part of the containment problem eventually lived somewhere Binance did not control. Once compromised authority became blockchain state, incident response itself had to cross onto the blockchain to take the authority back.
Roughly US$6.34 billion in assets were affected. Binance says about US$2.85 billion was later frozen or intercepted. It reported roughly 98 percent of impacted token assets replenished by October 31 using its own resources.
Two Record Heists
CrowdStrike tracks the DPRK cryptocurrency-theft specialist adversary as PRESSURE CHOLLIMA. Other vendors in the security community use different names, such as TraderTraitor, Jade Sleet, Slow Pisces, UNC4899, and Mata. CrowdStrike formally separated PRESSURE CHOLLIMA from the broader LABYRINTH CHOLLIMA lineage in January 2026 after reassessing years of DPRK activity.
CrowdStrike assesses PRESSURE CHOLLIMA operations likely diverged around February 2019. The adversary specializes in high-risk, high-reward cryptocurrency theft and increasingly uses malicious Node.js and Python projects against developers. Recruitment lures and poisoned development environments sit comfortably inside the tradecraft.
The FBI calls both the February 2025 Bybit theft and the October 2026 Binance theft TraderTraitor activity. CrowdStrike maps TraderTraitor to PRESSURE CHOLLIMA. On those mappings, this single adversary is now responsible for the two largest cryptocurrency thefts on record. Bybit held the record at roughly US$1.5 billion. Binance broke it roughly twenty months later by more than four times.
The geopolitical scale is difficult to overstate. The United States, Japan, and South Korea have repeatedly warned that DPRK cryptocurrency theft generates illicit revenue for North Korea's unlawful weapons of mass destruction and ballistic-missile programs. The Multilateral Sanctions Monitoring Team (MSMT) attributed at least US$2.8 billion in cryptocurrency theft to North Korea with high confidence between January 2024 and September 2025.
Binance alone involved US$6.34 billion.
Even after the roughly US$2.85 billion Binance says was frozen or intercepted, about US$3.49 billion remained outside that total at the time of the report. One operation had already left more value unfrozen or unintercepted than DPRK's high-confidence cryptocurrency theft total across the twenty-one-month window the MSMT examined. A fake interview on a developer laptop had become a proliferation-financing problem measured in billions.
It is difficult not to think about the engineer at the center of this. Binance has not blamed him publicly, and nothing in the report suggests he knew what the assignment really was. The task looked like an ordinary job interview exercise, and completing it turned one laptop into the entry point for a theft measured in billions. Whatever the company concludes internally, the weight is hard to imagine, a single decision becoming the opening PRESSURE CHOLLIMA used to reach the systems behind the largest cryptocurrency theft in history. The adversary engineered the deception. The engineer has to live with what it led to.
There is an uncomfortable lesson underneath the sympathy. The assignment came from another company, and the engineer ran it on a Binance work machine. Whatever the acceptable use policy said, that should never have happened. A job interview is personal activity, and courting another employer sits even further outside the purpose of a company asset. For a wallet engineer the stakes ran higher still, because the machine was a trusted development endpoint surrounded by credentials, tooling, and access worth billions. PRESSURE CHOLLIMA did not have to break that boundary. The engineer carried it across, persuaded by a deception built for exactly that purpose. Both are true at once. The lapse was real, and it was engineered.
PRESSURE CHOLLIMA is not improvising. It is a specialized state-sponsored operation built around converting access to cryptocurrency infrastructure into revenue for the regime. The fake company, the live HR interview, the coding assignment, and the patience across four months were not incidental social engineering. They were part of an industrial collection and theft process aimed at the people closest to the systems capable of moving money.
Beyond Cryptography
Binance finally answered the question the earlier reporting could not. The June compromise mapped the people around the wallets. The September interview acquired a foothold security tooling missed. The internal AI system became part of the path deeper into the wallet team. The adversary found a container deployment token, then later used stolen credentials from Engineer A to deploy a container and reach the attack path into wallet signing operations. EIP-7702 then carried compromised authority beyond the withdrawal system Binance was trying to shut down.
This is larger than a story about one engineer running the wrong repository. Modern custody is designed to make private keys extraordinarily difficult to steal. Binance's account shows the other side of that architecture. The people, endpoints, credentials, deployment systems, AI tools, and signing workflows surrounding the keys become part of the security boundary too.
An adversary does not have to break the cryptography if it can inhabit the machinery authorized to invoke it.
PRESSURE CHOLLIMA spent months moving through that machinery until Binance's own systems could produce transactions the blockchain would accept. The alarms worked. The withdrawal freeze worked where Binance still held authority. MPC left no single key to steal. None of those controls could erase permissions already written on-chain.
The cryptography held. The trust around it moved US$6.34 billion.